Blog

  • Best WordPress Website Management Tools for 2027

    Best WordPress Website Management Tools for 2027

    A WordPress website management tool is a dashboard for updating, backing up, monitoring, and logging into many WordPress sites from one place. For 2027, the tools still worth using are MainWP and InfiniteWP if you want a self-hosted setup you run yourself, and hosted platforms such as ManageWP, WP Umbrella, Modular DS, WP Remote, Kadence Central, and The Hub from WPMU DEV or GoDaddy Pro if you prefer a vendor-hosted dashboard. This guide compares those nine, based on what their official sites described in November 2026, and leaves out products that have shut down or that are really hosting or marketing suites.

    What is a WordPress website management tool?

    If you look after more than a handful of WordPress sites, logging into each one to run updates, check backups, or see whether a site is down gets old quickly. A website management tool connects those sites to one dashboard so you can do that work in bulk, watch uptime and security from one screen, and, in many cases, send a client a report of what you did. Used well, these dashboards help you simplify website maintenance without hopping from wp-admin to wp-admin.

    They are not the same thing as managed WordPress hosting, and they are not a substitute for a care plan if you do not want to do the work yourself. The rest of this page is about the dashboards.

    Which WordPress website management tools are worth using in 2027?

    The list below is limited to products that were still actively maintained in late 2026. CMS Commander announced a permanent shutdown in 2026 and no longer sells accounts, so it is not included. Hosting control panels and marketing platforms are out of scope too. Pricing changes often, so each section points to the vendor’s official site rather than quoting a figure that may already be out of date.

    ToolBest forHosted or self-hostedKey features
    MainWPAgencies that want client data to stay on their own serverSelf-hosted plugin (Dashboard + Child)Bulk updates, backups, uptime monitoring, client reports (Pro), unlimited sites with no per-site fee
    ManageWPTeams that want a free hosted dashboard they can extend per siteHostedFree core on unlimited sites, updates, backups, one-click login, paid add-ons billed per site
    The Hub by GoDaddy ProFreelancers and agencies in the GoDaddy ecosystem, including sites hosted elsewhereHostedBulk core, plugin, and theme updates, backups, security and performance checks, uptime monitoring, client reports
    The Hub (WPMU DEV)Agencies that want site management bundled with WPMU DEV’s plugin suiteHostedAutomated updates, offsite backups, uptime alerts, white-label reports, one-click SSO, client billing
    WP RemoteAgencies that want management built around BlogVault backupsHostedUpdates, backups, staging, migrations, security, API and MCP access
    InfiniteWPTeams that want a self-hosted admin panel on their own serverSelf-hosted admin panelBulk management, off-site backups, uptime and security monitoring, client reports
    WP UmbrellaFreelancers and agencies selling WordPress care plansHostedSafe updates with visual regression testing, scheduled backups, monitoring, white-label reports, built-in security
    Kadence CentralKadence users managing a client portfolio from one dashboardHosted dashboard + pluginBulk updates, uptime monitoring, Kadence Backups and Security integrations, white-label reports, client dashboard controls
    Modular DSAgencies that want update-risk scoring and care-plan reports in a hosted dashboardHostedBulk updates, Update Copilot, backups, monitoring, security, client reports, API and MCP

    MainWP

    MainWP is a self-hosted, open-source WordPress management tool. You install the MainWP Dashboard plugin on a WordPress site you control, add the MainWP Child plugin on each site you want to manage, and run updates, backups, and monitoring from that dashboard. Because the dashboard lives on your server, your site list and client history stay in your own WordPress database instead of a vendor’s cloud.

    Official docs and the product site describe bulk updates for plugins, themes, and WordPress core, built-in backups, uptime monitoring, and branded client reports as part of MainWP Pro. MainWP Core is free for unlimited sites, with no per-site fees on Core or Pro. Pro is a paid add-on bundle rather than a per-site plan. Check MainWP’s signup and plans page for current pricing. The project was still shipping dashboard updates in 2026, including MainWP 6.2 in September.

    Choose MainWP if you want to own the dashboard, add as many client sites as you need without a per-site fee, and are comfortable hosting and maintaining that dashboard yourself.

    ManageWP

    ManageWP is a hosted dashboard for monitoring and maintaining WordPress sites at scale. You get a free core on unlimited sites, including updates and a monthly cloud backup, and you can add paid features per site when you need them. Official pricing is billed per website, per add-on, after you use the extras. See ManageWP’s pricing page for the current add-on list.

    ManageWP is a GoDaddy brand. Its privacy policy, revised May 13, 2026, says so clearly. It remains a separate product from The Hub by GoDaddy Pro, which is covered next. If you want a hosted dashboard you can start on for free and extend only on the sites that need more, ManageWP is built for that model.

    The Hub by GoDaddy Pro

    The Hub by GoDaddy Pro is GoDaddy’s current dashboard for web professionals. It replaces the older GoDaddy Pro experience. GoDaddy still publishes a Hub versus Legacy Pro comparison if you have been on the older interface. You can manage client sites from one sign-on, including WordPress sites that are not hosted at GoDaddy.

    Official pages list bulk WordPress core, plugin, and theme updates, backups, security and performance checks, uptime monitoring, and client reports. Some maintenance features are sold as paid add-ons. Check GoDaddy’s Hub pages for current pack details. Use this if you already work in the GoDaddy ecosystem and want one dashboard for client sites, wherever they are hosted. Do not treat it as the same product as ManageWP, even though both sit under GoDaddy.

    The Hub (WPMU DEV)

    The Hub is WPMU DEV’s site management dashboard, not a generic “WPMU DEV” app. From one place you can run automated plugin, theme, and core updates, store offsite backups, get uptime alerts, and send white-label client reports. Official feature lists also include security, performance, and SEO tools from WPMU DEV’s plugin suite, one-click SSO into connected sites, and client billing. You can connect sites hosted at WPMU DEV or elsewhere.

    This is a strong fit if you already want WPMU DEV’s plugins and would rather manage sites, backups, and reports from the same membership. Current plan prices are on WPMU DEV’s pricing page.

    WP Remote

    WP Remote is a hosted WordPress management platform made by BlogVault. The same team builds the backup, security, and performance products that the dashboard can use. Official pages describe connecting sites from one list, running updates (with a backup first), and using BlogVault for incremental offsite backups, staging, and migrations, plus security tools and an API with MCP access for other apps.

    Choose WP Remote if you want management and backups from one vendor, and if BlogVault’s restore-focused backup workflow matters to you. It is the management product in that family, so you do not need a second “BlogVault management” tool. See wpremote.com for current plans.

    InfiniteWP

    InfiniteWP is a self-hosted admin panel for agencies, developers, and freelancers who want to manage, protect, and report on many WordPress sites from their own server. Official positioning covers bulk management, automatic off-site backups, uptime and performance monitoring, security checks, and client reports. You install the admin panel yourself and connect sites with the InfiniteWP client plugin.

    The client plugin was still receiving public updates in 2026; version 1.13.10 was listed on August 19, 2026. Like MainWP, this is a good fit when you want the control panel on infrastructure you run. Check infinitewp.com for current plans and requirements, and make sure you are prepared to host and update the panel.

    WP Umbrella

    WP Umbrella is a hosted platform aimed at freelancers and agencies that sell WordPress care plans. Official pages put updates, backups, monitoring, security, and white-label client reports in one system. Safe Update is described as testing and validating updates before they go live, with visual regression testing and a backup taken first. Monitoring covers downtime, performance, PHP errors, and security events. Security features listed on the site include vulnerability detection, hardening, and two-factor authentication.

    Pricing is per site rather than a flat site-count tier. See WP Umbrella’s pricing page for the current rate and add-ons. Choose it if you want a hosted care-plan workflow and reports you can put in front of a client, without running your own management server.

    Kadence Central

    Kadence Central is the current name for the dashboard formerly known as iThemes Sync, then Solid Central. The WordPress.org plugin, published by Nexcess, was at version 4.0.3 and last updated on August 19, 2026. The older sync.ithemes.com address still tells returning users that iThemes Sync became Solid Central; the product branding is now Kadence.

    Official plugin and product pages describe bulk WordPress, plugin, and theme updates, uptime monitoring, remote login, backups through Kadence Backups, security through Kadence Security, white-label maintenance reports, and a client dashboard you can simplify for site owners. Liquid Web lists Kadence Central as part of the Kadence Elite plan. If you already use Kadence, this is the dashboard that sits with that stack. Confirm current plans on Kadence or Liquid Web before you buy it as a standalone tool.

    Modular DS

    Modular DS is a hosted WordPress management platform for agencies and freelancers. Official pages list bulk updates for plugins, themes, and WordPress core, scheduled backups and restores, uptime and security monitoring, and automated client reports. Update Copilot is their scoring system for how risky a pending plugin update is likely to be. The company also documents an MCP server for AI assistants and a public API.

    Modular DS uses subscription plans with a fixed price and overages, rather than a purely per-site or per-add-on model. Official materials described a 14-day trial when we checked in November 2026; confirm details on modulards.com. It is a solid option if you want a current hosted dashboard with care-plan reporting and some update-risk guidance built in.

    When is a management dashboard not enough?

    A dashboard is the right choice when you, or your team, will actually run the updates, backups, and monitoring. It will not fix a broken checkout, clean a hacked site, or write the monthly report unless someone still does that work. If you would rather have a team handle the care plan, Infyways offers WordPress maintenance services for site owners and agencies who want that work done for them.

    How should you choose a WordPress website management tool?

    Start with where the dashboard should live. Self-hosted tools (MainWP, InfiniteWP) keep client data on a server you control, and you are responsible for that server. Hosted tools put the dashboard in the vendor’s cloud, which is usually faster to set up and easier to hand to a teammate.

    Then look at the pricing model, not just the first number you see. Some products are free for unlimited sites and charge for add-ons. Some charge per site. Some sell one membership that also includes a plugin suite. Open the official pricing page on the day you decide, because the figures on older blog posts, including earlier versions of this one, go stale.

    If you sell care plans, check white-label reports, client dashboards, and whether backups can be restored, not only created. If updates have burned you before, look for staging, rollback, or pre-update testing, and read how the vendor describes that flow. Finally, confirm the product is still being updated. A polished homepage is not the same thing as a changelog from the past year.

    Also consider Automattic for Agencies

    Automattic for Agencies is a free-to-join partner program, not a standalone management SaaS in the same sense as MainWP or WP Umbrella. Official pages describe a portal with a sites dashboard for updates, licenses, and client billing. Sites can be connected with Jetpack or the Automattic for Agencies plugin, and the program also offers discounts and commissions on Automattic products such as WordPress.com, Pressable, WooCommerce, and Jetpack. You do not have to host with Automattic to join. It is worth a look if you already work in that stack and want those sites, licenses, and referrals in one place.

    WordPress website management tools in 2027

    In 2027, a WordPress website management tool is still the practical way to look after many sites without living in wp-admin. If you want to host the dashboard yourself, start with MainWP or InfiniteWP. If you want a vendor-hosted platform, ManageWP, The Hub by GoDaddy Pro, The Hub from WPMU DEV, WP Remote, WP Umbrella, Kadence Central, and Modular DS are the ones still being maintained. Skip tools that have already shut down, and check each vendor’s current pricing and changelog before you commit.
  • Joomla Admin Dashboard Is Slow

    Joomla Admin Dashboard Is Slow

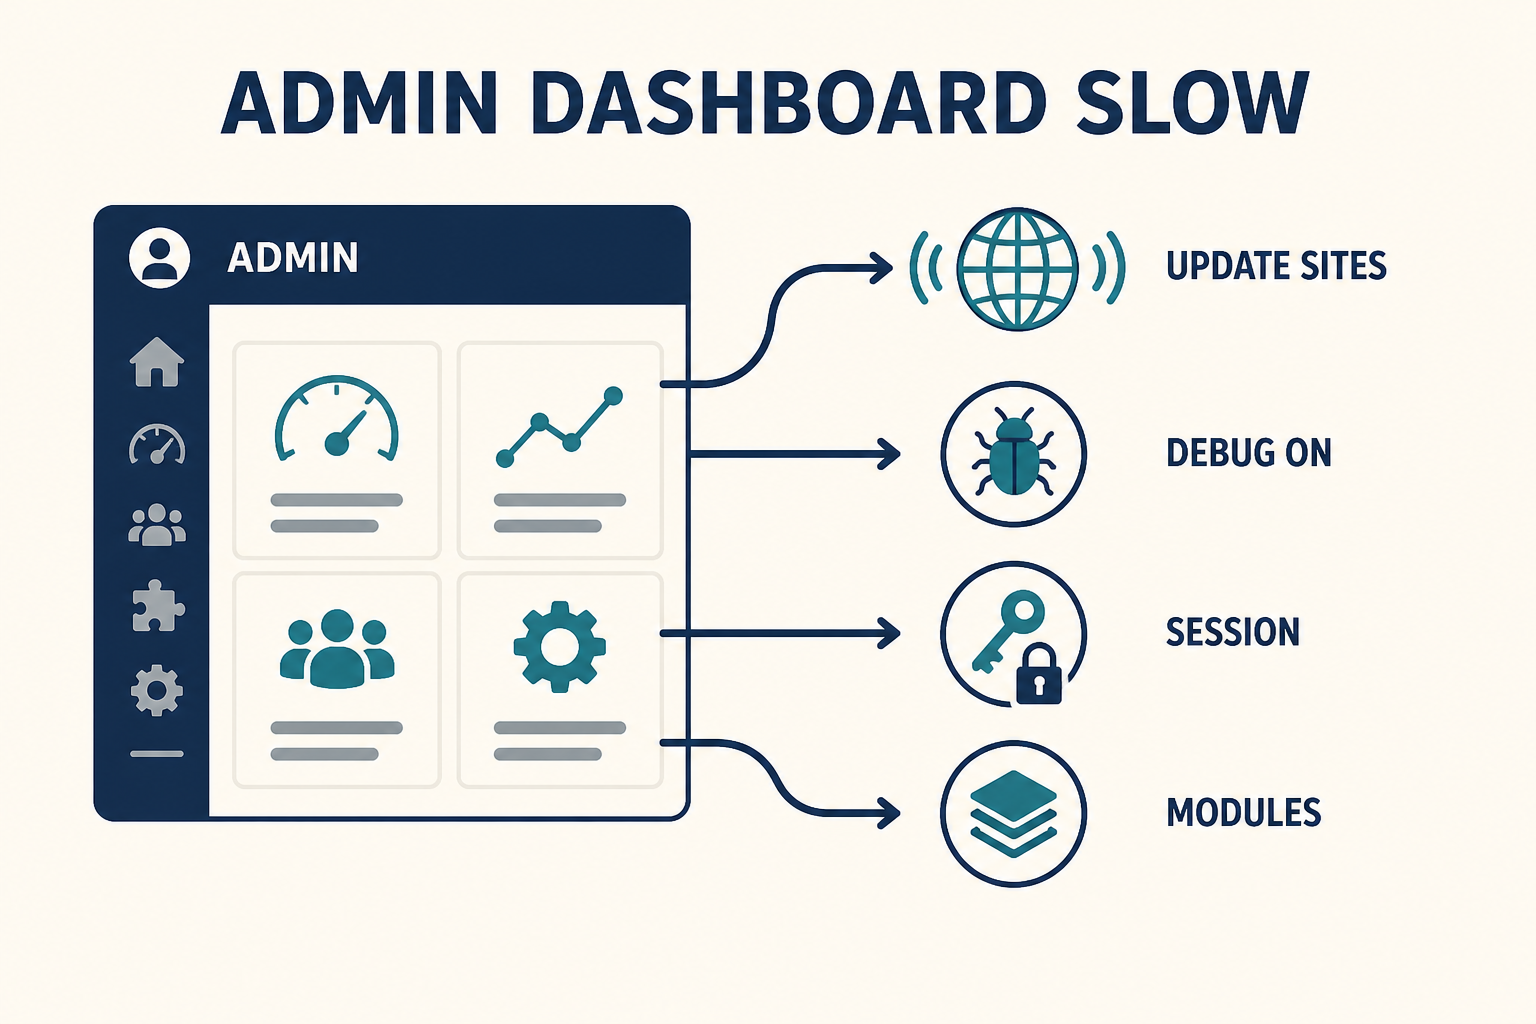
    A slow Joomla administrator is usually update-site HTTP pings, Debug System left on, a locking session handler, too many modules on the Home Dashboard, or a long chain of enabled administrator plugins. It is not the same problem as a slow public site. Atum (the default admin template) is rarely the root cause. The Home Dashboard and com_installer talk to the network. The public Page Cache plugin does not save you here, because it is for guest HTML on the site, not for /administrator/.

    Joomla 4, 5, and 6 paint the control panel with administrator modules. Sample data, backup dashboards, and extension “cpanels” add more tiles. Each tile is work. Separately, the installer update finder (com_installer / Joomla Update) contacts update sites. Dead or slow vendor URLs sit there until PHP times out. That matches what people see as “Checking extensions…” hanging on the dashboard. Core discussed this class of delay when update checks moved to AJAX on the control panel (joomla-cms discussion of update checks): expired update cache means one HTTP call per update server.

    Filesystem PHP sessions can also serialise admin clicks (exclusive lock on the session file until the request ends). That is PHP behaviour, and it shows up with multiple admin tabs. Joomla’s own tracker has pointed people at the Database session handler when Filesystem locking bites (session start / Filesystem). Test handler changes on staging after a backup.

    Administrator slowness: update pings, dashboard modules, debug, session

    Public cache will not fix /administrator/. Look at update sites, Home Dashboard modules, Debug System, and the session handler.

    What you will learn

    • Why Atum is usually innocent
    • How update sites and com_installer stall the dashboard
    • That unpublished modules and disabled plugins do not run (and what still does)
    • How Debug System makes every admin page heavier
    • How to try Database vs Filesystem sessions without guessing on production
    • How this differs from a slow Joomla front end

    Admin slow vs site slow

    Where it hurts Typical causes Not the first lever
    Home Dashboard / every admin view Update site pings, dashboard modules, debug, session locks, admin plugins System – Page Cache, Cloudflare HTML cache
    Public articles only Images, cache off, TTFB, site plugins Uninstalling administrator modules
    Both Host CPU, PHP version, Debug System Yes, disk “Install a new admin template first”

    If the public site is also slow, run the front-end diagnosis in parallel. Do not skip this article because you already turned on Conservative cache. That setting does not cache the administrator UI the way people hope.

    Step 1: Confirm it is administrator, not the whole origin

    Open a public URL logged out. If that is fast and /administrator/index.php is not, stay here. In the browser Network panel on the dashboard, watch:

    • The document TTFB for administrator/index.php
    • XHR/fetch calls to Joomla Update and installer update find (option=com_joomlaupdate, option=com_installer with task=update.find)
    • Long-pending requests to third-party hosts (vendor update XML)

    If those installer calls sit in pending for many seconds, you have an update-site problem until proven otherwise. If the document itself is slow with no update XHR, look at debug, sessions, and PHP.

    Use staging for experiments. Take a backup before you disable update sites or switch session handlers.

    Step 2: Audit update sites (com_installer), not the template

    Atum is the core administrator template. A slow dashboard on stock Atum is almost never “pick a new admin theme.” Third-party admin templates can add JS, but start with installer traffic.

    System → Install → Update Sites (Joomla 4+ System dashboard: Install → Update Sites). You will see one row per extension update server, plus Joomla core.

    What you find What to do
    URLs for extensions you uninstalled years ago Remove or disable those update sites
    A vendor domain that times out in the browser Disable that site. Contact the vendor or replace the extension
    Dozens of sites after a “template club” history Disable unused ones. Core Joomla update site stays
    Dashboard fast after they are disabled You confirmed the ping tax

    Then System → Update → Extensions (or Installer Update) and use Check for Updates once. If that screen is slow but Content → Articles is fine, the diagnosis is still update HTTP, not “Joomla admin is generally broken.”

    Installed extensions live under administrator/components/, plugins/, modules/, components/. A crowded extensions tree means more update sites if those extensions registered one. Uninstall what you do not use (backup first). Unpublishing a module does not remove its update site. Disabling a plugin stops it running. It may still have an update site until you clean Update Sites.

    Do not disable the Joomla core update site to “make admin fast.” You need core security releases.

    Step 3: Cut Home Dashboard modules (the administrator cpanel)

    The Joomla 4+ Home Dashboard is a module chrome. Extra “cpanel” tiles from backup tools, documentation, and sample data all load on that view.

    System → Manage → Administrator Modules (client: Administrator). Unpublish tiles you do not need on the Home Dashboard. Unpublished administrator modules do not render. That is the correct way to slim the cpanel.

    Do not confuse this with Site modules. Unpublishing a site footer module will not speed /administrator/.

    Sample data packs are a frequent source of extra admin modules. If you installed sample data on a real site, remove the sample dashboard modules you do not use.

    Step 4: Turn off Debug System on production

    System → Global Configuration → System: Debug System = No for live administrator work. Server tab: Error Reporting = System Default (not Maximum or Development) on production.

    Debug System Yes was the right move for a white screen. Left on, it prints query lists and debug chrome on administrator pages. That is extra work every click. It is a common “we fixed the outage and now admin is awful” leftover.

    Step 5: Test the session handler, then enabled plugins

    System → Global Configuration → System, Session section: Session Handler. Common options you will actually see: PHP / Filesystem-style, Database, and Redis when the extension and server exist. Exact labels follow your Joomla version.

    Filesystem (PHP files) can lock: one slow admin AJAX holds the session file, other tabs wait. Database is the documented alternative when that happens. Change this on staging first. Changing session handler logs people out (new store). Backup configuration.php and the database.

    If sessions are fine and update sites are clean:

    1. List enabled plugins (System → Manage → Plugins). Sort by Status.
    2. Disabled plugins do not execute. You do not need to hunt unpublished plugins for CPU.
    3. Enabled system plugins still run on administrator requests when they subscribe to those events. Temporarily disable non-core ones on staging and retest a heavy screen (Extension Manage, Module list).

    A huge plugins/ folder of disabled leftovers is disk clutter and update-site clutter. It is not per-request PHP unless something is still enabled.

    PHP version still matters. Joomla 5 wants 8.1+; Joomla 6 wants 8.3+. Admin on an undersized PHP worker pool feels like “Joomla is slow” when the origin is queued. That is hosting, same as the front end. Recipe overlap: speed up Joomla for origin capacity, upgrade if the stack is ancient.

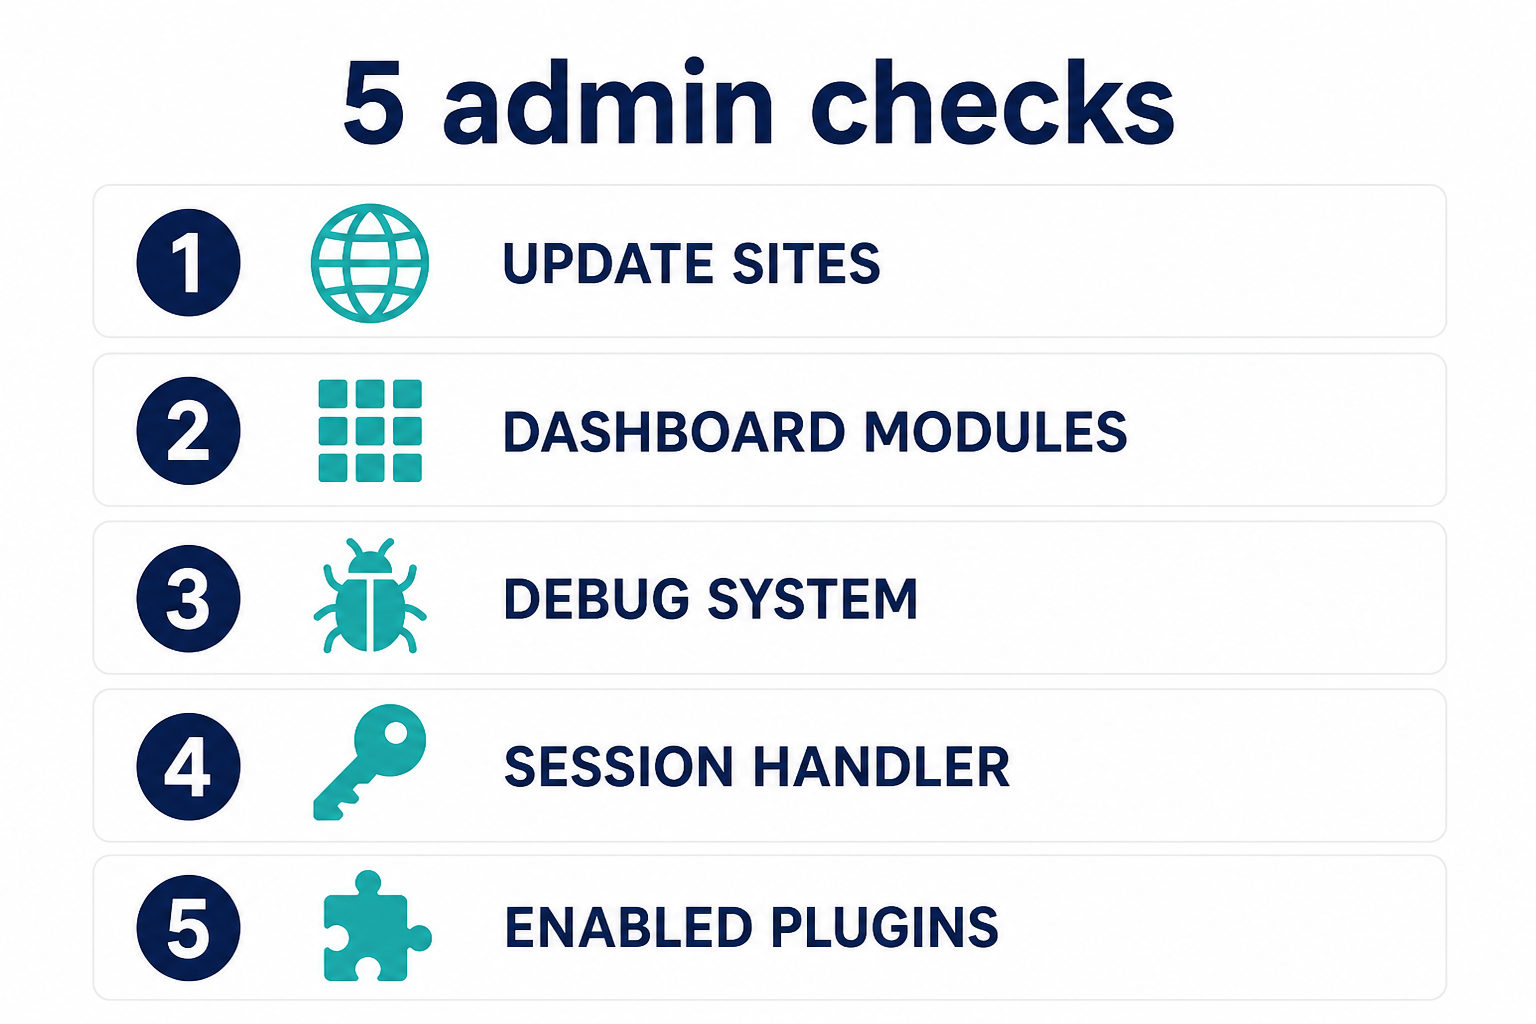
    Five admin checks: update sites, dashboard modules, debug, session, enabled plugins

    Installer pings first. Then cpanel modules. Then debug. Then session handler. Then enabled plugins.

    Key takeaways

    1. Slow /administrator/ is not fixed by System – Page Cache or Cloudflare HTML cache.
    2. Atum is the default admin template. Update sites and dashboard modules are likelier than a template swap.
    3. com_installer / Joomla Update will wait on every live update site. Disable dead vendor URLs.
    4. Unpublished administrator modules do not render. Disabled plugins do not run. Enabled leftovers and leftover update sites still cost you.
    5. Debug System Yes belongs off on production after you finish an outage.
    6. Filesystem sessions can lock multi-tab admin. Try Database on staging. Expect a log-out.
    7. If the public site is also slow, diagnose it separately.

    Related Joomla troubleshooting

    Frequently asked questions

    Why is the Joomla admin dashboard slow when the site is fast?

    The administrator does not use guest Page Cache. The Home Dashboard loads administrator modules and often waits on update-site HTTP. The public site can be cached at the edge while /administrator/ still talks to PHP, the database, and vendor URLs.

    Do unpublished extensions still load in the administrator?

    Unpublished modules do not render. Disabled plugins do not run. Extensions that are still installed can still have Update Sites, and enabled plugins still run. Clean Update Sites and uninstall what you do not need. Do not assume unpublished equals gone.

    Is Atum making my Joomla 4, 5, or 6 admin slow?

    Usually no. Atum is core. Profile the dashboard network tab for installer XHR before you buy an admin template. A third-party admin template can add its own cost, but it is not the first check.

    How do update sites slow com_installer?

    Check for Updates requests each update server whose cache expired. One dead host can stall the dashboard or the update view until PHP gives up. Disable that row under Update Sites and retest.

    Should I enable Debug System to find admin slowness?

    Briefly, on staging, if you need query times. On production it makes every page heavier. For update-site stalls, the Network panel is the clearer tool.

    Will changing session handler to Database speed up admin?

    It can, when Filesystem session locks are the bottleneck (many tabs, long requests). It is not a universal accelerator. Test on staging. You will need to log in again.

    Does Cloudflare cache the Joomla administrator?

    You should not cache /administrator/ at the CDN. If someone did, you get stale admin HTML and odd logins, not a speed win. Bypass admin in Cloudflare page rules. Public speed is the front-end article.

    Conclusion

    Treat a slow Joomla admin as a control-panel problem: update pings, dashboard modules, debug left on, session locking, enabled plugins. Leave Atum alone until those are clean. Take a backup, use staging for session and plugin tests, and keep the core update site enabled.

    If you want someone else to keep update sites and PHP current, that is Joomla support and maintenance.

  • Why Is My Joomla Website Slow?

    Why Is My Joomla Website Slow?

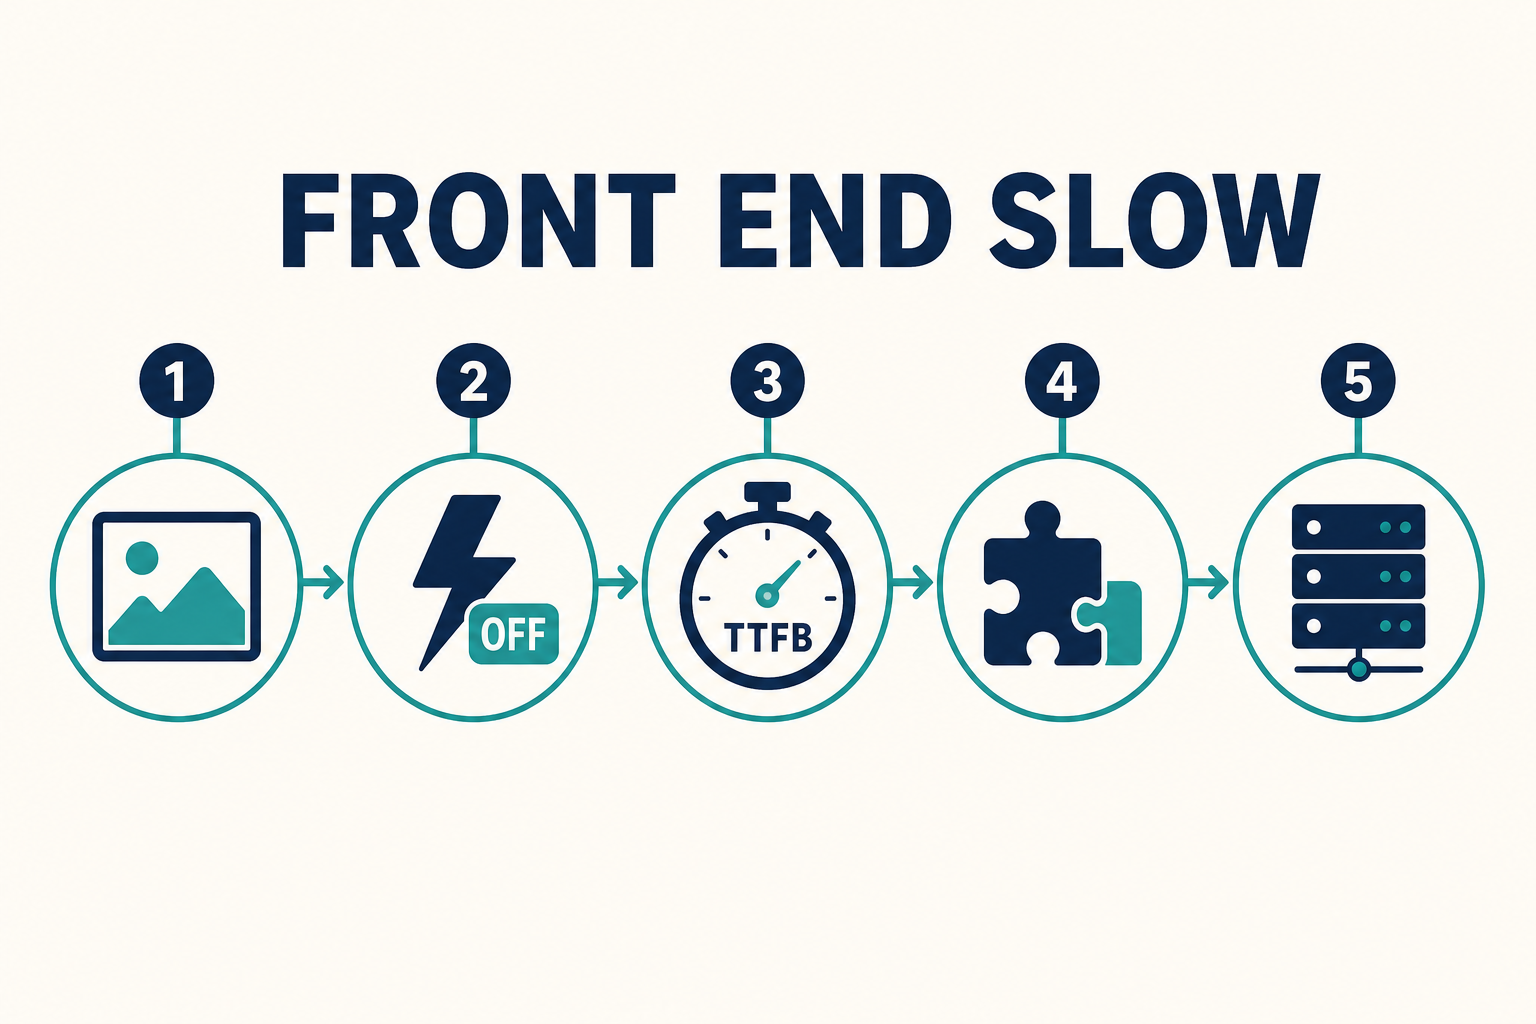
    A slow Joomla front end is usually oversized images, cache left off, a high Time to First Byte (TTFB), heavy extensions, or hosting that cannot hold PHP and MySQL at the same time. Diagnose those causes here. When you know which layer is slow, follow the fix list in How to speed up a Joomla website. This article is the checklist. That article is the recipe. It is not a white-screen outage, and it is not a slow administrator (that is a different pipeline).

    TTFB is the wait before the first byte of HTML arrives. If that is already hundreds of milliseconds to seconds, compressing CSS later will not save you. If TTFB is fine and the page still crawls, look at image bytes and third-party JavaScript. Joomla cache (Conservative / Progressive, Cache Handler, System – Page Cache) sits in the middle: off means every guest pays full PHP and SQL; on means you must still watch freshness (separate posts).

    Official cache behaviour: Joomla Cache documentation and the programmer notes on caching views and modules. PHP floors: Joomla 4 / 5 / 6 technical requirements (Joomla 5.4, Joomla 6). Recommended PHP memory is at least 256MB. That is a floor, not a speed guarantee.

    Front-end slowness stacks: images, cache, TTFB, extensions, hosting

    Measure TTFB first. Then weigh image transfer. Then check whether Joomla cache and Page Cache are even on for guests.

    What you will learn

    • How to split “slow HTML” (TTFB) from “slow assets” (images, JS, CSS)
    • What “cache off” actually means in Global Configuration vs the Page Cache plugin
    • Why huge images dominate front-end time even on a tuned PHP box
    • How to spot an extension tax without guessing
    • When hosting (CPU, I/O, PHP workers, distance to DB) is the real cause
    • Which Infyways guide to open once you know the cause

    Front end vs administrator vs down

    Symptom Article
    Public pages take seconds, admin is fine This checklist, then speed up Joomla
    /administrator/ crawls, public site is acceptable Joomla admin dashboard is slow
    White screen, 500, or error page Joomla website suddenly stopped working
    Page loads fast but shows yesterday’s article Joomla cache showing old content

    Do not tune cache on production as your first experiment if you have never taken a backup. Use staging for Progressive cache and for turning Page Cache on.

    Step 1: Measure TTFB and what the browser actually downloads

    Open the public URL in a private window while logged out. Logged-in users skip the System – Page Cache plugin by design (it serves guests only). If you test while logged in, you will call the site “uncacheable” when guests would have been fine.

    In the browser Network panel:

    1. Reload with cache disabled (or hard refresh once to see uncached assets, then a second load for repeat-view).
    2. Note the document request: status, waiting (TTFB), total time.
    3. Sort by size. Note images, then JS, then CSS.
    4. Note third-party hosts (fonts, tags, chat, maps). Those are not Joomla cache.

    If the HTML document’s TTFB is already slow, stop blaming Cassiopeia’s CSS. Work the server/PHP/SQL/extension path. If TTFB is short and a 3 MB hero PNG is 80% of the waterline, that is an image problem. Joomla Media stores illustrations under images/ (not the media/ folder used for extension JS/CSS). Docs: Managing Media.

    Record three URLs: home, a heavy article, a category blog. One slow template position can hide on the home page only.

    Step 2: Check whether Joomla cache is off

    System → Global Configuration → System (Cache Settings):

    Setting What it does on the front end
    System Cache OFF No conservative/progressive view and module cache. Every guest rebuilds those pieces.
    ON – Conservative caching Views and modules can cache. Per-module Advanced tab can set Use Global or No caching. Default path for most sites.
    ON – Progressive caching More aggressive module caching. Module “No caching” does not protect guests the way people expect. Test on staging.
    Cache Handler File (default, cache/ and administrator/cache/), or APCu / Memcached / Redis when those PHP extensions and servers exist.
    Cache Time Minutes. Default in core docs is 15.

    Full page HTML is not this dropdown. That is the System – Page Cache plugin: System → Manage → Plugins, find System – Page Cache, enable it. Official Cache doc: enable it under Plugins; it keeps serving until Cache Time expires. It is the fastest layer and the least flexible. Leave it off on staging until you exclude login, cart, and forms.

    Cloudflare (or another CDN) is yet another layer in front of Joomla. Cache off in Joomla plus Cloudflare “cache everything” is a freshness problem. Cache off in Joomla plus Cloudflare bypass is a speed problem. Do not mix the two diagnoses.

    If System Cache is OFF and Page Cache is disabled, you have a cause. The recipe to turn them on safely is in speed up Joomla, not here. If they are ON and the site is still slow, cache was not the bottleneck. Keep going.

    Step 3: Weigh images and media

    Front-end slowness is often bytes, not PHP. Check:

    • Full-width photos uploaded at camera resolution (several megabytes each)
    • PNG used where JPEG or WebP would do for photographs
    • Slideshows that load every slide up front
    • Background images in the template CSS pointing at huge files
    • Missing width/height causing layout delay (Core Web Vitals), which is not TTFB but feels “slow”

    Joomla 4+ can resize on insert in Media, but it will not shrink files you pasted as raw URLs in a custom HTML module. Template folders after a switch can also leave you loading two image trees. Broken images are a different article: Joomla images not loading. Here the files load. They are just too big.

    Do not invent a compression ratio. Look at the Network size column. If one image is larger than the HTML, CSS, and JS combined, that is the first front-end fix in the speed-up guide.

    Step 4: Count the extension tax

    Every enabled plugin runs on the request types it is subscribed to. Unpublished modules do not render. Disabled plugins (enabled = 0) do not run. Installed-and-forgotten enabled plugins still run. That is the usual surprise.

    On staging (backup first):

    1. Note the TTFB of a logged-out URL.
    2. Temporarily disable non-core system and content plugins you can name (analytics duplicates, old SEF, unused security scanners, leftover editors).
    3. Measure again.

    If TTFB drops, you found a class of cause. Re-enable one by one. Do not disable core plugins as a bundle. Do not do this fishing trip on production.

    Other extension tells:

    • A template that loads many extra JS libraries on every page
    • Chat, heatmap, and A/B snippets in index.php or Custom HTML
    • A page builder adding a large CSS/JS payload to articles that are “just text”

    Core edits to “make it faster” are how sites get stuck. Keep changes in a child template and non-core customisation.

    Step 5: Ask whether hosting can run this PHP and this database

    Hosting is the rest of TTFB when cache is on, images are reasonable, and plugins are few:

    • PHP workers exhausted (queueing)
    • Slow disk for File cache and sessions
    • Database on another host with high latency
    • PHP below the version Joomla recommends (old PHP can be slower and unsupported)
    • Shared neighbours saturating CPU
    • Geographic distance (TTFB includes network)

    Joomla 5 wants PHP 8.1+ (8.3 recommended). Joomla 6 wants PHP 8.3+ (8.4 recommended). Staying on an ancient PHP “because it works” is both a security and a performance dead end. Upgrade path: Joomla upgrade.

    Debug System Yes on production adds query lists and overhead to every page, public and admin. If someone left it on after a white-screen incident, turn it off. Error Reporting Maximum belongs off too.

    Cloudflare can hide origin TTFB for cached HTML (you see the edge). Test with a cache bypass or Cache-Control that misses, or you will think the origin is fast when only the CDN is.

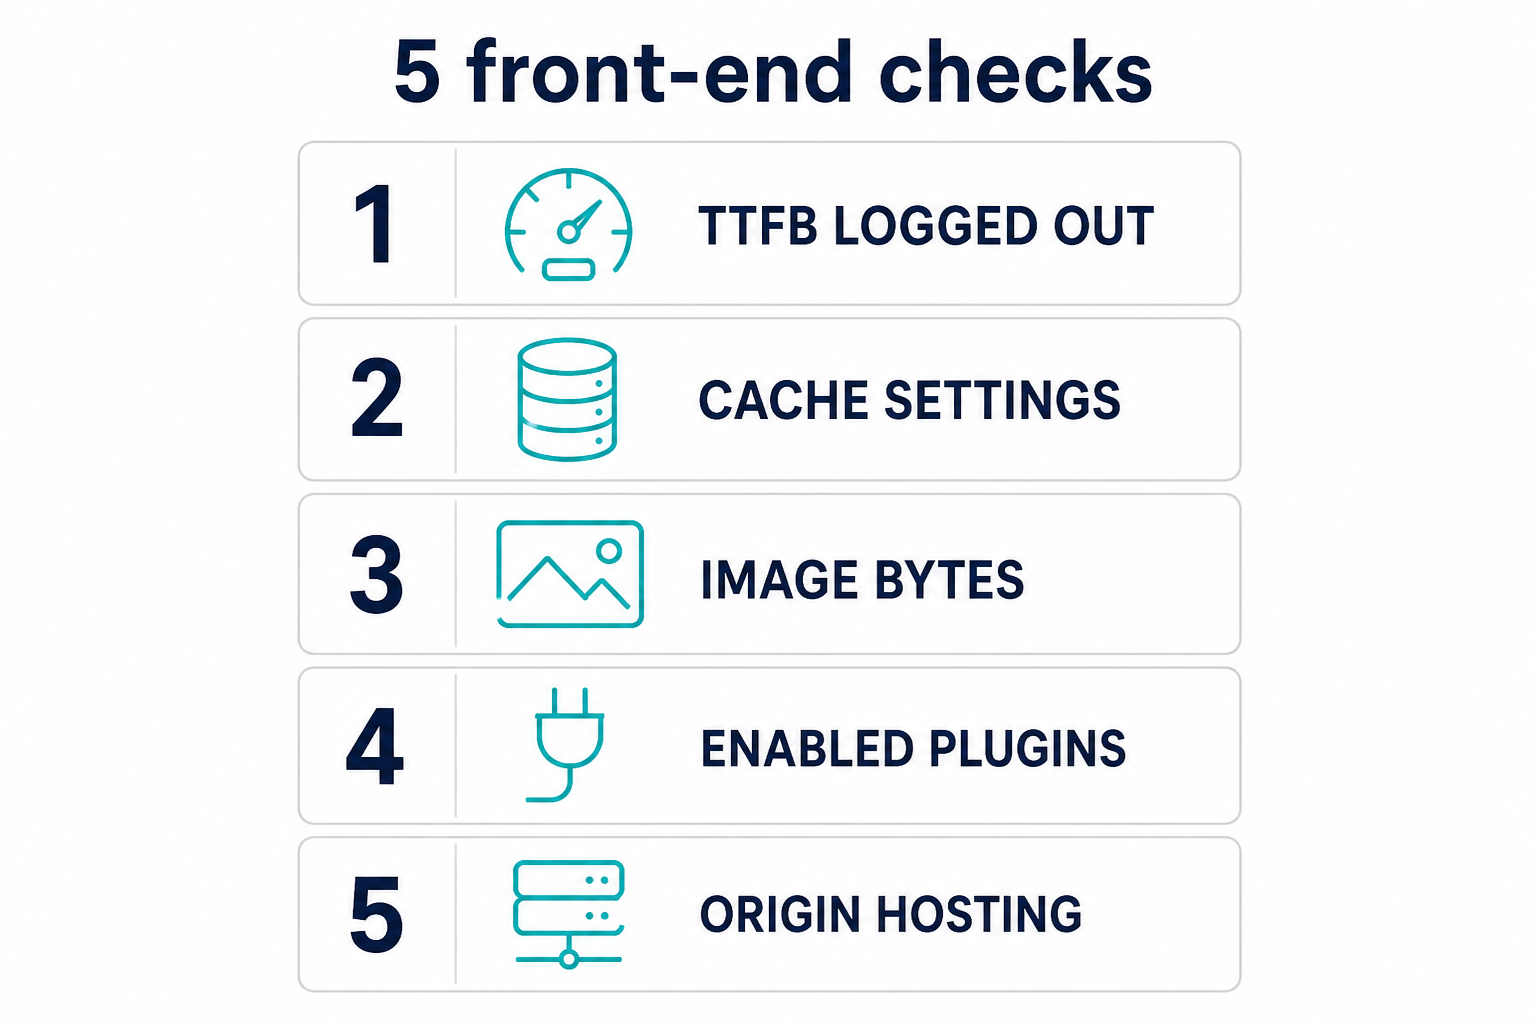
    Five front-end checks: TTFB, cache, images, extensions, hosting

    Logged-out private window. Then TTFB, cache settings, image bytes, enabled plugins, origin hosting.

    After you know the cause

    Open How to speed up a Joomla website and apply the matching section. Do not turn on Progressive caching and Page Cache in the same hour on production without staging. If stale HTML appears afterward, that is cache showing old content. If Clear Cache does not change files, that is cache not clearing.

    Ongoing care (PHP, updates, not leaving debug on): Joomla support and maintenance.

    Key takeaways

    1. Split TTFB (HTML generation) from asset weight (images, JS). They are different jobs.
    2. Test logged out. System – Page Cache does not serve logged-in users.
    3. System Cache OFF plus Page Cache disabled is a real, common cause. Confirm it in Global Configuration and Plugins.
    4. Conservative vs Progressive vs Page Cache vs Cloudflare are different layers. Only one of them may be your bottleneck.
    5. Enabled plugins and bloated media dominate many “Joomla is slow” tickets. Disabled plugins are not the tax. Enabled leftovers are.
    6. Hosting and PHP version set the floor. Cache cannot fix a saturated origin.
    7. Use this article to name the cause. Use the speed-up guide to apply the fix.

    Frequently asked questions

    Why is my Joomla website slow on the front end?

    Most often: large images, Joomla cache and Page Cache left off, high TTFB from PHP/SQL/extensions, or hosting. Measure TTFB and transfer size in a logged-out private window before you change settings.

    Does turning on Joomla cache always make the site fast?

    No. System Cache (Conservative or Progressive) caches views and modules. Whole-page speed for guests needs the System – Page Cache plugin as well, and it still will not shrink a 4 MB photo. Official Cache docs describe those as separate switches.

    Should I test speed while logged into Joomla?

    Not if you care about visitors. Page Cache is guest-only. Logged-in TTFB is a different number. Use a private window signed out for the public diagnosis.

    Is Progressive caching faster than Conservative?

    It is more aggressive on modules. It is also a common source of the wrong module on the wrong page. Start with Conservative on staging. Progressive is not the first diagnosis step.

    Can Cloudflare make Joomla look fast while origin is slow?

    Yes. Edge cache serves old HTML quickly. Bypass cache or check origin logs when you need the real TTFB. Cloudflare will not fix admin, and it will not fix uncached HTML generation.

    Why is the site slow only on mobile?

    Sometimes the same huge images. Sometimes a mobile-only script. Sometimes a host or CDN geo path. Compare the same URL’s document TTFB and image bytes on desktop vs mobile throttling. Do not assume Joomla “detects mobile” unless you enabled Platform Specific Caching.

    Where do I go for the actual speed fixes?

    How to speed up a Joomla website. This page is causes. That page is the how-to.

    Conclusion

    A slow Joomla front end is a measurement problem first. Logged-out TTFB, image bytes, cache switches, enabled plugins, then hosting. Name the layer, then apply the speed-up recipe. Do not flatten all four into “we need Redis” before you have looked at a 3 MB PNG.

  • Joomla Website Suddenly Stopped Working

    Joomla Website Suddenly Stopped Working

    When a Joomla site suddenly stops working, treat it as a last-change problem, not a mystery. A white screen, an HTTP 500, or a red system error page almost always follows a PHP version bump, a bad .htaccess rule, an extension install, or a failed update. Turn error reporting on, read the stack (or error.php), and undo that change on a backup. This is for a site that is down. If the site loads but crawls, use the slow-site diagnosis instead.

    A page that used to render and now returns nothing is PHP dying before Joomla can print HTML. A 500 is the same class of failure with the web server covering the message. Joomla can also show its own error page when the CMS still boots: the system error page (red background) or the template error.php layout. Official recovery starts with Debug System and Error Reporting, then the stack. See the Joomla User Manual: Fatal errors and the Joomla 4 docs mirror J4.x:FatalError.

    Do this on a backup, and test destructive checks (rename .htaccess, disable plugins in the database) on staging first when you have a copy. Production is not the place to discover that mod_rewrite was the only thing keeping URLs alive.

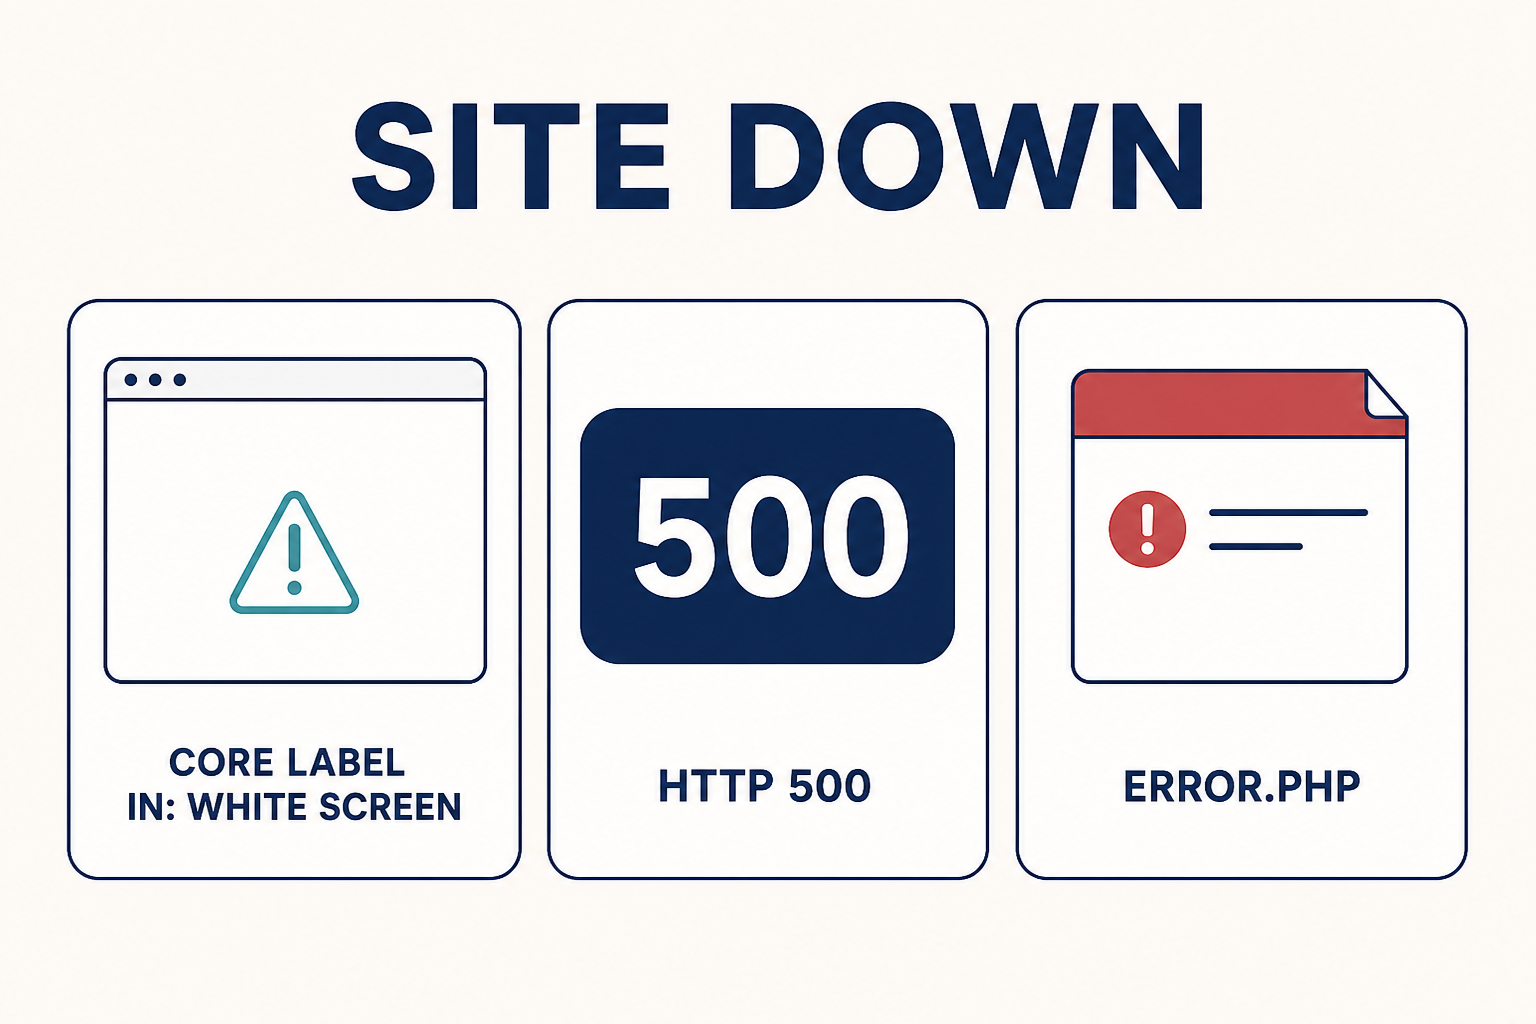
    White screen, HTTP 500, and Joomla error.php are three faces of the same outage

    White screen means PHP failed with display_errors off. 500 is the server wrapping that failure. error.php means Joomla still booted far enough to render an error layout.

    What you will learn

    • How to tell a white screen from a 500 from a Joomla error.php page
    • Why the last change (PHP, .htaccess, extension, update) is the first clue
    • How to turn on Debug System when the administrator is dead
    • Which PHP versions Joomla 4, 5, and 6 actually require
    • How to test .htaccess without burning production
    • How to disable a bad extension from #__extensions if admin will not load
    • What to revert after the site is up

    White screen, 500, and error.php

    What you see What it usually means First move
    Blank white (or empty) page PHP fatal with display_errors off. Joomla never printed output. PHP error log, then Debug System in configuration.php
    HTTP 500 from Apache or nginx Same class of failure. The server hid the PHP message. Same, plus the vhost / host error log
    Red system error page Serious error before the site or admin template rendered Read the message. Enable debug if it is incomplete
    Template-styled error page Error in content code. Joomla used templates/{name}/error.php or templates/system/error.php Read the message and stack. Do not “fix” the crash by rewriting error.php

    Joomla’s error.php is an error layout, not a debugger. Core documents it as independent of the CMS plugin chain: no <jdoc:include />, no modules. Override path: copy templates/system/error.php into the active template. Docs: Custom error pages. If a custom error.php was edited badly, it can make a recoverable error look like a total outage. Compare it to the stock file from the same Joomla package before you chase plugins.

    If the public site is down but /administrator/ still loads, you still have Global Configuration. If both are down, you edit configuration.php over SFTP or the host file manager.

    Step 1: Take a backup and name the last change

    Before you rename files or toggle plugins, snapshot files and the database. Host backup, Akeeba, or both. Write one sentence: “The host moved us to PHP 8.3 last night,” or “We installed extension X,” or “We turned on URL rewriting,” or “We ran a Joomla update.”

    Typical last changes that take a site down:

    • Host PHP upgrade or a MultiPHP selector change
    • Joomla or extension update
    • New plugin, module, or template
    • .htaccess edit (security generator, RewriteBase, custom deny rules)
    • Disk full, inode limit, or a restored backup that missed configuration.php

    If you cannot name a change, check the host’s PHP version history and the Joomla #__extensions enabled / install dates anyway. Hosts often bump PHP without telling you. That is still a last change.

    If the site is on an old Joomla 3 stack that a host just moved to PHP 8, the fix is not a one-line patch in core. Plan a proper Joomla upgrade.

    Step 2: Confirm PHP matches this Joomla version

    Joomla will fatal on a PHP that is too old or on a jump your extensions never saw. Minimums below are from the Joomla project’s technical requirements (Joomla 4.x, 5.x, and 6.x tables). Recommended versions are what the project tests against.

    Joomla PHP minimum PHP recommended (project tables) Source
    4.x 7.2.5 8.2 Hosting setup
    5.x 8.1.0 8.3 Joomla 5.4 technical requirements
    6.x 8.3.0 8.4 Joomla 6 technical requirements

    Required PHP modules listed there include json, simplexml, dom, zlib, gd, and mysqlnd or pdo_mysql (or pdo_pgsql). Recommended memory limit is at least 256MB.

    If administrator still loads: System → Information → System Information (and the PHP Information tab). If it does not: phpinfo in a throwaway file on staging, or the host’s MultiPHP / Select PHP Version screen. Then compare to the table. A Joomla 5 site on PHP 7.4 will not boot. A Joomla 4 site whose third-party plugin is not PHP 8.3-ready will white-screen after a host bump even when core is fine.

    Do not “fix” a PHP mismatch by editing core files. Switch PHP on the host (or staging) to a version that matches both Joomla and the installed extensions. Then update or replace the extension.

    Step 3: Turn on Debug System and Maximum error reporting

    If administrator works: System → Global Configuration. System tab: Debug System = Yes. Server tab: Error Reporting = Maximum. Save. Reload the broken URL. You want a stack trace, not a prettier blank page.

    If administrator is dead, edit configuration.php in the site root. Official steps:

    1. If the file is 444 / read-only, set it to 644 so you can write.
    2. Set $debug to true and $error_reporting to 'maximum'.
    3. Save. Reload the broken URL.

    That wording is from the Fatal errors manual. After you save Global Configuration later, Joomla sets configuration.php back to read-only. That is intended.

    Read the first frame that is not core bootstrap. A path under plugins/, modules/, components/com_something (not com_content / com_users unless you overrode them), or a template html/ override is the usual culprit. The official advice if you can name the extension: disable it. If admin is down, in phpMyAdmin (or equivalent) open #__extensions, find that row, set enabled to 0. Do not disable core Joomla extensions as a fishing trip.

    Also read the PHP error log the host provides. A fatal that happens before Joomla loads configuration.php never appears in the Joomla debug console.

    When you are done, set Debug System back to No and Error Reporting back to System Default. Leaving Maximum on a public site leaks paths.

    Step 4: Test .htaccess on staging, not by deleting production

    Apache 500s after “Use URL Rewriting” or after a security .htaccess generator are common. Joomla ships htaccess.txt. Enabling rewriting is: rename htaccess.txt to .htaccess, then Global Configuration → Site → Use URL Rewriting. Official walkthrough: SEF URLs on Apache. If mod_rewrite is missing, turning rewriting on is a 500. If RewriteBase is wrong for a subdirectory install, same class of failure.

    Do not delete .htaccess on the live site to “see what happens.” Copy the site to staging, or at minimum copy .htaccess to .htaccess.bak and keep that backup off to the side.

    On staging:

    1. Confirm you have the backup copy.
    2. Rename .htaccess to .htaccess.bak (Apache then ignores it).
    3. Reload. If the site returns (often with /index.php/ in URLs), the rules were the problem.
    4. Restore stock rules from the htaccess.txt that matches this Joomla version. Do not paste a Joomla 3 file onto Joomla 5.
    5. If you use a subdirectory, set RewriteBase to that folder as the SEF docs describe.
    6. Only then turn Use URL Rewriting back on and retest.

    Extra Deny / Rewrite blocks from security tools belong in the “last change” list. Test those on staging too. A rule that forbids a PHP file you actually need is a 500, not a permissions mystery.

    nginx does not use .htaccess. If the host is nginx, a rename test proves nothing about rewrite. Use the vhost config and the host error log instead.

    Step 5: Read error.php, then disable the bad extension

    If you get a template-styled error page, open the active template’s error.php only to read what it prints. Compare with templates/system/error.php. You are looking for the exception message and file path, not a design tweak.

    Once the stack names an extension:

    • Administrator working: disable the plugin/module/component there.
    • Administrator dead: #__extensions.enabled = 0 for that row.
    • Override involved: a layout in templates/{template}/html/ can fatal after a Joomla update if the parent view changed. Rename the override folder on staging (do not delete until you know). Safe customisation belongs in a child template, not in core. See customize Joomla without editing core.

    The User Manual also points at the Forum Post Assistant (FPA), a standalone PHP script the Joomla Forum uses. Install it only while debugging, in the site root, then remove it when you clean up. It is not a substitute for a backup.

    Disk space, memory, and script timeouts are on the official cause list too. A full disk makes Joomla look “suddenly dead” after a cache or log spike. Check the host panel before you rewrite configuration.php a third time.

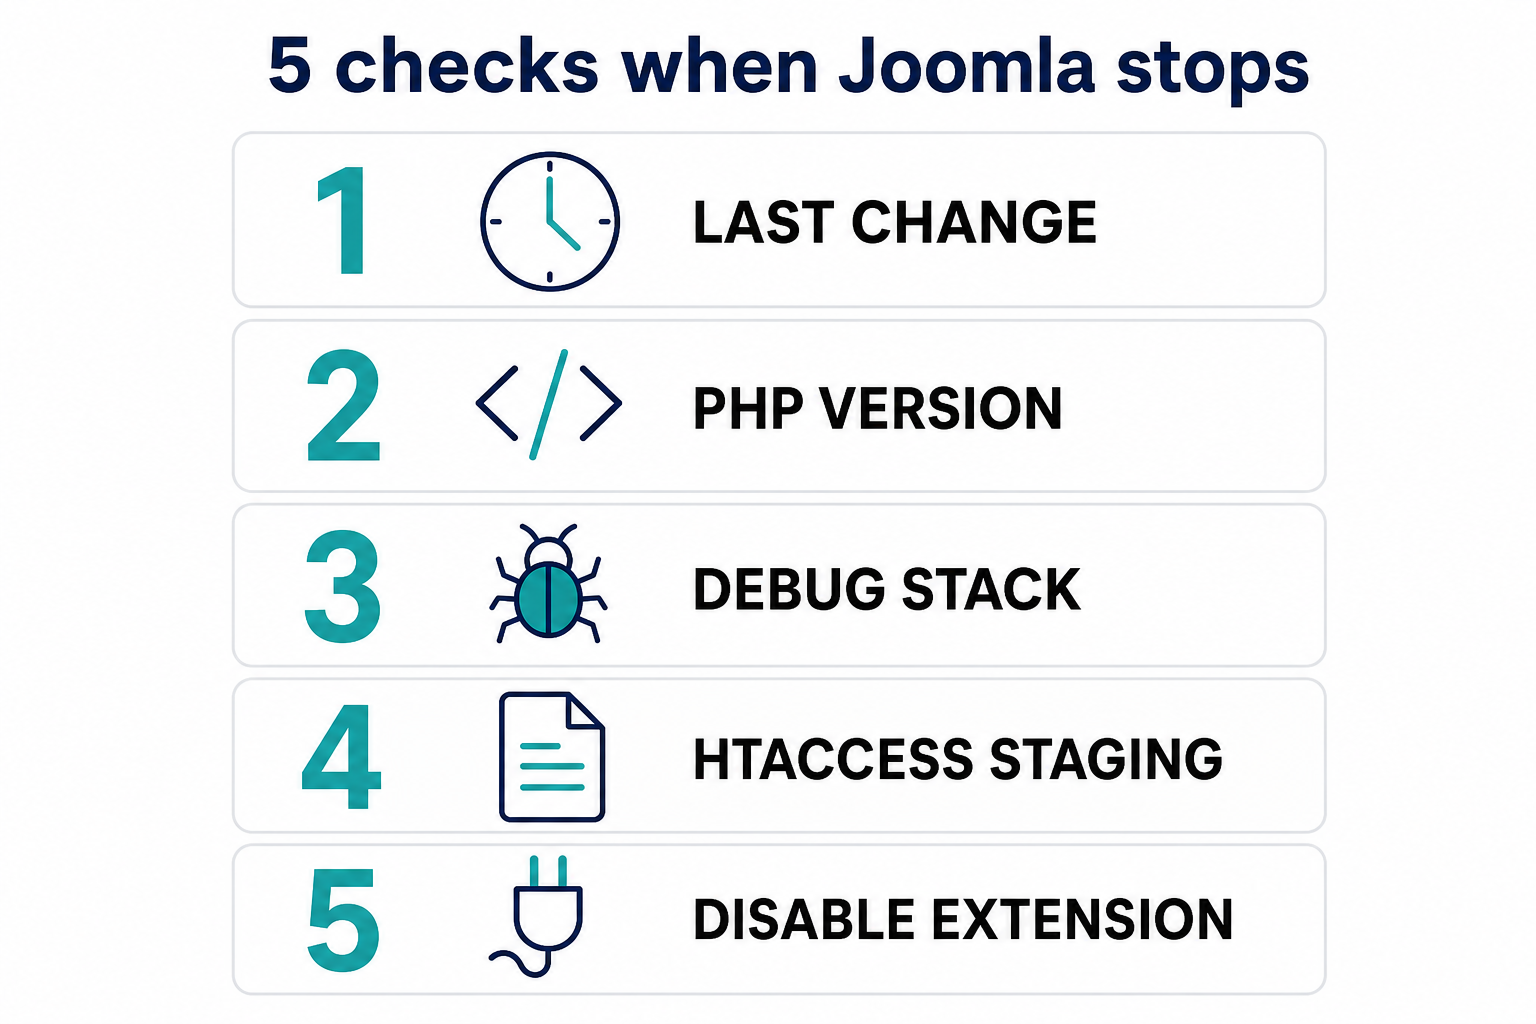
    Five checks when Joomla suddenly stops

    Order: last change, PHP version, debug/stack, .htaccess on staging, then disable the named extension.

    What this article is not

    This is not “why is Joomla slow.” A slow site still responds. Diagnose that in Why is my Joomla website slow and fix it with How to speed up a Joomla website. Admin-only slowness is Joomla admin dashboard is slow.

    If you cannot get a stack and cannot afford more downtime, that is a restore-from-backup moment, then a staged replay of the last change. Joomla support and maintenance is the human version of that loop.

    Key takeaways

    1. A white screen and a 500 are usually the same PHP fatal. error.php means Joomla still booted far enough to render an error layout.
    2. Name the last change first: PHP version, .htaccess, extension, or update.
    3. Match PHP to the official table for Joomla 4, 5, or 6, and to your third-party extensions.
    4. Enable Debug System and Maximum error reporting in Global Configuration, or set $debug and $error_reporting in configuration.php when admin is down.
    5. Test .htaccess by renaming a copy on staging after a backup. Restore from this Joomla version’s htaccess.txt.
    6. Disable the extension named in the stack. Use #__extensions if the administrator will not load. Do not disable core as a guess.
    7. Turn debug off when you are done. Remove FPA. Put configuration.php back to how Global Configuration saves it (read-only).

    Frequently asked questions

    Why is my Joomla site a white screen of death?

    PHP hit a fatal error and display_errors is off, so you get no HTML. Enable Debug System and Maximum error reporting, or set $debug to true and $error_reporting to 'maximum' in configuration.php, then reload and read the stack and the PHP log.

    What does an HTTP 500 mean on Joomla?

    The web server failed to complete the request. On Joomla that is commonly a PHP fatal, a .htaccess / rewrite problem, or a missing mod_rewrite after Use URL Rewriting was enabled. Check the server error log and the same debug steps as a white screen.

    How do I enable Joomla debug if I cannot log in to administrator?

    Edit configuration.php in the site root. Make it writable if it is 444, set $debug to true and $error_reporting to 'maximum', save, reload. That is the official path in the Fatal errors user manual.

    Should I delete .htaccess to fix a 500?

    No. Copy it to .htaccess.bak and test the rename on staging (or after a verified backup). If the site returns, replace rules from this version’s htaccess.txt and fix RewriteBase if Joomla lives in a subdirectory.

    Where is Joomla error.php?

    Stock file: templates/system/error.php. If the active template has its own error.php, Joomla uses that instead. It displays the error. It is not where you patch the bug. See Custom error pages.

    Can a PHP version change take Joomla down overnight?

    Yes. Hosts change MultiPHP without a Joomla update. Joomla 5 needs PHP 8.1 or newer. Joomla 6 needs PHP 8.3 or newer. An old plugin can still fatal on a newer PHP even when core is compatible.

    Do I edit core PHP to get the site back?

    No. Disable the extension, restore the backup, or roll PHP back to a compatible version. Core edits vanish on the next update or block the update. Use overrides and a child template for lasting changes.

    Conclusion

    A Joomla site that “just died” almost never died of boredom. It died of the last change. Backup, name that change, match PHP, turn the errors on, test .htaccess on staging, then disable what the stack names. When the page renders again, turn debug off and keep the backup until the next day behaves.

    If you are still on a Joomla version the host will not run, schedule the upgrade on a clone, not as a panic edit on production.

  • A Closer Look at GPT Image 2.5 on Pollo AI

    A Closer Look at GPT Image 2.5 on Pollo AI

    Sponsored post: This article is a paid guest contribution.

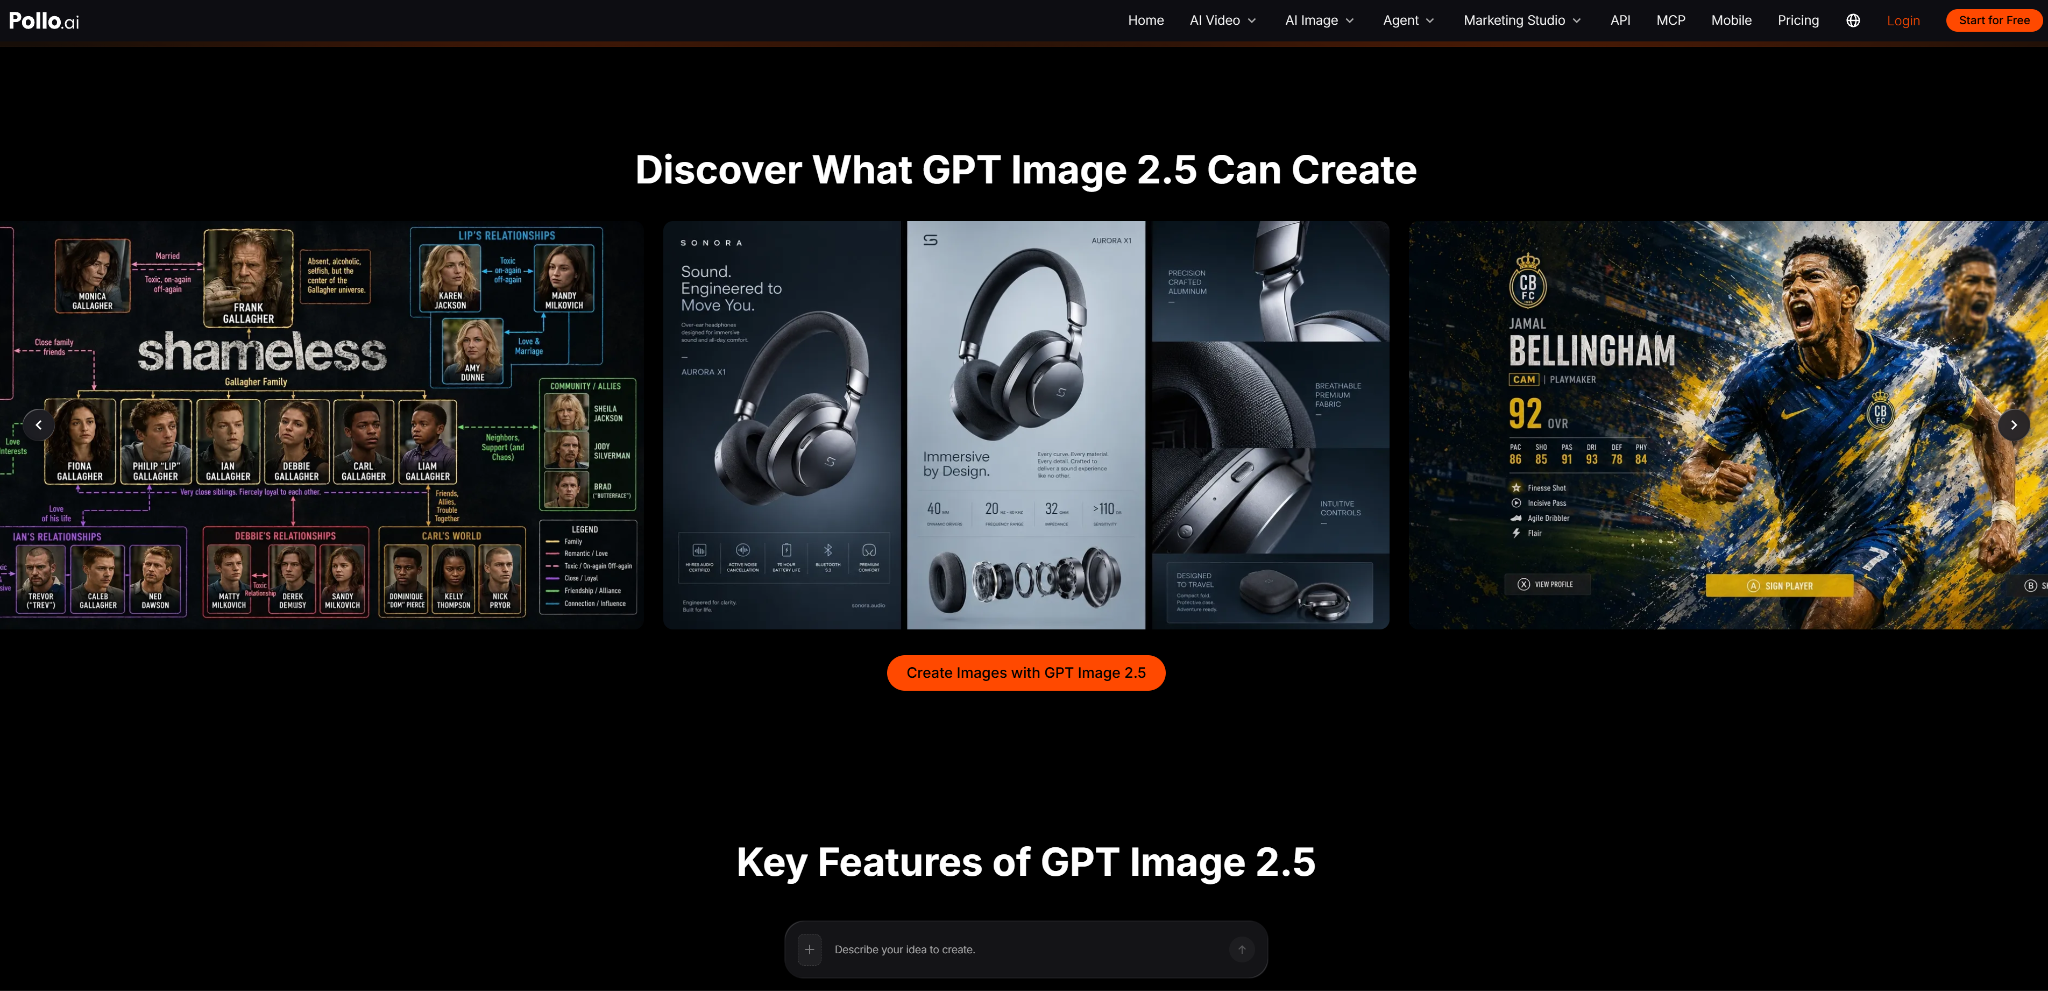
    GPT Image 2.5 is OpenAI's image generation and editing model, built to create realistic visuals, follow detailed prompts, and refine existing images with targeted changes. On Pollo AI, it supports both Text to Image and Image to Image generation.

    This review looks at how GPT Image 2.5 performs on Pollo AI, covering image quality, reference consistency, editing capabilities, speed, and limitations to help readers decide whether it fits their needs.

    What Can GPT Image 2.5 on Pollo AI Do?

    GPT Image 2.5 on Pollo AI

    More Realistic Images

    GPT Image 2.5 on Pollo AI creates images with natural lighting and detailed textures. It can also retain more recognizable features from reference photos, which helps when creating new looks for people, pets, or products.

    For example, you can use a product photo as a reference and try a different setting or visual style. Check details such as logos, labels, and proportions before using the result in a listing or ad.

    Edit Images with Fewer Unwanted Changes

    GPT Image 2.5 is better at making specific edits while keeping the rest of an image intact. On Pollo AI, this can help when you want to change a background, adjust a product detail, or refine an existing visual without starting from scratch.

    Describe the change clearly and mention what should stay the same. The model can still alter other details, so compare the result with the original.

    Generate Images Faster

    Pollo AI says GPT Image 2.5 can generate images in up to 50% less time than Image 2.0. That can be useful when testing several prompts or working through multiple revisions.

    The 50% figure is the maximum claimed improvement, not a guaranteed speed for every image. Actual generation times vary.

    Create Images from Text or Reference Photos

    Pollo AI supports both Text to Image and Image to Image with GPT Image 2.5. Use Text to Image when starting with an idea, or upload a reference photo when the result needs to follow an existing subject or visual direction.

    A useful prompt describes the subject, composition, and style. For edits, be specific about what needs to change—for example, replacing the background while keeping the product's color and shape. This gives the model clearer instructions and makes the output easier to assess.

    How to Use GPT Image 2.5 on Pollo AI

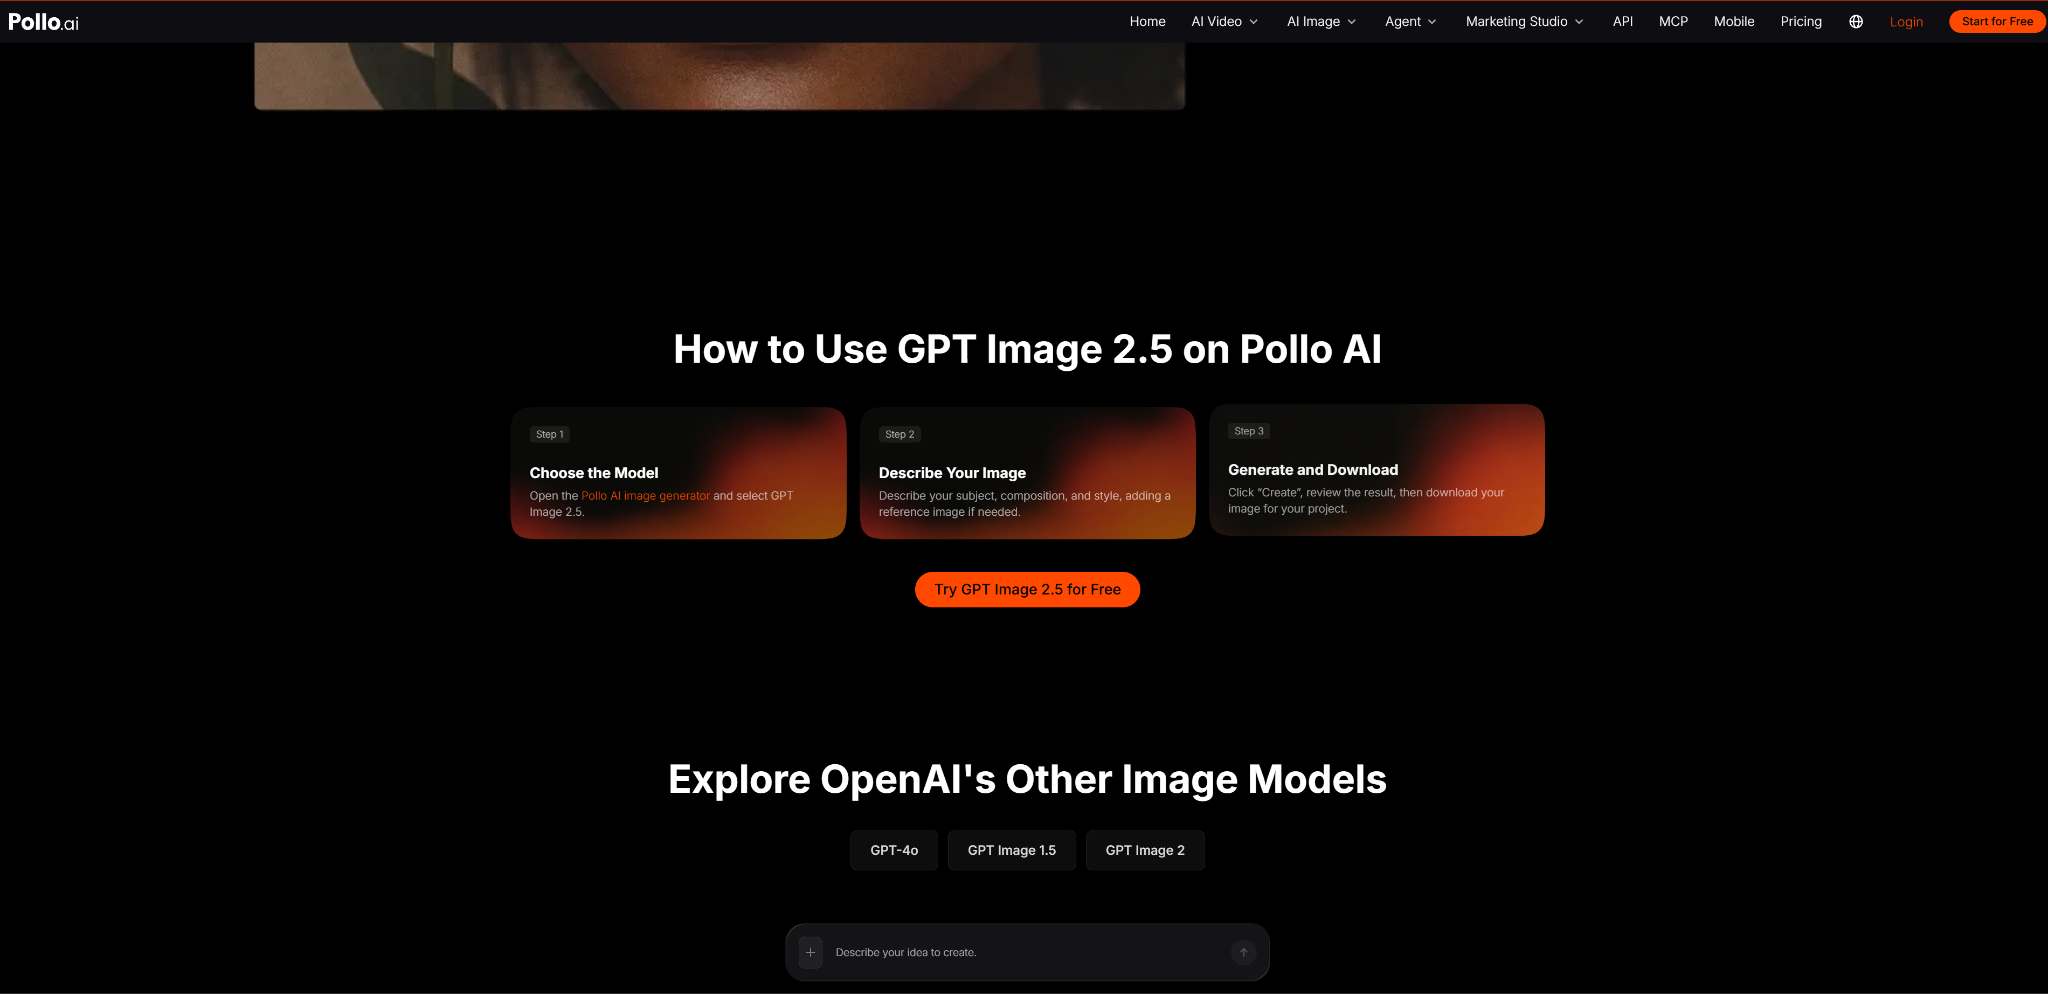
    GPT Image 2.5 on Pollo AI

    Step 1: Open GPT Image 2.5

    Open GPT Image 2.5 at https://pollo.ai/im/gpt-image-2-5. Choose Text to Image for a new image or Image to Image if you want to work from an existing photo.

    Step 2: Write a Prompt or Upload a Reference

    For a new image, describe the subject, setting, composition, and lighting. For example, instead of asking for “a product photo,” specify the product's position, background, and light source.

    If you're editing an existing image, upload it and explain what needs to change. For a product shot, you might request a new background while keeping the product's shape, colors, and label intact.

    Step 3: Generate and Check the Image

    Generate the image and look for details that don't match your prompt. Check faces, product features, text, and composition, especially if the image is intended for an ad or product listing. Small errors can be easy to miss when the overall image looks convincing.

    Step 4: Make Targeted Edits

    If the image is close to what you want, avoid rewriting the entire prompt. Ask for one specific change at a time, such as brightening the background or moving an object, and state which details should stay the same.

    This makes revisions easier to compare, though the model may still change parts of the image you wanted to preserve.

    Step 5: Download and Prepare the Final Image

    Once you're happy with the result, download it and check the full-size version. For commercial use, you may need a separate editor to correct text, fine details, or alignment before publishing.

    How Does GPT Image 2.5 Perform on Pollo AI?

    GPT Image 2.5 is most useful when a project needs more than a single generation. Reference photos help guide the result, while follow-up prompts let users adjust individual details without rebuilding the image from scratch.

    For product visuals, portraits, and campaign graphics, this can save time during revisions. A useful prompt names the exact change and the details that must remain untouched. Even then, check each version rather than assuming earlier details will stay intact.

    The model also supports detailed compositions and text in images, but generated copy and layouts still need proofreading. A visually convincing result is not necessarily ready to publish.

    Pollo AI states that GPT Image 2.5 can generate images in up to 50% less time than Image 2.0. This is the maximum claimed improvement, not a guaranteed generation time; actual speed varies.

    Overall, GPT Image 2.5 is a practical option for reference-based creation and iterative editing. Its improvements can reduce rework, but they do not eliminate the need for prompt adjustments and quality checks.

    Final Take

    GPT Image 2.5 is worth considering for product images, portraits, advertising graphics, and other projects where recognizable subjects and controlled edits matter. For simple images, the difference may be less noticeable; for projects that require several rounds of revision, its editing capabilities may be more useful.

    If you want to see how it handles your own prompts or reference images, try GPT Image 2.5 on Pollo AI with a small test project first. Compare the results with your current workflow, paying attention to subject consistency, edit accuracy, and the amount of rework needed before deciding whether it fits your needs.

  • Strata Files: The Free, Open-Source Finder Alternative That Makes Managing Files on Your Mac Better

    Strata Files: The Free, Open-Source Finder Alternative That Makes Managing Files on Your Mac Better

    Let’s be honest. How many times have you opened Finder on your Mac, searched for a file, waited for results, and wondered why something so basic still feels unnecessarily complicated?

    Apple’s Finder has been around for decades. It does its job, but if you work with hundreds or thousands of files, manage development projects, handle large media libraries, or regularly move files between folders, you might find yourself wishing it could do a little more.

    What if you could have faster search, better file management, detailed disk usage insights, developer-friendly tools and a more powerful browsing experience without paying for another application?

    That’s where Strata Files comes in.

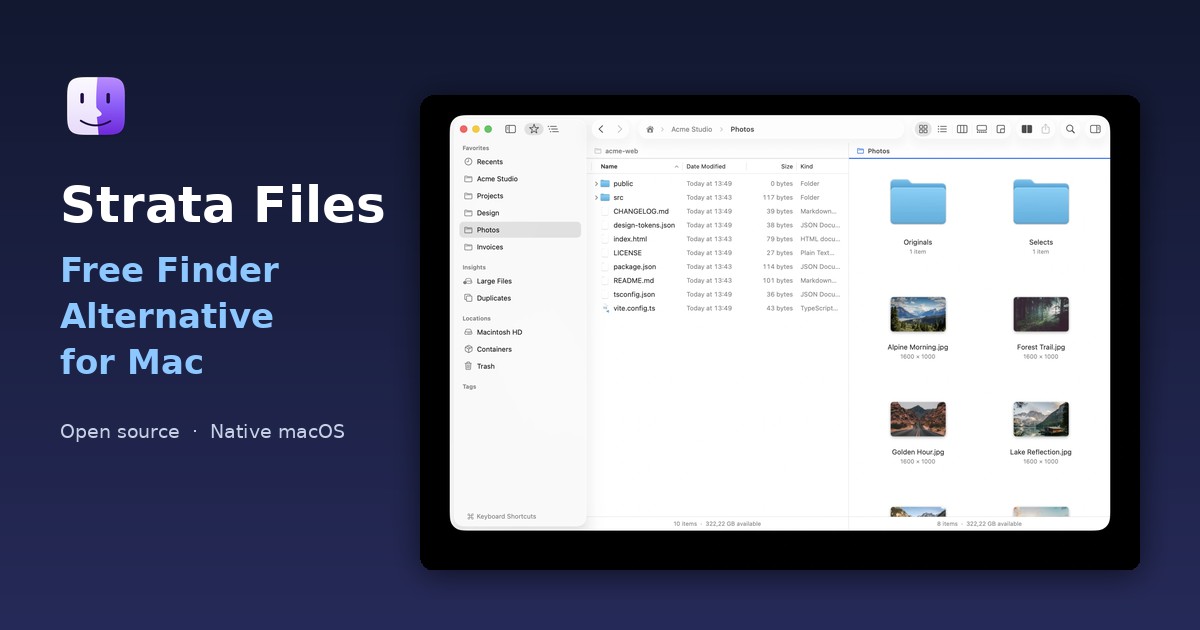
    Strata Files is a free, open-source file manager for macOS that aims to make managing files faster, smarter and more enjoyable. It takes the familiar experience of Finder and adds features that many Mac users have been waiting for.

    And yes, it is completely free.

    What Is Strata Files?

    Strata Files is a native macOS file manager designed as an alternative to Apple’s Finder.

    It combines familiar file management features with powerful capabilities such as instant file search, real-time folder sizes, disk usage visualization, dual-pane browsing, advanced filtering and developer tools.

    But there’s something particularly interesting about Strata Files: it is built entirely using Apple’s native AppKit and Swift technologies.

    There is no Electron, no web views and no unnecessary layers running in the background.

    It is designed specifically for Mac users who want a fast, lightweight and privacy-focused experience.

    Even better, Strata Files is open source under the MIT license. You can download it, use it, inspect its source code and contribute to its development.

    Why Look for a Finder Alternative?

    Finder is convenient, familiar and deeply integrated into macOS. However, convenience doesn’t always mean efficiency.

    Consider a few everyday situations.

    • You want to find every PDF modified last month.
    • Your Mac is running out of storage, but you have no idea which folders are consuming the most space.
    • You need to compare two project folders and move files between them.
    • You want to search for files larger than 1 GB.
    • You work with multiple repositories and frequently navigate between project directories.

    These are relatively simple tasks, but they can become frustrating when your file manager doesn’t provide the right tools.

    Several third-party applications attempt to solve these problems, but some come with paid licenses, subscriptions or additional complexity.

    Strata Files takes a different approach: deliver a powerful Finder alternative that is free and open source.

    7 Reasons to Try Strata Files

    1. Lightning-Fast File Search

    Searching for files shouldn’t feel like waiting in a queue.

    Strata Files indexes files in your home folder and Applications directory, allowing you to search as you type. Once indexing is complete, results can appear in milliseconds, even across millions of files.

    You can search using file names, precise filters or natural language.

    For example:

    • “PDFs from last month”
    • “Videos bigger than 500 MB”
    • ext:swift modified:<7d
    • size:>1gb kind:movie

    You can even save searches and keep them available for later.

    If you regularly work with large collections of documents, images, videos or development files, this feature alone is worth exploring.

    2. Finally Understand Where Your Disk Space Goes

    Running out of storage on your Mac?

    Instead of manually opening folders and checking their properties, Strata Files provides a dedicated Disk Usage view.

    It visualizes folder sizes using a map, making it easier to identify which directories are consuming the most storage.

    You also get dedicated Large Files and Duplicates sections to help identify unnecessary files and reclaim valuable disk space.

    This is particularly useful for developers, designers, photographers and video editors who regularly work with large files.

    3. A Keyboard-First File Management Experience

    If you love keyboard shortcuts, you’ll appreciate this.

    Strata Files includes a command palette that lets you jump between folders, search files and execute commands without constantly reaching for your mouse.

    Some useful shortcuts include:

    Shortcut Action
    Command + K Open command palette
    Command + L Type a path
    Command + 1–5 Switch between views
    Space Quick Look
    Shift + Command + F Open Recents

    You can also filter files within a folder simply by typing.

    The goal is simple: spend less time navigating and more time getting things done.

    4. Five Views and Dual-Pane Browsing

    Different files deserve different ways of viewing them.

    Strata Files supports five viewing modes:

    • Icons
    • List
    • Columns
    • Gallery
    • Disk Usage

    It also includes Dual Pane mode, allowing you to work with two folders side by side.

    Need to copy files from one project to another? Compare folders? Move documents between locations?

    Dual Pane makes these operations much more convenient.

    5. Powerful Features for Developers

    This is where Strata Files becomes particularly interesting.

    Most file managers focus primarily on everyday file operations. Strata Files goes further by offering tools designed for developers.

    You can:

    • See Git status directly on files.
    • View the current Git branch in the path bar.
    • Run project scripts for Node.js, Rust, Swift, Python, Go and other technologies.
    • Preview Markdown, HTML, JSON, CSV and SQLite files.
    • Browse Docker and other container environments.
    • Connect to SFTP servers and S3 buckets.
    • Manage project files and inspect build artifacts.

    For developers who spend most of their working day inside project directories, these features can make file management considerably more efficient.

    6. Privacy Without Compromise

    Privacy is another area where Strata Files stands out.

    Your files are yours. Your file manager shouldn’t need to upload them somewhere else just to help you find them.

    Strata Files runs locally on your Mac.

    There are no accounts to create, no tracking and no cloud-based file indexing. Its search index and history are encrypted on disk, with the encryption key stored in your macOS Keychain.

    Even its document summaries and AI-related features are designed to run locally.

    That’s a meaningful advantage for people working with private documents, business files and development projects.

    7. Completely Free and Open Source

    Here’s perhaps the most interesting part.

    Strata Files is free.

    Not free for seven days. Not free with limited functionality. Not free until you need an essential feature.

    The application is released under the MIT open-source license, and its website lists all its major features as included at no cost.

    You can download it, use it, inspect the source code and contribute to its development.

    For users looking for a free Finder alternative, that’s a compelling proposition.

    Strata Files vs. Apple Finder

    How does it compare with the file manager already installed on your Mac?

    Feature Apple Finder Strata Files
    Native macOS experience Yes Yes
    Advanced instant search Standard search Yes
    Natural-language search Limited Yes
    Real-time folder sizes Limited Yes
    Disk usage visualization No built-in equivalent Yes
    Large files and duplicates Limited Dedicated tools
    Dual-pane browsing No Yes
    Git integration No Yes
    SFTP and S3 No built-in support Yes
    Container browsing No built-in support Yes
    Free Yes Yes
    Open source No Yes

    Strata Files is not necessarily intended to replace every feature of Finder. It is designed to work alongside Finder, giving users another way to manage their files.

    You can even configure supported file-reveal workflows to open Strata instead.

    Is Strata Files Really Free?

    Yes.

    Strata Files is released under the MIT license, and its website currently lists its complete feature set at $0.

    There are no subscription plans or paid feature tiers advertised.

    This includes advanced search, disk usage analysis, dual-pane browsing, developer tools, SFTP, S3, copy history, undo and on-device summaries.

    For anyone searching for a free and open-source Finder alternative, this makes Strata Files worth considering.

    How to Download and Install Strata Files

    Getting started is straightforward.

    Step 1: Visit the official website:

    https://stratafiles.app

    Step 2: Select Download for Mac to access the latest release on GitHub.

    Step 3: Download and install the application.

    Step 4: Follow the initial setup instructions. You can optionally grant Full Disk Access to allow Strata to search and measure files across your Mac.

    You can also install it using Homebrew:

    brew install --cask cristipufu/tap/strata
    

    Important: Strata Files currently requires a Mac with Apple silicon running macOS 26 Tahoe. It is not currently advertised as compatible with Intel Macs or older macOS versions.

    Who Should Use Strata Files?

    Strata Files is particularly interesting for:

    • Developers: Git integration, project inspection, terminal commands and container browsing.
    • Designers: Better file organization, gallery previews and large-file discovery.
    • Content creators: Managing large video, audio and photography libraries.
    • Power users: Keyboard shortcuts, advanced search and dual-pane browsing.
    • Privacy-conscious users: Local processing without accounts or cloud-based file indexing.
    • Open-source enthusiasts: A free application with publicly available source code.

    If you regularly work with files on your Mac, there is a good chance you’ll find something useful here.

    Final Verdict: Is Strata Files Worth Trying?

    A good file manager should make your computer easier to use, not introduce another layer of complexity.

    Strata Files makes an interesting case for itself by combining the familiarity of Finder with features that go considerably further.

    Its fast search, disk usage visualization, dual-pane interface, developer tools and privacy-focused architecture make it more than just another Finder replacement.

    But perhaps its biggest advantage is its pricing.

    You get a native macOS application, an extensive feature set and an MIT open-source license without paying a subscription.

    If you’ve been searching for a Finder alternative that is powerful, private, free and open source, Strata Files deserves a place on your shortlist.

    You don’t have to uninstall Finder or commit to anything. Download it, explore its features and see whether it fits your workflow.

    Ready to give your Mac a better file manager?

    Visit Strata Files and try it for free.


    About Strata Files: Strata Files is a free and open-source native file manager for Apple silicon Macs, built with Swift and AppKit. It offers advanced search, disk usage analysis, dual-pane browsing, developer tools and privacy-focused local processing.

    Official Website: https://stratafiles.app

    Source Code: Available through the official GitHub link on the website.

  • Joomla Extension Installed but Not Working

    Joomla Extension Installed but Not Working

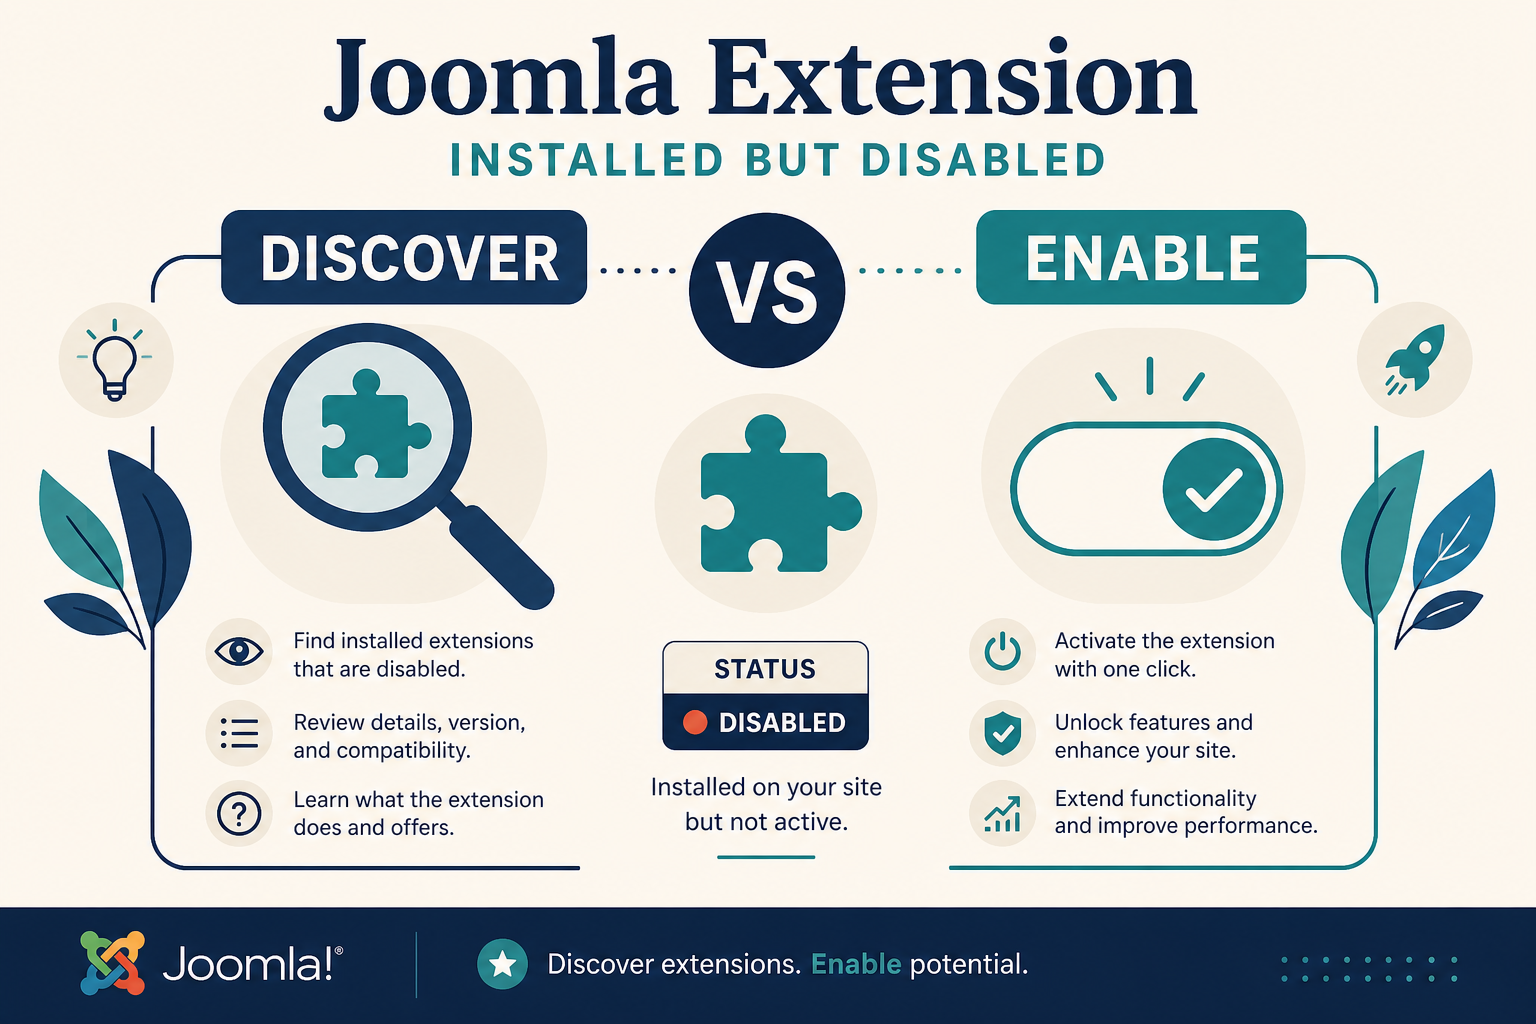
    A Joomla extension is installed but not working when files exist (or a zip succeeded) and the site still has no working feature: the package is undiscovered, the row is disabled, the database schema never ran, PHP is too old or too new, a menu type was never created, or a module instance was never published. “Installed” in the installer message is not the same as enabled, assigned, and given a menu item. This is a readiness checklist, not a 500 hunt and not a two-plugin conflict hunt.

    If the administrator or site is a 500, stop: find which extension causes a 500. If two enabled add-ons fight, use extension conflict. If the zip never finished, stay in System → Install → Extensions and read the installer message. This page assumes the installer said success, or you uploaded files by SFTP, and the feature is still dead.

    Installer success message next to a disabled plugin and no menu item

    A green install is a database row and files. The feature still needs Discover or enable, schema, PHP, a menu type, and often a module you create by hand.

    What you will learn

    • The difference between Upload, Discover, and Enable
    • How to see the extension in System → Manage → Extensions
    • When System → Maintenance → Database (Update Structure) is the real fix
    • How to match PHP version to the extension’s requirements
    • One check for Behaviour – Backward Compatibility on Joomla 5 (not a full compatibility essay)
    • Why a component can install with no menu item type until you create one
    • Why a package’s module is not on the page until you create and assign it

    Official: Installing an extension, Help5.x Discover, Version update, database check.

    Installed, discovered, enabled, configured

    State What is true What you still must do
    Files on disk only You unzipped into components/ or plugins/ Discover then Install
    Installer success #__extensions row exists Enable plugins, create menu, create module
    Enabled plugin enabled = 1 Check ordering, access, and that you enabled the right plugin in a package
    Component enabled Admin menu may show it Create a menu item of that type for the site
    Module type exists You can pick it under New Module New, publish, position, assignment
    Schema out of date Files newer than SQL Maintenance → Database → Update Structure

    Most “not working” tickets are the right-hand column, not a corrupt zip.

    Step 1: Find the row in Manage Extensions

    1. System → Manage → Extensions.
    2. Search the extension name and the com_, mod_, plg_ element if you know it.
    3. Confirm Status (enabled). A lock icon means protected core. Third-party rows should be enableable.
    4. Open the details. Note type (component, module, plugin, package, library, file).

    A package installs several rows. The component can be enabled while the plugin that injects the feature is disabled. Filter by the package name and enable every non-core row the vendor documents.

    If the search is empty, the installer did not register the extension. Either the zip failed silently (host upload limit) or someone copied folders by FTP. Go to Step 2. Do not keep uploading the same zip on top without checking Discover.

    Step 2: Discover is not Enable

    Discover is for files already on the server that Joomla does not have in #__extensions. Official help: Extensions: Discover.

    Use it when:

    • The package was too large for the web uploader, so you extracted into components/com_example, administrator/components/com_example, media/com_example, and language folders as the installing guide describes.
    • A deploy process copied a git checkout of an extension into those paths.

    Then:

    1. System → Install → Discover (some sites label this under Manage → Discover).
    2. Toolbar Discover.
    3. Tick the extension. Install.

    Discover does not turn a disabled plugin on. It creates the row. Then you enable in Manage Extensions or Plugins.

    If Discover finds nothing, the files are in the wrong tree (nested extra folder, or site files only without administrator files). Fix the paths. Do not invent a second copy under tmp/ and expect Joomla to see it.

    Normal small zips should go through System → Install → Extensions (upload). Discover is the exception path.

    Step 3: Enable the plugin (packages hide this)

    System → Plugins. Search the vendor or feature name.

    Many components ship:

    • A system plugin that loads language or routing
    • A content plugin that prints a button or shortcode
    • An actionlog or privacy plugin you can leave off

    If the system plugin is disabled, the component admin screen may open and the site view stays empty. Enable it. Then check Access on any module the package added.

    Installer sample data sometimes creates an unpublished module. Published component + unpublished module = “not working” on the frontend.

    Step 4: Fix the database schema

    If the Home dashboard warns that the database is out of date, or the extension errors about a missing table or column:

    1. System → Maintenance → Database.
    2. If problems are listed, select the extension and Update Structure.

    That replays skipped SQL. It is the documented fix after a partial Joomla or extension update: Version update, database check.

    If Update Structure fails, the extension’s sql/updates files may not match the database engine, or a previous update died. Restore a backup and reinstall on staging. Do not create tables by hand unless the vendor gives you SQL.

    A component that “installed” but never ran install.sql (Discover on incomplete files, or a failed package) will 500 or show empty lists. That can look like “not working.” Check error_log if the view fatals: 500 article.

    Step 5: Match PHP version (and host extensions)

    Open System → System Information (site and PHP tab). Note PHP version.

    Open the extension’s documentation for minimum PHP and maximum tested. Joomla 5 itself needs a current PHP (see technical requirements for the Joomla version you run). An add-on that last shipped for PHP 7.4 will not run on PHP 8.3.

    Also check System → Manage → Warnings and System Information for missing PHP modules (intl, gd, mbstring, zip). The installer may have succeeded while runtime needs curl for an API.

    Host “PHP selector” can differ between the site and CLI cron. A plugin that works in admin and fails on cron is often two PHP versions.

    Step 6: One Joomla 5 compatibility plugin check

    On Joomla 5, core ships Behaviour – Backward Compatibility (plg_behaviour_compat). It loads Joomla 4 class aliases so older extensions can run. Official note: Compatibility plugin.

    Check, do not redesign your stack around it:

    • System → Plugins, search Backward Compatibility or compat.
    • If a Joomla 4-era extension is installed and this plugin is disabled, enable it on a staging copy first and test. The Joomla docs warn that disabling it on production can fatal old extensions, and that you may need the database to turn it back on.
    • If you are preparing Joomla 6, this plugin must be disabled before that upgrade, and you need extensions that do not rely on it. That is an upgrade project, not this article.

    This is one checkbox in the “installed but dead” list. It is not a substitute for a vendor’s Joomla 5 build. Prefer an updated extension. Do not treat the compat plugin as a permanent architecture.

    Joomla 5.4 also installs Behaviour – Backward Compatibility 6 for the later jump. Do not disable that in a way the Joomla 6 migration guide forbids. Read Compatibility plugins (5.4 to 6) when you upgrade. For “not working today on Joomla 5,” the plg_behaviour_compat enable check is enough.

    Step 7: Create the menu item (missing menu type)

    A component can install a menu item type (Articles → Archived Articles is the core example). Your add-on is the same. Until you create Menus → your menu → New and select that type, the site has no URL.

    Symptoms:

    • Administrator component works. Frontend 404 or Home never changes.
    • You look for a module. The feature is a component view, not a module.
    • The type is missing from the New Menu Item list: the component is disabled, Discover never ran, or the XML submenu / menu section failed. Reinstall or Discover. Confirm the component is enabled in Manage Extensions.

    Create the menu item, set Access, set a template style if needed, save. Open that URL. Do not expect the installer to inject a menu item on a production menu. Many packages do not.

    If the type appears but the view is empty, you may still need to create records inside the component (a first category, a first item). That is configuration, not a failed install.

    Step 8: Create and publish the module

    System → Site Modules → New. If the module type is in the list, the module type is installed. A type in the list is not an instance on the page.

    Packages often do not create a published module. You must:

    1. New → pick the type.
    2. Set Position to a name the template actually prints (position not showing if the slot is empty everywhere).
    3. Menu Assignment (wrong pages if it appears in the wrong place).
    4. Publish. Public access. Language All or the right language.

    If the type is not in New Module, the module file never installed (package incomplete, or you only installed the component zip). Install the full package. Discover if you dropped modules/mod_example by hand.

    Editor buttons (editors-xtd) are plugins, not modules. Enable them under Plugins. They will not appear as Site Modules.

    Language, ACL, and cache (short)

    • Install the extension’s language pack if the vendor ships one, or you will see KEY_NAMES as titles. For core string tweaks, language overrides.
    • Super User sees a module a Guest does not: Access.
    • Clear cache after enable. Page cache can hide a module you just published.

    Custom fields inside an extension are not core article fields. Core article fields have their own empty-frontend guide: custom fields not showing.

    Warnings, update sites, and a second install attempt

    System → Manage → Warnings (or Installer warnings) lists environment problems Joomla already detected: PHP version, missing modules, memory. If a warning names the same constraint the vendor lists, fix the host before you reinstall the zip. Reinstalling will not add intl.

    System → Update → Update Sites (or Manage → Update Sites): if the extension installed from a URL and later “does nothing” after you expected a patch, Rebuild the update sites, then System → Update → Extensions. An old build that “installed fine” on Joomla 5 can still be a Joomla 4 package. The update site is how you learn a Joomla 5 zip exists.

    If you install twice, Joomla may refuse or may leave the first schema in place. Prefer Uninstall (after a backup) then install the matching Joomla 5 package, over copying folders on top of a half Discover. Uninstall removes #__extensions rows. It can drop the extension’s tables. That is why the backup exists.

    A library or file package can install with no admin menu. The feature then lives inside another component. Read the vendor’s “where to click after install” once. Searching Site Modules for a library is a dead end.

    Checks: Manage row, Discover, enable, schema, PHP, menu, module instance

    Files and a green installer are the start. Enable, schema, PHP, menu type, and a published module instance are the rest.

    Key takeaways

    1. Installer success means a registry row. It does not mean enabled, schema-current, or on a menu.
    2. Discover registers FTP-copied files. Enable turns plugins on. They are different buttons.
    3. Packages hide a disabled system plugin. Search Plugins after every component install.
    4. Maintenance → Database → Update Structure when files and SQL diverged.
    5. Check PHP version and System Information warnings before you blame Joomla.
    6. On Joomla 5, confirm Behaviour – Backward Compatibility if the add-on is old. Prefer a native Joomla 5 build. This is one check, not a strategy.
    7. Components need a menu item type you create. Modules need a New instance, position, and assignment.
    8. If it 500s, leave this checklist and read the log. If it works alone and fails with a neighbour, that is a conflict.

    When a vendor package is registered but the live site still has no menu, no module, and no plugin enabled, a maintainer can finish the wiring: Joomla support and maintenance.

    Frequently asked questions

    Why is my Joomla extension installed but not working?

    The zip registered files, but a plugin is still disabled, Discover was skipped after an FTP copy, the schema is behind, PHP does not match, or you never created a menu item or module instance.

    What is the difference between Discover and Enable?

    Discover finds manifests on disk and creates #__extensions rows (then you click Install on that screen). Enable turns an existing row on. Uploading a zip uses Install Extensions, not Discover.

    Do I always get a module on the page after install?

    No. You often get a module type. You still click Site Modules → New, publish it, and assign a position and pages.

    Why is there no menu item type for my component?

    The component is disabled, not fully discovered, or you are looking at the wrong client (site vs administrator). Enable the component, run Discover if files were copied, reinstall the package, then Menus → New.

    Should I disable the Joomla 5 compatibility plugin to test?

    Only on staging, and only if you can re-enable it in the database when admin dies. For an old extension that is “not working,” try enabling the plugin first. Plan a real Joomla 5 build before Joomla 6.

    Update Structure did nothing. Now what?

    Confirm you selected the extension that listed errors. If SQL still fails, restore a backup and reinstall on staging. Do not drop random tables on production.

    Could this be a template problem?

    Yes, if it is a module in a position the template does not print, or an override that errors. Check position names and child-template overrides after the extension is enabled and assigned.

  • PHP2Shell (CVE-2026-109618/109619): How to Patch Joomla & WordPress Sites

    PHP2Shell (CVE-2026-109618/109619): How to Patch Joomla & WordPress Sites

    Last updated Oct 21, 2026. We will update this guide as hosts and Linux vendors ship fixed packages.

    Short answer: PHP2Shell is the name for two critical flaws in PHP itself, CVE-2026-109618 and CVE-2026-109619. Both are rated CVSS v4.0 9.2 and can let an attacker run code on your server without logging in. The only complete fix is to run PHP 8.2.35, 8.3.36, 8.4.27 or 8.5.12 or newer, released on 21 October 2026 (php.net advisory). Nothing in Joomla or WordPress fixes it, and no plugin or extension does either. If your site runs PHP 8.1 or older, there is no official fixed release: you need to move to PHP 8.3 or later, or get a patched package from your Linux vendor.

    The fix in five steps: 1) find the PHP version your site actually serves, 2) get it onto a fixed build, 3) confirm the fix is really running, 4) add the interim hardening if you are still waiting, 5) plan an exit if your host will not move. Each step has its own section below, with steps for cPanel, Plesk, CloudLinux, VPS servers, Joomla 4, 5 and 6.2, and WordPress.

    What is PHP2Shell, in plain English?

    PHP is the engine that runs Joomla and WordPress. Every page of your site, from the home page to the admin login, is built by PHP on your web server. PHP is installed by your hosting company, not by you and not by your CMS.

    PHP2Shell is a fault in that engine. A stranger can send your server one specially crafted web request, just like a normal visit but built to trigger the fault. The server can then run the stranger’s commands. No password is needed and no account is needed.

    Because the fault sits in PHP, it hits before Joomla or WordPress even starts. Your admin password, two-factor login, security plugin or Joomla access rules never get a say. php.net confirms there is a working attack that triggers before any application code runs on the most common Apache setup.

    An analogy: your Joomla or WordPress security is the lock on your apartment door. PHP2Shell is a broken lock on the building’s front door, and it opens the service corridor behind every apartment. A better apartment lock does not help. The building manager, your host, has to replace the front-door lock, which here means installing the fixed PHP release.

    What can happen to your site if you ignore it?

    Running commands on your server means an attacker can do roughly what your site itself can do. These are the usual results of that kind of access on any hacked site, not specific reported PHP2Shell cases:

    • Defacement. Your pages are replaced or altered with the attacker’s content.
    • Hidden malware or spam. Code is slipped into your files or database that redirects visitors, shows spam links or infects visitors’ browsers.
    • Stolen data. The site can read its own database, so customer details, orders, contact form submissions and user accounts can be copied.
    • Your server attacks others. The site is used to send spam email, host phishing pages or attack other websites, often without you noticing.
    • Google warnings and lost rankings. Google may label the site This site may be hacked in search results or show a red browser warning, and visitors and rankings drop while that lasts. See Google’s Security Issues report help.
    • Hosting suspension. Hosts commonly suspend accounts that send spam or host malware, which takes the whole site offline.
    • Cleanup cost and downtime. Removing malware, restoring backups, resetting every password and asking Google for a review takes time and money, and data that was stolen cannot be taken back.

    If you sell online, handle bookings or collect personal data, a breach can also bring legal duties to report it to customers or regulators, depending on where you and they are.

    Which PHP versions are safe, and which are not?

    Check the first two numbers of your PHP version (the branch), then the last number (the patch level). Versions are from the PHP 8 changelog, the CERT-FR alert and NVD; support dates are from php.net’s supported versions and end-of-life pages.

    Your PHP branchVulnerableFixed inBranch support (php.net)What you do
    8.58.5.11 and below8.5.12Active support to 31 Dec 2027Update to 8.5.12
    8.48.4.26 and below8.4.27Active support to 31 Dec 2026, security to 31 Dec 2028Update to 8.4.27
    8.38.3.35 and below8.3.36Security fixes only, to 31 Dec 2027Update to 8.3.36
    8.28.2.34 and below8.2.35Security fixes only, ends 31 Dec 2026Update to 8.2.35, then plan 8.3+
    8.1AllNo official releaseEnd of life since 31 Dec 2025Move to 8.3+ or use a vendor backport
    8.0, 7.x, 5.xAllNo official releaseEnd of lifeMove to a supported branch
    8.6 release candidatesNot covered by the fixed releasesNone yetTesting only, not for productionDo not run in production

    The PHP team also published minimal source-only patches for 7.4, 8.0 and 8.1 for people who compile PHP themselves. They are not releases, and a shared hosting panel cannot offer them.

    Still on Joomla 3? Why patching PHP is not an option

    This is the hardest case, and it is worth being precise about. Joomla’s official technical requirements list PHP 8.0 as the recommended version for Joomla 3.x, and no newer PHP version is listed. Joomla 3 support ended on 17 August 2023, and the extended LTS version ended on 17 February 2025, so Joomla 3 gets no more updates to make it work on newer PHP. Joomla volunteers on the official Joomla forum report that 3.10 does not work on PHP 8.2 or later and is unreliable on 8.1. Every branch that received the PHP2Shell fix is 8.2 or newer. Put those facts together and no officially supported Joomla 3 setup can run a patched PHP release.

    What about the stopgaps? Each one helps a little and costs something:

    OptionWhat it gets youWhere it falls short
    Source-only backports for 7.4, 8.0, 8.1The PHP2Shell fix for people who compile PHP themselvesNo releases and no binaries. Shared, reseller and most managed hosts cannot install them, and you take on maintaining a custom PHP build.
    Vendor or distribution backport (for example a Linux LTS package)A patched PHP 8.0 or 8.1 from a vendorOnly on servers you or your host control at the OS level, often paid, and only covers PHP. Joomla 3 itself still gets no security fixes.
    Interim php.ini settings and a WAFFewer known attack pathsphp.net says they do not make an installation safe, and WAF rules can be bypassed by direct-to-origin traffic.
    Forcing Joomla 3 onto PHP 8.2+A patched PHPUnsupported: expect white pages, 500 errors and broken extensions, which is why hosts that move clients forward often break Joomla 3 sites.

    So the risk of staying is not only PHP2Shell. It is that every future PHP or Joomla vulnerability lands on a site with no supported fix. The lasting fix is to move the site to Joomla 6.2, which requires PHP 8.3 or newer, so it runs on a branch that gets security releases until at least the end of 2027. Joomla does not allow skipping straight from 3 to 6: the path is 3.10 → 4.4 → 5.x → 6.x, and our Joomla 3 to 6 upgrade guide walks through each hop. Run the free Joomla 6 compatibility check first to see which extensions have Joomla 6 versions and which need replacing; that list is what decides how long the move takes. If you would rather have the migration done for you, that is what our Joomla upgrade service covers.

    Old WordPress on PHP 7.4 or 8.1? WordPress is gentler: current WordPress still runs on PHP 7.4 but recommends 8.3 or greater. Update WordPress core, plugins and themes first, then switch the branch as in Step 2b. Plugins abandoned by their authors are the usual blocker, so replace them before the switch.

    How do the two flaws work?

    Both flaws are about what PHP leaves behind when a web request ends badly. According to the NVD descriptions supplied by the PHP security team:

    • CVE-2026-109618: when PHP runs out of memory mid-request, some internal request memory can be left uninitialised. The cleanup step then reads it as if it were valid, and several out-of-memory tricks can turn that into remote code execution.
    • CVE-2026-109619: some global state can keep pointing at request memory after it has been freed. A later request on the same PHP worker can read that stale state before it is reset, which can also lead to remote code execution.

    php.net says the risk covers all PHP installations serving web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed, and is highest for mod_php, where a demonstrated exploit runs before any application code. For a Joomla or WordPress site this means your login page, security extension and file permissions are not in the way: the attack happens one layer below the CMS.

    FactDetailSource
    CVSS v4.0 score9.2 for both CVEs (vector AV:N/AC:H/AT:P/PR:N/UI:N)NVD
    Advance notice20 Oct 2026, release set for 21 Oct 14:00 UTC (7:30 PM IST)php.net
    Fixed releases8.5.12, 8.4.27, 8.3.36, 8.2.35 on 21 Oct 2026php.net
    Changelog entry“Fixed GHSA-w8hw-w9fx-j79w, GHSA-6wmf-4rv5-p3rp (Avoid state corruption via bailout)” in all four branchesPHP changelog
    NVD publication21 Oct 2026, 14:17 UTC (7:47 PM IST), status “Received”NVD
    CISA assessmentOn 21 Oct, CISA’s SSVC entry on NVD rated exploitation as “none” and technical impact as “total”; NVD status is still “Received” (not yet analysed)NVD
    Attack trafficCloudflare says it observed attack traffic after the CVE details leakedCloudflare

    Step 1: How do I check which PHP version my site really runs?

    Check the version the web server uses for your site. The command-line php -v on the same server can be a different build, so do not rely on it alone.

    In Joomla 4, 5 or 6.2

    Log in to the Administrator, open System → System Information, and read PHP Version on the System Information tab. The PHP Information tab shows the full phpinfo output, including the Server API line (for example FPM/FastCGI or Apache 2.0 Handler), which tells you whether you are on the higher-risk mod_php.

    In WordPress

    Go to Tools → Site Health → Info and expand Server. The PHP version and Server API rows are listed there (WordPress Site Health docs).

    With no admin access

    Upload a one-line file, open it in the browser, note the version, and delete it immediately, because phpinfo output helps attackers:

    <?php echo PHP_VERSION, " ", PHP_SAPI;

    Name it something random (not info.php). It prints the exact version and the server API, for example 8.3.36 fpm-fcgi. PHP manual: phpversion()

    Checking many sites

    Repeat the same check per site, because one hosting account can run different PHP branches per domain. Record domain, branch, patch level and Server API in a sheet, and sort by the table above.

    Step 2: How do I update PHP to a fixed version?

    Two different things are called “updating PHP”. A patch update (8.3.35 to 8.3.36) is a drop-in security fix that your host installs on the server. A branch change (8.1 to 8.3) is something you usually select yourself and must test, because extensions and plugins can break. PHP2Shell needs the patch update everywhere, and a branch change if you are on 8.1 or older.

    cPanel (shared hosting)

    1. Open Software → MultiPHP Manager (cPanel docs), or Select PHP Version on CloudLinux servers.
    2. Check which branch your domain uses. The selector picks a branch; the patch level inside it is whatever the host has installed.
    3. If you are on 8.1 or older, take a backup, then pick 8.3 or newer and test the site (see Step 2b).
    4. Run the Step 1 check again. If the patch level is still below the fixed build, open a ticket (template in Step 5).

    Server admins with WHM install the fixed EasyApache 4 packages through the normal system update and manage versions in MultiPHP Manager for WHM.

    Plesk

    In Plesk, open the domain, then PHP (PHP Settings), and choose the PHP version. Plesk’s own advisory (updated 21 Oct 2026, 15:13 UTC / 8:43 PM IST) lists the state of its PHP builds:

    Plesk PHPLinuxWindows
    8.2Fixed in 8.2.35In development
    8.3Fixed in 8.3.36In development
    8.4Fixed in 8.4.27In development
    8.5Fixed in 8.5.12In development
    7.4, 8.0, 8.1In developmentIn development

    To see which builds a Plesk server has, go to Tools & Settings → PHP Settings; the version is part of each handler name. On Linux over SSH, /opt/plesk/php/8.3/bin/php -v shows it (swap 8.3 for your branch).

    Plesk also lists its own panel engine (sw-engine) as affected on all versions, with hotfixes planned as 18.0.80#11 and 18.0.81#4. If you run Plesk on Windows, use the interim hardening in Step 4 until the builds ship, and keep checking Plesk’s advisory.

    CloudLinux, LiteSpeed and other managed hosts

    On CloudLinux, the per-site PHP selector uses CloudLinux’s own alt-php builds, so the patch arrives when CloudLinux ships it and your host installs it. LiteSpeed is named in php.net’s list of affected setups. On managed WordPress and Joomla hosts with no PHP setting, the host alone controls the patch: ask for the exact version and date (Step 5).

    Your own VPS or dedicated server

    • Distribution packages (Ubuntu, Debian, RHEL and clones): install the vendor security update with your normal package manager. Distributions often backport security fixes without changing the upstream version number, so confirm with the vendor’s security notice for these CVE IDs, not by version string alone.
    • Third-party repositories or source builds: upgrade to the fixed upstream release from php.net downloads or your repository once it publishes the build.
    • Docker images: pull an image built on the fixed release, rebuild, and redeploy every container; a running container never patches itself.
    • Then restart PHP (Step 3). Without a restart the old code keeps serving requests.

    Step 2b: Moving off PHP 8.1 or older without breaking the site

    CMS versionPHP minimumPHP recommendedCan it reach a fixed branch?
    Joomla 6.x (incl. 6.2)8.3.08.4Yes, every supported setup is 8.3+ (Joomla docs)
    Joomla 5.x8.1.08.3Yes, move to 8.3 (Joomla docs)
    Joomla 4.x7.2.58.2Yes on 8.2, but upgrade Joomla too (Joomla docs)
    Joomla 3.x5.3.108.0 (highest listed)No; see the Joomla 3 section below (Joomla docs)
    WordPress (current)7.4 (legacy)8.3 or greaterYes (WordPress requirements)
    1. Back up files and database first (how to back up Joomla).
    2. Update the CMS core, then every extension, plugin and theme, on the old PHP version.
    3. For Joomla, scan extensions for compatibility with our free Joomla 6 compatibility check.
    4. Switch the branch on a staging copy if you have one, or during a quiet hour on live.
    5. Test front end, forms, checkout, login and admin. If you get a white page or 500 error, switch back and use this guide to find the failing extension.
    6. Still on Joomla 3? PHP cannot move until Joomla does; see the Joomla 3 section.

    Step 3: How do I confirm the patch is actually live?

    1. Repeat the Step 1 check through the website (Joomla System Information, WordPress Site Health or the one-line file). The version must be 8.2.35, 8.3.36, 8.4.27, 8.5.12 or higher, or a vendor package your vendor confirms fixes both CVEs.
    2. On a server, restart every PHP process: restart PHP-FPM pools, and for mod_php restart Apache fully. php.net’s advisory tells admins to restart every worker for settings to apply; the same applies to new binaries.
    3. Check that no process still uses the old library. On Linux this should print nothing:
    grep -lE ' /(usr|lib|opt).*\(deleted\)$' /proc/[0-9]*/maps 2>/dev/null

    Then check every site on the account, not just the main one; add-on domains can run different branches.

    Step 4: What can I do while I wait for my host?

    php.net lists interim measures that reduce exposure to specific attack paths but, in its words, do not make an installation safe. They must be set in php.ini, the PHP-FPM pool or the web server config, which apply before the request is parsed. php.net says not to rely on ini_set() or FPM .user.ini.

    SettingTargetsNotes from php.net
    session.upload_progress.enabled=0CVE-2026-109619Blocks the confirmed session paths, not other variants. Neither Joomla nor WordPress core needs it.
    fatal_error_backtraces=0 (PHP 8.5 only)CVE-2026-109619Blocks the confirmed fatal backtrace path only.
    memory_limit=-1 set with php_admin_valueCVE-2026-109618Removes the controllable memory-limit failure; use a container or cgroup limit instead, not RLIMIT_AS or RLIMIT_DATA.
    post_max_size = 8M (no uploads) or 32M (uploads), upload_max_filesize lowerCVE-2026-109618Also cap request size, field count, multipart parts, headers and nesting at the web server or proxy.
    Remove invalid or deprecated per-request settings (for example in .htaccess)CVE-2026-109619Hiding errors with display_errors or error_reporting does not help.

    A Joomla site with large media uploads or a WordPress shop importing big CSV files may need the 32M limit. Our Joomla .htaccess guide shows where per-directory PHP settings live, so you can find and remove deprecated php_value lines.

    Does Cloudflare or a WAF protect me?

    Partly. Cloudflare says customers using its free or paid WAF have been protected by default against known PHP2Shell attacks since 21 Oct 2026, 03:02 UTC (8:32 AM IST), and still tells customers to patch PHP (Cloudflare blog). A WAF only helps if attackers cannot reach your server directly by IP, so restrict the origin to Cloudflare’s IP ranges. Treat any WAF rule as a stopgap.

    Step 5: What if my host will not update PHP?

    Send a short ticket that leaves no room for a vague answer:

    Subject: PHP2Shell (CVE-2026-109618 / CVE-2026-109619) patch date
    
    Hi, my site [domain] runs PHP [version]. PHP released 8.2.35, 8.3.36,
    8.4.27 and 8.5.12 on 21 October 2026 to fix two unauthenticated remote
    code execution flaws (https://www.php.net/). Please confirm:
    1. the date the fixed build will be installed for my account, and
    2. if you use vendor-backported packages, the package version that
       includes both fixes.
    If my branch (8.1 or older) will not be patched, which supported
    branch can I switch to today?
    Thanks.

    If the host cannot give a date, or only offers PHP 8.1 or older, that is a reason to move. Until then, put the site behind a WAF with the origin locked down, apply what Step 4 allows on your plan, and keep fresh offsite backups. CERT-FR’s advice for unsupported versions is to isolate affected systems and migrate to a maintained version (CERT-FR), and BleepingComputer reports that the UK NCSC told organisations to update or take systems offline until patched (BleepingComputer).

    Step 6: How do I know if my site was already attacked?

    The flaws allow code execution as the web server user, so look for what an attacker would leave behind:

    • New or changed PHP files in upload, cache, images or tmp folders, especially since 20 Oct 2026.
    • Unknown administrator or Super User accounts.
    • Unusual POST requests, very large multipart uploads, or bursts of 500 errors in the access and error logs around 20 and 21 October.
    • Unexpected cron jobs, outbound connections or spam sent from the server.

    If you find any of these, patching alone is not enough. Follow our hacked Joomla incident-response guide or our WordPress malware removal service, and rotate database, FTP, admin and API passwords afterwards. For ongoing hardening see the Joomla security guide.

    PHP2Shell checklist

    Done?Task
    ☐Recorded PHP version and Server API for every site
    ☐Every site on 8.2.35, 8.3.36, 8.4.27, 8.5.12 or a vendor-confirmed backport
    ☐PHP-FPM / Apache restarted, no deleted libraries in use
    ☐Sites on 8.1 or older scheduled for a branch change
    ☐Interim settings applied where still unpatched
    ☐Logs and files checked for signs of compromise
    ☐Host ticket answered with a patch date

    The short version

    Find the PHP version every site really serves, get it onto 8.2.35, 8.3.36, 8.4.27 or 8.5.12, restart PHP and check again. Use the interim settings only while you wait, and chase your host for a date. If a site is on Joomla 3 or PHP 8.1 and older, the patch you need is a version upgrade, and the sooner it is planned the less any future PHP flaw matters. If you want a second pair of hands, Infyways has worked on Joomla sites since 2010 and replies to enquiries within 12 hours; you can reach us here.

    Frequently asked questions

    What does PHP2Shell mean for a non-technical site owner?

    PHP, the engine that runs Joomla and WordPress, has a fault that lets a stranger run commands on your server without logging in. Ask your host to confirm your site runs PHP 8.2.35, 8.3.36, 8.4.27, 8.5.12 or newer.

    Can I patch PHP2Shell on a Joomla 3 site?

    Not on a supported setup. Every fixed PHP release is 8.2 or newer, and Joomla 3.10 does not run on PHP 8.2+. Vendor backports and php.ini settings reduce risk only partly, so the lasting fix is upgrading to Joomla 6.2 via 4.4 and 5.x.

    What is PHP2Shell?

    PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, two critical flaws in the PHP runtime rated CVSS v4.0 9.2. They can allow unauthenticated remote code execution on servers that serve web requests with PHP.

    Which PHP versions fix PHP2Shell?

    PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12, released on 21 October 2026. PHP 8.1 and older get no official release.

    Do I need to update Joomla or WordPress?

    No CMS update fixes PHP2Shell, because the flaw is in PHP. Keep the CMS updated anyway, especially if you need to move to a newer PHP branch.

    Will a security plugin or extension protect my site?

    No. php.net describes a demonstrated exploit that triggers before any application code runs, so CMS security plugins and extensions never see it.

    Is PHP 8.1 safe if my host says it is patched?

    Only if the host uses a vendor package that backports both fixes, and can name it. The PHP project itself published no fixed 8.1 release.

    Which PHP version should a Joomla 6.2 site use?

    Joomla 6 requires PHP 8.3 and recommends 8.4. Use 8.4.27 or 8.3.36 or newer.

    Which PHP version should WordPress use?

    WordPress recommends PHP 8.3 or greater. On 8.3, use 8.3.36 or newer.

    Can I set the PHP2Shell mitigations in .user.ini?

    No. php.net says not to rely on ini_set() or FPM .user.ini; use php.ini, the FPM pool or server configuration, then restart every worker.

    Is Cloudflare enough to protect my site?

    No. Cloudflare deployed WAF rules on all plans but still tells customers to patch, and a WAF does nothing for traffic sent straight to your server IP.

  • How to Find Which Joomla Extension Is Causing a 500 Error

    How to Find Which Joomla Extension Is Causing a 500 Error

    A Joomla 500 error means PHP or the web server aborted the request. The extension name is in the log, not in the generic “Whoops” page. Read error_log (and Joomla’s log folder), turn Debug on from Global Configuration or configuration.php, then isolate the last update. On a staging copy only, you can temporarily rename a plugin folder to prove the group. Never delete production files without a backup, and never “clean up” live plugins to find a 500.

    The browser message is empty on purpose. Production hides fatals. Your job is to make the fatal visible in a log, then disable one extension, not the whole site.

    500 page with no name, error_log line pointing at plugins/system

    The HTML is a dead end. The PHP error log is the map. The path under plugins, modules, or components is the extension.

    What you will learn

    • Where hosts put error_log and where Joomla writes administrator/logs
    • How to enable Debug and Maximum error reporting when the admin still opens
    • How to set $debug and $error_reporting in configuration.php when admin does not
    • Why the last update is the first extension to disable
    • How to rename a plugins folder on staging only as a group test
    • How to disable one row in #__extensions without deleting files
    • What not to do on production

    Official: Fatal error (Joomla User Manual). If the site runs but two add-ons fight, use Joomla extension conflict instead of this 500 path.

    500 vs white screen vs “Whoops”

    Joomla 4 and 5 often show a page titled like Whoops, looks like something went wrong with an HTTP 500 status. That is still a server 500. A white screen is the same class of failure with display_errors off.

    Source What it is good for
    PHP error_log (host panel, or a file in the account) Fatals that happen before Joomla’s pretty error page
    Web server error log (Apache/nginx) .htaccess, PHP-FPM socket, permissions
    administrator/logs/ (or the path in Global Configuration) Joomla Log::add and some extension logs, not every fatal
    Debug System + Error Reporting Maximum Stack trace after Joomla has bootstrapped
    Browser Network tab Confirms 500 vs 403 vs timeout. Does not name the PHP file

    If the log line is .htaccess or mod_security, you may not have an extension problem. Fix the server rule, then come back if PHP still fatals.

    Step 1: Copy the site, then backup production anyway

    Before any rename, disable, or configuration.php edit on a live site:

    1. Snapshot or copy files and the database (host backup, or your own). If you cannot restore, do not experiment on production.
    2. Prefer a staging URL with the same Joomla and PHP versions. Do the hunt there. Deploy the known-good disable back to production.
    3. Tell the team the site may be briefly noisy if you enable Maximum error reporting on production.

    Do not delete the plugins directory on production “to see what happens.” You will take down authentication, two-factor, and SEF. You may not get admin back without a restore.

    If you need someone else to hold the copy and the log hunt: Joomla support and maintenance.

    Step 2: Read error_log before you click around

    Ask the host where PHP logs. Common places:

    • cPanel Errors or Metrics → Errors
    • Plesk PHP log
    • A file named error_log in public_html or in the account home
    • ~/logs/error.log on some VPS stacks

    Open the log at the timestamp of your test request. One line of PHP Fatal error is worth an hour of plugin guessing.

    Copy:

    • The exception class (Error, TypeError, ParseError)
    • The file path and line
    • The first few frames of the stack if present

    Map the path:

    • plugins/system/example/ → System plugin “example”
    • plugins/content/example/ → Content plugin
    • modules/mod_example/ → that module (unpublish it in Site Modules once admin works)
    • components/com_example/ → that component
    • templates/cassiopeia/ or a child → template PHP, often an override. See customize without editing core after the site is up.
    • libraries/ → core or a library package. Do not delete libraries. Restore a backup or revert the last Joomla update.

    Joomla also logs under Global Configuration → System → Path to Log Folder (default administrator/logs). Check everything.php or dated files if the host PHP log is empty. Many fatals never reach Joomla’s logger because PHP died first. That is why error_log is step 2, not step 5.

    Step 3: Debug from Global Configuration, or from configuration.php

    If administrator still loads:

    1. System → Global Configuration.
    2. System tab: Debug System = Yes.
    3. Server tab: Error Reporting = Maximum.
    4. Save. Reload the failing site URL once (and the admin URL if that is what 500s).
    5. Read the on-screen file and line. Then set Debug = No and Error Reporting = System Default. Save.

    The Debug console is configured by System – Debug. Allowed Groups can hide the console from guests. You still want Maximum reporting for the fatal text.

    If administrator is a 500 too, do not keep hitting login. Use FTP or the host file manager:

    1. Download configuration.php. Keep a copy.
    2. If the file is 444, set it to 644 long enough to edit (the manual describes this).
    3. Set public $debug = true;
    4. Set public $error_reporting = 'maximum';
    5. Save. Reload once.
    6. Put $debug back to false and $error_reporting back to 'default' or 'none' (match what you had) as soon as you have the path. Leaving Maximum on production leaks paths to visitors.

    Official steps: Fatal error.

    Optional: rename the template’s error.php on staging if that file is itself fataling and hiding the real message. Do that only on the copy.

    Step 4: Disable the last update first

    System → Update → Extensions (if admin works) or your change log:

    • Last extension update
    • Last Joomla update
    • Last PHP version change on the host (this 500s old extensions without a zip install)

    Disable in this order once you have a path, or if the log is empty but the clock matches an update:

    1. The extension named in the log.
    2. If the log names a plugin, disable that plugin in System → Plugins (or #__extensions below).
    3. If admin is down, you cannot click Plugins. Use the database: table #__extensions (your prefix), find element matching the plugin name, set enabled to 0. The user manual describes this for a faulty extension. Do not set core rows to 0 unless you know the row.
    4. If the last change was a component update, disable its plugins first (packages register several rows). Then take the component off the default menu item so it is not the Home view.

    Clear cache files on disk if page cache is on (cache/ folder) after a disable. A cached 500 is rare. A cached blank HTML is less rare. Still worth deleting cache/ on staging.

    Step 5: Staging only, rename a plugins folder to test a group

    This is a group proof, not a production technique.

    On staging:

    1. Confirm you can restore (snapshot, or a zip of plugins/ you just made).
    2. Rename one third-party plugin directory, for example plugins/system/suspect → plugins/system/suspect.off. Joomla will skip that folder. Core plugins stay.
    3. Reload. If the 500 is gone, that folder was in the path (or something it triggered was).
    4. Rename it back. Disable the plugin properly in the database or UI so the site does not fatal on the next page that autoloads it in a different way.

    You can rename a group folder on staging in an emergency, for example plugins/system → plugins/system.off, to see whether any system plugin is involved. That will break a lot of features. It is a binary test on a copy, then you put the folder name back immediately and disable one plugin at a time.

    Do not do this on production. Do not delete the folder. Do not rename plugins as a whole on a live shop. You will remove authentication plugins and lock everyone out. If you already did that on production, restore the backup from Step 1. Do not invent a “fix” by uploading empty directories.

    If you need a batch disable with the UI still up, that is the conflict article’s plugin batches, not a filesystem delete.

    Step 6: Database disable when the UI is dead

    phpMyAdmin or an SQL client, on a backup first:

    • Table: {prefix}_extensions
    • Find the row: type = plugin, element = the plugin name, folder = system/content/…
    • Set enabled = 0

    For a module, you can also unpublish in {prefix}_modules (published = 0) if the log named mod_….

    For a component Home page that 500s, change the default menu item in {prefix}_menu to a core featured or article view, or disable the component’s plugins, rather than DROP TABLE. Deleting tables is how you turn a 500 into a restore.

    When admin returns, uninstall or roll back the extension with System → Manage → Extensions if you are done with it. Uninstall is not the same as deleting folders by hand. The installer cleans #__extensions rows.

    Memory, timeouts, and logs that name PHP, not an extension

    Some 500s never mention plugins/. They still belong to an extension.

    • Allowed memory size exhausted at a line in plugins/system/example/ is that plugin (or a loop it triggered). Raise memory_limit only on staging to confirm. On production, fix the plugin or the data set it loads (a module that queries every article is a typical case).
    • Maximum execution time exceeded in a component view is that component, or a plugin that runs on that view. Do not raise max_execution_time as the only fix.
    • PHP Parse error in an override under templates/…/html/ is your copy, not the vendor zip. Restore the core layout on staging, then repair the override in a child.

    .htaccess 500s often follow a security plugin that wrote rewrite rules, or a hand edit after an extension installer. On staging, temporarily rename .htaccess to .htaccess.bak and use Joomla’s default htaccess.txt copied to .htaccess. If the 500 vanishes, the rules were the problem. Put your custom rules back one block at a time. Do that on production only after a backup, and only if you can restore via the host panel when you lock yourself out.

    Gzip in Global Configuration plus Maximum error reporting can produce odd output on some hosts. If Debug shows a fatal and the browser still shows a generic 500, disable Gzip for the test. Turn it back on later.

    After the site loads, close the hole

    1. Set $debug false and error reporting off/default.
    2. Set Preview and Debug plugins back to normal groups.
    3. Update or replace the extension. If it needs old class names on Joomla 5, that is a compatibility check on the installed but not working article, not a reason to leave Debug on.
    4. If a plugin tmpl was the fatal (parse error in an override), fix the override in a child. Plugin override.
    5. Write the extension name and version in your runbook so the next 500 is shorter.

    Checks: backup, error_log path, debug, last update, staging rename only

    Log first. Last update second. Rename plugin folders only on staging. Never delete live files to “test.”

    Key takeaways

    1. A Joomla 500 is a server abort. The extension is named in error_log (or a Debug stack), not in the Whoops HTML.
    2. Copy the site or take a full backup before you change configuration.php or plugin folders on anything you care about.
    3. Enable Debug and Maximum error reporting only for the reproduce, then turn them off.
    4. Disable the last updated extension first when the clock matches and the log agrees.
    5. Rename plugin folders only on staging, as a temporary proof. Put the names back. Disable via Plugins or #__extensions.
    6. Never delete production plugins/, components/, or libraries/ to debug. Restore from backup if you already did.
    7. Database enabled = 0 on one extension row is the safe UI-down move. Dropping tables is not.
    8. When two extensions work alone and 500 together, finish recovery then use the conflict process.

    Frequently asked questions

    How do I find which Joomla extension is causing a 500 error?

    Read the PHP error_log at the request time. The file path under plugins/, modules/, or components/ is the extension. Enable Debug if Joomla still bootstraps. Then disable that extension, starting with the last update if the log is empty.

    Can I rename the plugins folder on the live site?

    No. Use staging. On production, take a backup and disable one #__extensions row, or restore. Renaming plugins on live removes authentication and can lock out admin.

    Admin is a 500. How do I turn on debug?

    Edit configuration.php: $debug = true and $error_reporting = 'maximum'. Reload once, copy the error, then turn both back off. The user manual documents the permission change if the file is read-only.

    The error_log is empty. What next?

    Check the web server log, Joomla’s log path, and whether you are looking at the right vhost. Enable Maximum reporting on staging. If PHP dies before logging, ask the host for the FPM log.

    Should I delete the extension files to stop the 500?

    No. Disable it. Deleting files on production without a backup is how you lose the only copy of a paid extension and still leave broken #__extensions rows. Restore, then uninstall from the administrator when it loads.

    Could PHP be the “extension”?

    A host PHP upgrade can fatal old extensions. The log still names the extension file. The fix is an update of that extension, or rolling PHP back on staging to prove it.

    When is a 500 not an extension?

    Disk full, bad database credentials in configuration.php, a broken .htaccess, or a core update that failed mid-way. The log still decides. If it names libraries/ after a Joomla update, restore the update backup, do not delete libraries.